Quotulatiousness

April 27, 2011

High computer use linked to “smoking, drunkenness, non-use of seatbelts, cannabis and illicit drug use, and unprotected sex”

Filed under: Cancon, Health, Media, Technology — Tags: , , , — Nicholas @ 07:20

Talk about upsetting the stereotype of basement dwelling, dateless nerds:

The revelations come in research conducted lately in Canada among 10 to 16-year-olds by epidemiology PhD candidate Valerie Carson.

“This research is based on social cognitive theory, which suggests that seeing people engaged in a behaviour is a way of learning that behaviour,” explains Carson. “Since adolescents are exposed to considerable screen time — over 4.5 hours on average each day — they’re constantly seeing images of behaviours they can then potentially adopt.”

Apparently the study found that high computer use was associated with approximately 50 per cent increased engagement with “smoking, drunkenness, non-use of seatbelts, cannabis and illicit drug use, and unprotected sex”. High television use was also associated with a modestly increased engagement in these activities.

According to Ms Carson this is because TV is much more effectively controlled and censored in order to prevent impressionable youths seeing people puffing tabs or jazz cigarettes while indulging in unprotected sex etc. The driving without seatbelts thing seems a bit odd until one reflects that old episodes of the The Professionals, the Rockford Files etc are no doubt torrent favourites.

April 23, 2011

A neat way to address software piracy

Filed under: Gaming, Humour, Technology — Tags: , , , — Nicholas @ 12:52

I still find it hard to believe that Cracked, of all the media entities from the pre-internet era, is worth visiting (and linking to). However, this is good stuff:

The [Arkham Asylum] developers included a little bit of extra code to detect when the game has been pirated, a common tactic used to track a company’s losses or simply mess with cheap people. The game is mostly unchanged when hacked, with one seemingly minor exception: Batman’s glider cape is hilariously unusable and has the aerodynamics of a piece of cardboard riddled with bullet holes.

It’s not that the cape is faulty, apparently; it’s simply that your version of Batman doesn’t know how to use it. Instead of gliding from one surface to another, Batman simply opens his wings over and over like a total ass-clown, causing him to lose altitude and fall down. It’s like you’re being forced to play with the pudgy Batman copycat from the beginning of The Dark Knight.

All the other gadgets still work, so you can always fight your way across the level on foot, right? Well, yeah, except that without the glider cape you’ll be completely stranded in a certain room — you know, the one filled with poisonous gas. That’s right, in the pirated version of Arkham Asylum, the always-prepared Dark Knight is such an useless idiot that he gets himself killed due to his shitty cape.

This trick gets misconstrued a lot as a simple game glitch, so you have people like this guy asking what’s wrong with his game at the official Eidos message board … only for the forum administrator to explain the situation and tell him: “It’s not a bug in the game’s code, it’s a bug in your moral code [punk].“

April 22, 2011

DC business owner successfully fights photo tickets

Filed under: Bureaucracy, Law, Technology — Tags: , — Nicholas @ 16:17

Jon sent me this link, which shows that you sometimes can fight speed camera tickets:

Five times and counting before three different judges, the Prince George’s County business owner has used a computer and a calculation to cast reasonable doubt on the reliability of the soulless traffic enforcers.

After a judge threw out two of his tickets Wednesday, Mr. Foreman said he is confident he has exposed systemic inaccuracies in the systems that generate millions of dollars a year for town, city and county governments.

He wasn’t the only one to employ the defense Wednesday. Two other men were found not guilty of speeding offenses before a Hyattsville District judge during the same court session using the same technique.

“You’ve produced an elegant defense and I’m sufficiently doubtful,” Judge Mark T. O’Brien said to William Adams, after hearing evidence that his Subaru was traveling below the 35-mph limit – and not 50 mph as the ticket indicated.

April 21, 2011

Elon’s Dragon may “land on Mars”

Filed under: Space, Technology — Tags: , , , , , — Nicholas @ 12:35

While you’re talking up your own private space venture, you can probably be excused for a bit of boasting:

Famous upstart startup rocket company SpaceX, bankrolled and helmed by renowned internet nerdwealth hecamillionaire Elon Musk, has once again sent its goalposts racing ahead of its rapidly-advancing corporate reality.

The plucky challenger has stated that its “Dragon” capsule is not merely capable of delivering supplies to the International Space Station: it is — potentially — also capable of carrying astronauts to the space station and back down to Earth again.

In a statement released yesterday, Musk and SpaceX also make the bold claim that the Dragon, once fitted with modifications that the company is now developing under NASA contract, would also be able to land “almost anywhere on Earth or another planet with pinpoint accuracy, overcoming the limitation of a winged architecture that works only in Earth’s atmosphere” (our emphasis).

April 20, 2011

Railgun in the US Navy’s future?

Filed under: Military, Technology, Weapons — Tags: , — Nicholas @ 13:21

H/T to Cory Doctorow for the link.

What will Smartphones kill off next?

Filed under: Technology — Tags: , , , , — Nicholas @ 10:21

When you look at their track record, Smartphones are technological hit-men, taking down category after category of stand-alone electronic devices:

Cisco’s recent announcement that it was closing its Flip mini-camcorder business got us thinking. It’s pretty clear that today’s smartphones, with their excellent HD video cameras, are partly to blame for the Flip’s demise. But how many other consumer products and services — digital or analog — are being killed off by the big, bad smartphone?

We’ve assembled a list of likely victims here. If you know of other smartphone-induced casualties, please tell us in the Comments section — or contact your local law enforcement authorities. Let’s start with the most obvious victims…

The only two items on their list I disagree with are stand-alone GPS units and paper maps. Paper maps because the portable GPS units are excellent for what I think of as tactical directions — take this turn, drive this distance, etc., but are not as useful for strategic purposes. Paper maps aren’t dead yet.

And the reason I don’t think GPS units are quite dead isn’t technological, but financial: I can’t afford to use my iPhone for GPS because of the insanely high data costs when I’m roaming, especially if I’m in the United States.

April 19, 2011

WikiLeaks exposes Chinese espionage unit

Filed under: China, Military, Technology, USA — Tags: , , — Nicholas @ 09:15

Strategy Page points out that it’s not just American and allied secrets that have been exposed by WikiLeaks:

Chinese Cyber War units have been plundering foreign government and military online data for over five years now. But thanks to Wikileaks, and several other sources, the identity and location of the main Chinese Cyber War operation is now known. The Chinese Chengdu Province First Technical Reconnaissance Bureau (1st TRB) is a Chinese Army electronic warfare unit located in central China (Chengdu), and is the most frequent source of hacking attacks traced back to their source. The servers used by the 1st TRB came online over five years ago, and are still used. The Chinese government flatly refuses to even discuss the growing pile of evidence regarding operations like the 1st TRB.

The 1st TRB is part of the Chinese Army’s Third Department, which is responsible for all sorts of electronic eavesdropping. But given the praise showered on the 1st TRB, a lot of valuable data has apparently been brought to Chengdu, and then distributed to the appropriate industrial, diplomatic or military operations. The hacking operation has been so successful, that it has obtained more staff and technical resources. As a result, in the last five years, detected hacking attempts on U.S. government and corporate networks has increased by more than six times. Most of these hacks appear to be coming from China. Not all the hacking is done by 1st TRB personnel. A lot of it appears to be the work of Chinese freelancers, often working for pay, but sometimes just to “serve the motherland.”

Reuters has a special report on “Byzantine Hades”:

According to U.S. investigators, China has stolen terabytes of sensitive data — from usernames and passwords for State Department computers to designs for multi-billion dollar weapons systems. And Chinese hackers show no signs of letting up. “The attacks coming out of China are not only continuing, they are accelerating,” says Alan Paller, director of research at information-security training group SANS Institute in Washington, DC.

Secret U.S. State Department cables, obtained by WikiLeaks and made available to Reuters by a third party, trace systems breaches — colorfully code-named “Byzantine Hades” by U.S. investigators — to the Chinese military. An April 2009 cable even pinpoints the attacks to a specific unit of China’s People’s Liberation Army.

Privately, U.S. officials have long suspected that the Chinese government and in particular the military was behind the cyber-attacks. What was never disclosed publicly, until now, was evidence.

U.S. efforts to halt Byzantine Hades hacks are ongoing, according to four sources familiar with investigations. In the April 2009 cable, officials in the State Department’s Cyber Threat Analysis Division noted that several Chinese-registered Web sites were “involved in Byzantine Hades intrusion activity in 2006.”
Another commercial wargame used for professional training

Filed under: Gaming, Military, Technology — Tags: , — Nicholas @ 09:02

Back in 2005, I posted some information about a software package in use by the USMC called Tacops, which was a single-developer wargame that provided very high training value. The unusual thing was that the military was willing to adopt a commercial wargame for their own training, over internally developed simulations. They seem to have gotten over that inhibition, as Steel Beasts, another single developer wargame, is seeing similar use today:

It was a decade ago that tank crews the world over became aware of a computer tank simulator, Steel Beasts, that was different. Steel Beasts was created by a single programmer, but with input from several professional tank troops. The graphics weren’t the greatest, but it was very accurate, so much so that the professionals were starting to use it as a training device. The publisher and creator of Steel Beasts seized the opportunity, and by 2006 there was a version for military use (Steel Beasts Professional) only that allowed for the use of a LAN, an instructor watching over how all the players were doing, scenario and terrain building and AAR (after action report) functions so that everything that happened in a game was captured. This allowed the instructor to point out errors, and what should have been done.

So far, ten countries (Austria, Denmark, Sweden, Norway, Finland, Chile, Canada, Australia, Spain and the U.S.) have bought Steel Beast Professional (at $125 a copy) for training their armor vehicle crews. The troops find the vehicle controls, and tactical situations to be realistic, and compelling. The game really gets the pucker factor going, and even before the pro version came along, troops were buying the commercial version and playing it for the professional, and entertainment, value.

April 18, 2011

Happy thought of the day

Filed under: Law, Liberty, Media, Technology, USA — Tags: , , , , — Nicholas @ 15:43

Darlene Storm offers this cheery little nugget of information (from a post back in December):

Dear Americans: If you are not “authorized” personnel, but you have read, written about, commented upon, tweeted, spread links by “liking” on Facebook, shared by email, or otherwise discussed “classified” information disclosed from WikiLeaks, you could be implicated for crimes under the U.S. Espionage Act — or so warns a legal expert who said the U.S. Espionage Act could make “felons of us all.”

As the U.S. Justice Department works on a legal case against WikiLeak’s Julian Assange for his role in helping publish 250,000 classified U.S. diplomatic cables, authorities are leaning toward charging Assange with spying under the Espionage Act of 1917. Legal experts warn that if there is an indictment under the Espionage Act, then any citizen who has discussed or accessed “classified” information can be arrested on “national security” grounds.

H/T to Bruce Schneier for the link.

The Magic Washing Machine, by Hans Rosling

Filed under: Economics, Environment, Health, Technology — Tags: , , , — Nicholas @ 09:49

H/T to Jon for the link.

April 14, 2011

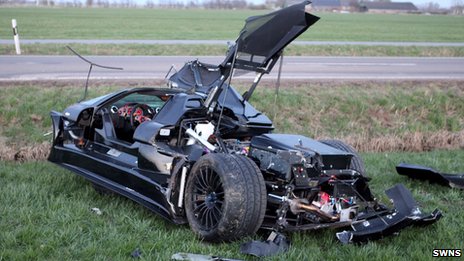
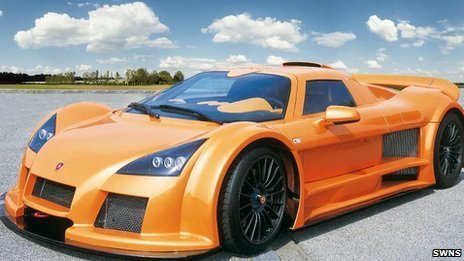
From supercar to superscrap

Filed under: Europe, Germany, Technology — Tags: , — Nicholas @ 12:15

This is what it looked like before the owner’s son took it for a drive:

And this is after the drive got stopped a bit early:

The good news is that the driver and passenger were able to walk away from the wreck, leaving £275,000 of scrap metal behind.

DANE to address weaknesses in internet security?

Filed under: Technology — Tags: , — Nicholas @ 12:05

The Economist looks at a possible way to address the known weaknesses of the current internet security defaults:

[A] comprehensive solution would let domain owners confirm that the names and machine numbers issued by a given CA are kosher. Under DNS-based Authentication of Named Entities (DANE), a standard being developed by Mr Schultze and others at the Internet Engineering Task Force, a browser retrieves a certificate from a web server, but checks with the DNS whether the certificate is in fact the one that was issued to a given domain owner. So, though a CA will still provide a validation step, the domain owner will have had to give it the thumbs up first. To prevent malevolent fiddling the DNS infrastructure itself needs to be secured, too. A long-running effort to do this, known as DNSSEC, hit a key milestone in 2010 and may have enough pieces in place soon to be usable. This is important because DANE would be incomplete without it.

Whilst all current browsers must be updated to take advantage of DANE, the new system can coexist with the old, and a gradual transition can be made. Browser plug-ins could bridge the gap before browser makers build in DANE, too. Those that want the added robustness of the new system — whether individuals, companies, or governments — may accelerate the adoption of updated browsers as DANE becomes available.

These moves do not provide total assurance that what your browser is told about an internet site’s identity and security is true. Trust, but verify — and verify again.

April 13, 2011

Never seen this before

Filed under: Randomness, Technology — Tags: — Nicholas @ 11:28

My Rogers email account appears to have a nasty case of rot-13 encoding in the address book. I’d include a screen capture, but now that I’ve told you the trick of decoding it, it’d expose folks’ email addresses, which would be a bit unethical of me. At first, I thought it was just a garble, but I noticed that a lot of the addresses ended in “.pbz” and “.pn” (that’d be “.com” and “.ca” rotated 13 characters).

It’s not crippling, as I can just copy and paste from existing email messages, but it is annoying.

Update, 14 April: It appears to be fixed now.

April 12, 2011

Israel’s “Iron Dome” missile defence system in action

Filed under: Middle East, Military, Technology, Weapons — Tags: , — Nicholas @ 08:42

Strategy Page discusses the first use of the new Israeli anti-missile system to defend civilian targets last week:

Israel has deployed two batteries of its Iron Dome anti-missile system near the Gaza border. One is near the town of Beer Sheva (the largest town in the Negev desert) and another near the coastal city Ashdod (the largest city within range of 122mm rockets fired from Gaza). On April 7th, a 122mm rocket was intercepted near Ashkelon, which is south of Ashdod. This deployment was prompted by an increase in rockets fired from Gaza, and the growing use of longer range (20 kilometers) 122mm rockets. Iron Dome proved that it could work under combat conditions, preventing the longer range, factory made, rockets from landing in populated areas.

This is a big turnaround for this system. Four months ago, the Israeli military revealed that its new Iron Dome anti-rocket system was not meant for defending towns and villages, but military bases. For years, politicians touted Iron Dome as a means of defending civilians living close to rockets fired from Gaza in the south and Lebanon in the north. But it turns out that it takes about 15 seconds for Iron Dome to detect, identify and fire its missiles. But most of the civilian targets currently under fire from Gaza are so close to the border (within 13 kilometers) that the rockets are fired and land in less than 15 seconds. This means that the town of Sderot, the closest Israeli urban area to Gaza, cannot be helped by Iron Dome.

[. . .]

Iron Dome uses two radars to quickly calculate the trajectory of the incoming rocket (Palestinian Kassams from Gaza, or Russian and Iranian designs favored by Hezbollah in Lebanon) and do nothing if the rocket trajectory indicates it is going to land in an uninhabited area. But if the computers predict a rocket coming down in an inhabited area, a $40,000 guided missile is fired to intercept the rocket. This makes the system cost-effective. That’s because Hezbollah fired 4,000 rockets in 2006, and Palestinian terrorists in Gaza have fired over six thousand Kassam rockets in the past eight years, and the Israelis know where each of them landed. Over 90 percent of these rockets landed in uninhabited areas, and few of those that did caused few casualties. Still, a thousand interceptor missiles would cost $40 million. But that would save large quantities of military equipment and avoid many dead and injured troops. Israel already has a radar system in place that gives some warning of approaching rockets. Iron Dome will use that system, in addition to another, more specialized radar in southern Israel.

Next iPhone to be delayed into 2012?

Filed under: Technology — Tags: , , — Nicholas @ 08:27

According to sources at some of the various suppliers for key iPhone components, Apple may be delaying the next iPhone:

Analyst firm Avian Securities said that production of the iPhone 5 won’t begin till September, meaning a holiday launch at the earliest, or even a New Year’s debut.

The note, reported in Business Insider, is based on chats with key component suppliers, which support a consensus view that launch will be either a late 2011 or early 2012 event.

The note adds that a low-spec, low-price iPhone is also on the Apple roadmap, though exactly where on the roadmap is unclear.

This is surely a worrying development for the iPhone elite — not only could such a nano-iPhone divert some components, further pushing back the iPhone 5, but it would mean that “ordinary people” can get their hands on a fondleslab.

My own iPhone 3G is still holding up well (I’m not a particularly abusive owner), but I’ll finally be out of contract with Rogers in August, so the delay in the next iPhone release may increase the chances of me switching to an Android phone instead.

« Newer Posts — Older Posts »

Powered by WordPress