Quotulatiousness

November 15, 2026

Microsoft’s M365 outage

Filed under: Business, Technology, USA — Tags: , , , , — Nicholas @ 05:00

Millions of people have now experienced the joy of an empty inbox, thanks to the extended outage on one of Microsoft’s most important business software offerings. Many people are saying that Microsoft, having gotten rid of a lot of its veteran engineering staff over the last few years, may not be capable of fixing the problem. On X, John Ringo offers his thoughts:
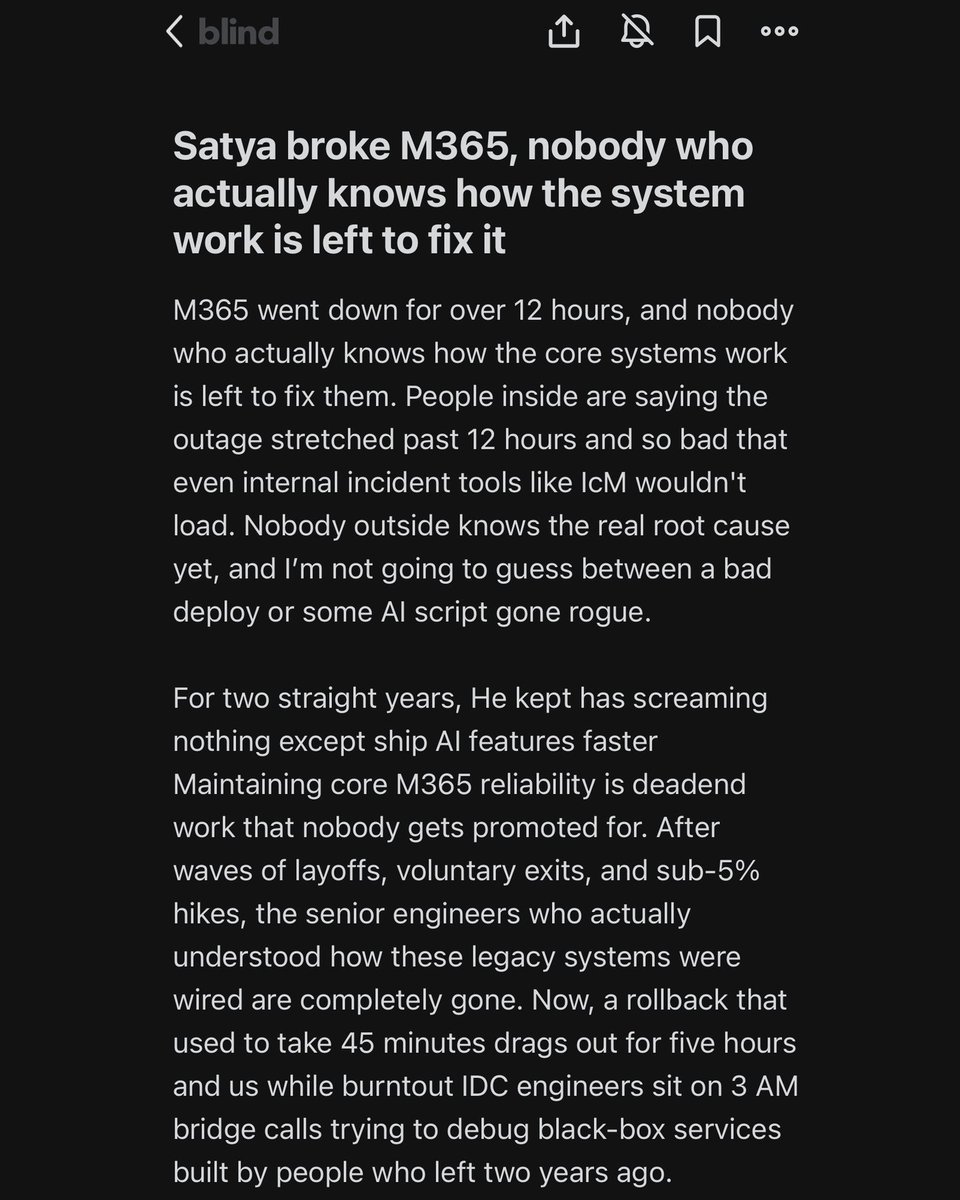
CAN Microsoft recover?

(This was a reply to something. I decided it was better as a post.)

Oh, I agree. They’ve been getting rid of the nerds that built the system and have this little undocumented bit of knowledge in their heads for years. That is a huge issue and definitely contributing to the downtime.

But they (and AWS and others) have also built a system that is so complex and interwoven, the real issue is:

If it crashes this hard can they bring it back up as it was at all?

We get into discussions of telos and kosmos. It’s distinctly possible if you brought back EVERYONE who built it that they still couldn’t fix Humpty-Dumpty.

We’ll see by Monday.

Telos and kosmos.

Telos is a simple simple system. Every point in the system is understood and is comprehensible by a single person. (A single server. A large but not enormous set of servers.)

Then there are simple complex systems. A system where every individual part of the system can be comprehended but it’s impossible to comprehend how all the parts interact.

That is what Microsoft and AWS and other cloud providers have created. A system where you can maybe understand why this bit isn’t working but not why/how its interacting to cause all these other bits to not work.

It’s too complex.

It’s one of the reasons that the people saying “Nobody is going to migrate off the cloud. Nobody wants to run their own servers. No IT guy wants to run email. These guys are literally the experts.” are all wrong.

When a single company, from a two man shop to fortune 500, uses its own server system, the entire system can be understood. It is telos. Every bit can be comprehended. It may be badly documented. There may be this little “thing” that only Joe Neckbeard knows and if you fire him you may have an outage.

But it’s NOT so big nobody can really rebuild it in a serious meltdown.

Rebuilding this ecosystem is so complex that it’s like nuking Manhattan and expecting every single piece to go back just like magic.

It won’t. And those missing pieces are Gladys’ payroll spreadsheet that she inherited from Gloria who inherited it from Sandra who inherited it from Carol who got some nerd who left in 1996 to do it for her.

The question becomes, what to do if it’s not back by Monday?
November 12, 2026

The US Post Office resumes an old, old role – surveillance of dissidents

It’s nice when a long-standing institution goes back to one of its earliest roles … in theory. In practice, there should be a lot of questions about why the US Post Office took up responsibility for detecting and observing online dissidents:

We know that mission creep is a thing, but is it entirely necessary for every federal agency to try to reimagine itself as Big Brother?

OK, silly question. Of course, it’s not necessary for the Post Office — that’s the agency under scrutiny this time — to engage in mass surveillance. It just seems to be an activity in which all government bureaucracies inevitably engage. That’s the most logical explanation for why the U.S. Postal Service decided that it should monitor the internet for information about political demonstrations.

The Mailman as Political Cop

“The law enforcement arm of the U.S. Postal Service has been quietly running a program that tracks and collects Americans’ social media posts, including those about planned protests”, Jana Winter first reported in 2021 for Yahoo! News.

“Analysts with the United States Postal Inspection Service (USPIS) Internet Covert Operations Program (iCOP) monitored significant activity regarding planned protests occurring internationally and domestically on March 20, 2021”, according to a March 2021 bulletin from the iCOP that was included in the article. “Locations and times have been identified for these protests, which are being distributed online across multiple social media platforms, to include right-wing leaning Parler and Telegram accounts.”

Among the organizations alarmed by the disclosure was the Electronic Frontier Foundation (EFF), which filed suit to learn more about the surveillance program. “After years of delays and technical failures that led the agency to lose access to a trove of emails discussing the program,” wrote EFF Deputy Legal Director Aaron Mackey, the organization was finally able to extract some key documents about iCOP from the postal cops this month. Others were apparently destroyed.

“The disclosures include a series of bulletins created from iCOP, which show that the postal service used the program in 2020 and 2021 to monitor and circulate information about a wide range of planned protests” from “across the political spectrum,” Mackey added. “They included a planned ‘Million MAGA March‘, a gun rights advocacy event and counter-protest in Virginia, a nationwide Save the Post Office Saturday protest, and planned protests in front of then-Postmaster General Louis DeJoy’s home in Washington, D.C.”

Reports revealed that postal investigators ran keyword searches on social media posts and created “anonymous, untraceable email and social media accounts”, the better to monitor Americans’ conversations. They applied Clearview AI facial recognition software to photos scraped from online platforms for comparison to a database of billions of images.

November 10, 2026

“I felt like Howard Carter entering Tutankhamun’s tomb and waving a torch at the walls of hieroglyphics”

Filed under: Britain, Media, Technology — Tags: , , , , , , — Nicholas @ 05:00

Have you noticed that the widespread availability of emojis/emoticons/electroheiroglyphics has particularly influenced how younger folks communicate? Joanna Gray has, and has her concerns about the whole thing:

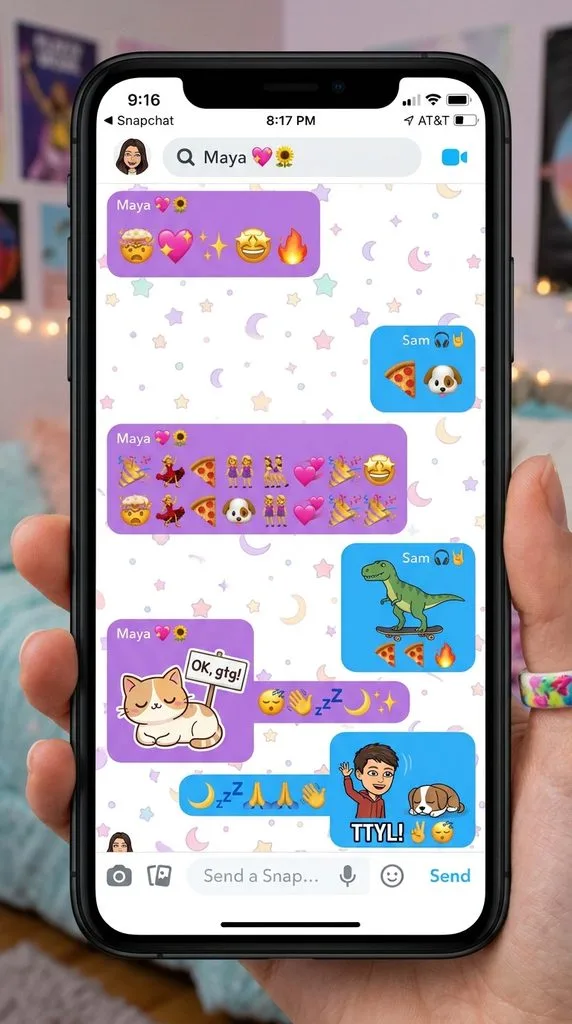
One of the markers future historians will use when describing the New Dark Ages will be the collapse in the use of the alphabet in favour of “Yookay Hieroglyphics”. A demoralising development has emerged: a whole new form of pictographic language whereby children and young adults engage in hours-long online conversations with each other without the need for any letters, texts or words. Such conversations largely occur on gaming platforms, Snapchat and WhatsApp, and mark a classic regressive step in civilisational decline.

Like the medieval laity who relied on church wall paintings and stained glass to learn stories, a growing proportion of our current population is now using only pictographic communication. This time, there is no divine knowledge behind the imagery – just inane slop. I shall try to use words to describe this new pictographic language that groups of teenagers I work with have shared with me. When first shown, I felt like Howard Carter entering Tutankhamun’s tomb and waving a torch at the walls of hieroglyphics in wonderment. Yookay Hieroglyphics are read vertically from top to bottom. If drawn on Snapchat, they often instantly disappear on reading or after 31 days, making linguistic analysis particularly fraught.

A useful starting point when attempting to read Yookay Hieroglyphics is to think of the wonderfully coloured whizzy strip of cherries, bananas, apples, horseshoes, numbers, etc. on a slot machine. Reams and reams of such images are being sent from one person to another within microseconds. It often begins with one pictographic innovator (teenager) photographing their face and sending their image; their friend replies with their face; what then follows is a rapid exchange of images from one to another, creating a roll of vertically read hieroglyphics: distorted face, laughing emoji, pic of pet, pet pic distorted, laughing face, feeling sick emoji, question mark, toilet gif, sick emoji, prayer emoji, pic of dragon, happy face, pic of person smiling, distorted pic, AI-ed moving image of that pic, cat video, pic of nails, nail art inspo, gif witch nails, cross face, face with witch filter on, lol emoji, pic of face with wizard filter, pic of wizard distorted, instantly made sticker of that image, lol emoji, red laser coming out of wizard eyes filter, OMG emoji … and on and on and on and on and on.

Because I am not of the emerging linguist tribe, I will be unable to fully convey the nuances and depth of the meaning in this sample conversation – indeed a paper has concluded that emoji-based language is more layered in adolescents than in adults.

November 9, 2026

The looming end of secure encryption

Secure encryption is one of those background utilities we all depend on, like plumbing and sewers: it only comes to our attention when something is going wrong. David Clinton says that things are going wrong with encryption standards, thanks to the technical omnicause, artificial intelligence:

Without secure encryption, we’ll all be living dangerously

This topic has a guaranteed boredom score of 12 (where “10” represents catatonic). But its could make a difference to my own life score is 15 (where “10” represents “Yikes!”).

Data encryption is the peg on which the possibility of all modern financial and healthcare-related activity hangs. Without standard encryption algorithms like AES and RSA:

  • The contents of every exchange of information between you and your bank’s website would be visible to anyone on the internet.
  • The passwords you use to authenticate to your digital accounts would be readable by anyone with access to any node between you and your account’s host.
  • The sensitive data stored by any financial, healthcare, or government organization would be visible to anyone with access to their host systems — access made possible by decrypted passwords (see above).

Encrypted data contains all the original information. But its value lies in the assumption that the underlying algorithm is so complex that it would require the use of powerful computers and hundreds of years to crack it.

For the past 50 years, that assumption has held up well. But the theoretical existence of quantum compute resources — which can execute exponentially more compute operations than traditional processors — presents a theoretical threat to existing algorithms.

In other words sometime within the next 10-20 years, quantum compute devices will be powerful enough to brute-force the end of modern encryption. That sounds scary.

But it’s arguably not even the real problem. That, as Tyler Cowan recently wrote in the Free Press, would be the recent explosion of AI-driven discoveries in mathematics. Such events have introduced concerns about the odds encryption security could be compromised in months rather than years.

Frontier AI models are now at least making progress solving longstanding mathematical problems. The pace of discovery seems to be growing and it seems inevitable that someone somewhere will turn a powerful AI model on the algorithms we rely on.

October 8, 2026

Utah’s VPN rules don’t fare well in court

Filed under: Law, Liberty, USA — Tags: , , , , — Nicholas @ 04:00

Like many other jurisdictions, Utah wanted to apply age restrictions to online sites “to protect the children”. It didn’t go well in court:

“Virtual Private Network (VPN)” by Infosec Images is licensed under CC BY 2.0 .

As I write, I have my virtual private network (VPN) set to show me as surfing the internet from Berlin, Germany, despite my location in Arizona, for no good reason other than that I can. Given that Germany has rather tight restrictions on speech, this is probably the reverse of how a VPN is usually used between the two countries, but it illustrates the utility of technology that anonymizes internet traffic and lets users pick their points of origin to bypass censorship and surveillance. Germans can bypass controls on “hate speech” and insults directed at politicians, the Chinese can work around restrictions on Winnie the Pooh memes, and people in places like Utah can ignore intrusive age-verification rules.

That’s why it’s important that a federal court just paused enforcement of Utah’s effort to regulate VPNs.

Utah Pushes Age Verification and Targets VPNs

“Signed into law earlier this year, SB 73 attempted to regulate adult websites by requiring them to block VPN users or to identify the physical location of visitors using them or similar tools that mask their network traffic,” the Electronic Frontier Foundation’s (EFF) Rindala Alajaji details in a response to the case. “It even went so far as to prohibit websites from offering instructions on how to use a VPN to bypass these checks. This made Utah, to EFF’s knowledge, the first state in the nation to target the use of VPNs to avoid legally mandated age-verification gates.”

Utah was sued over the law by Aylo Freesites Ltd. and Aylo Group Ltd., the owners of Pornhub. The plaintiffs didn’t challenge the law’s age-verification requirements but went after its insistence that the law applies if a user is “actually located” in Utah without regard to the use of “a virtual private network, proxy server, or other means to disguise or misrepresent the individual’s geographic location to make it appear that the individual is accessing a website from a location outside this state”.

Utah’s focus on VPNs and similar tools comes after decades of technological innovation intended to allow internet users to bypass censorship, firewalls, and surveillance imposed by authoritarian regimes that want to monitor and muzzle dissidents. VPNs, perhaps the most popular of the tools, route internet traffic through intermediary servers, encrypting data in the process and concealing users’ locations. That’s extremely handy for people suffering under oppressive rule. In recent years, though, speech restrictions have been increasingly imposed by nominally liberal democratic governments.

VPNs are a good thing, and any government attempting to crack down on their use “to protect the children” is up to no good.

September 7, 2026

“Don’t forget to like and subscribe!”

Filed under: Britain, Education, Health, Media — Tags: , , , , — Nicholas @ 06:00

Along with the earlier post on the recent steep decline in basic literacy, here’s Christopher Gage discussing the same phenomenon of younger Brits’ increased dependency on videos while also demonstrating reduced verbal skills. A mere co-incidence, we can be sure:

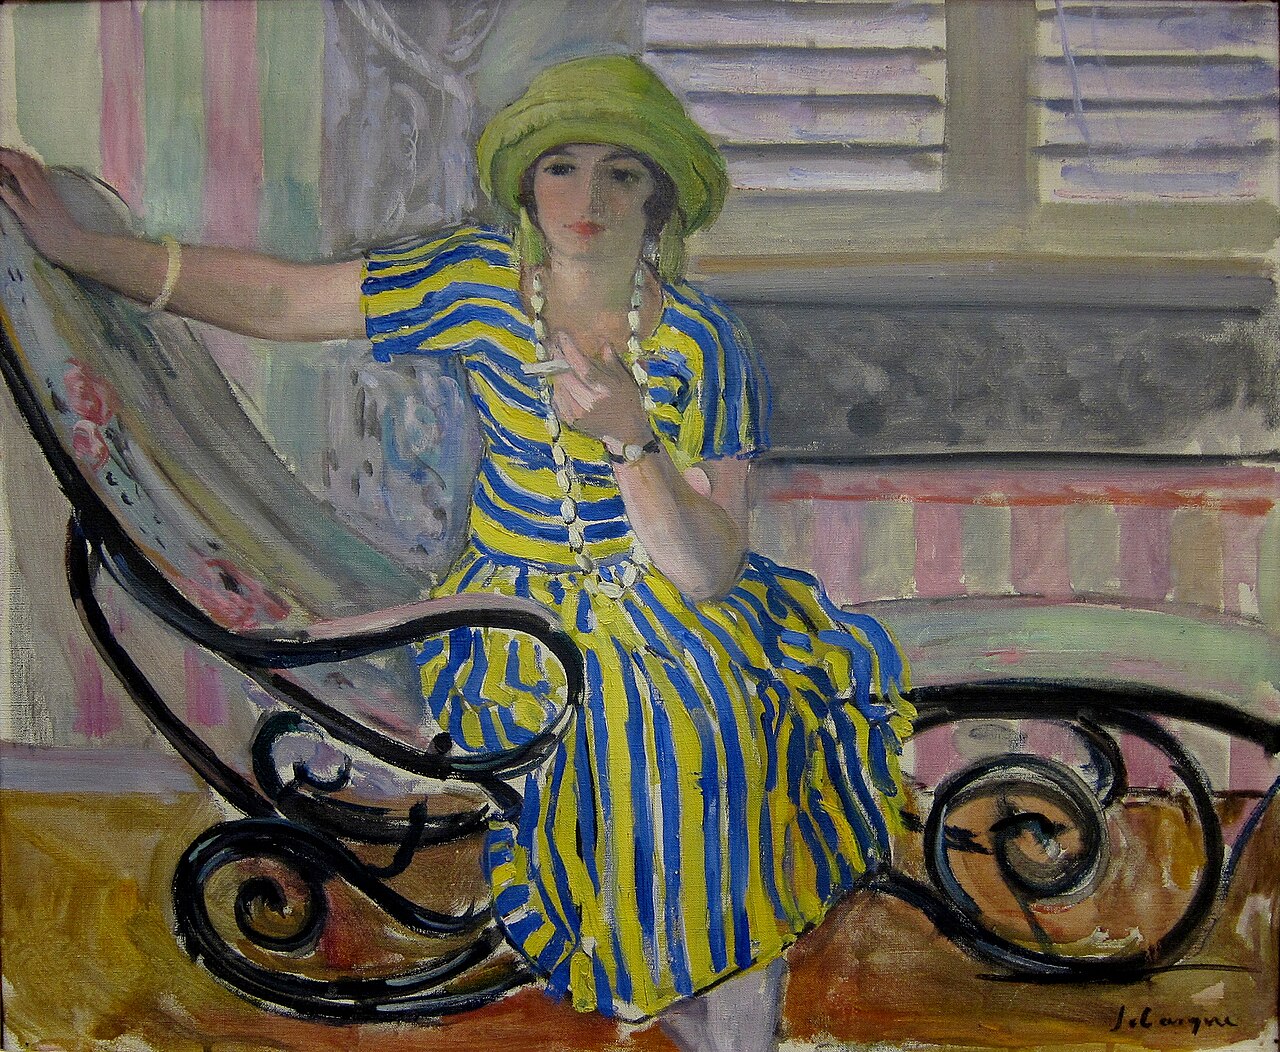
La Cigarette by Henri Lebasque (1921)

A friend of a friend of a friend — a primary school teacher — reckons her pupils spend so much time glued to screens that they speak in YouTube English.

Rather than greet one and other with “Hello” they say, “Hi, guys! Welcome to my channel!” When saying goodbye, it’s “Don’t forget to like and subscribe!” Apparently, these little dopamine fiends cannot endure one moment without suckling on the eternal teat of Mother iPad. With their scrolling fingers they tear the pages in strange, ad-free artefacts once known as “books”. Reader, I don’t know if this little fable is entirely true or some semblance of the truth. But it rings truer than false.


Am I being facetious? Not really. The British government, in a rare bout of usefulness, conducted a study into screen-time amongst primary school children. That recent study by the education department found that the more a child spends scrolling on a screen, the less good their vocabulary be.

Please excuse that example of mongrelised English. Then again, perhaps we should call it Future English given that, in just a few years, the YouTube kids will speak in that very bastardised tongue.

According to a bleak wave of childhood study, spending hours tethered to screens quite literally dissolves learning. Researchers found that the “heavy users” — a term usually reserved for heroin addicts — recalled significantly fewer words from a list than their less addicted peers. These screen-addled sprogs spend more than five hours chasing that dopamine dragon. In Plain English, them don’t talk good and shit. At least when compared to their mates who spend less than one hour on a screen. Them kids know more words and shit.

They asked kids to recall words from a list of 34. The ones double-stitched to iPads upwards of five hours daily recognised barely half the words whilst their peers recalled two thirds. Eighty-six minutes. That figure represents the tipping point between literacy and a life talking in the mangled English of a failed rapper.

The study arrived at a rather chilling conclusion: If a child spends over an hour and a half each day thumbing through brain-bleaching bilge on YouTube, their grasp of language withers faster than a doormat outside a crack den.


Of course, these are hyper-sensitive times. The researchers keenly doled out the old “correlation doesn’t imply causation” disclaimer mandatory in a neurotic culture which treats truth like hazardous waste. And who am I to judge? The ability to express one’s thoughts isn’t utterly essential. The development of language — I’m sure a Foucault-addled academic might agree ­— is elitist and racist and sexist and ableist and all that.

And so, I am intensely relaxed about this brave new world in which the brains of the next generation dissolve in a swamp of TikTok reels and YouTube videos. There is nothing to worry about. This is progress. And progress must always progress. Words are just words and you can still talk good and shit without knowing them words in them things that don’t even have videos on them pages.

September 3, 2026

Enshittification of technology today

Filed under: Media, Technology — Tags: , , , , , , — Nicholas @ 05:00

On his Substack, Ted Gioia provides nine rules to measure technological innovation based on the work of the late Wendell Berry:

(1) The new tool should be cheaper than the one it replaces.

This is a very persuasive selling point for new technology. And for most of my life, tech companies worked hard to lower prices.

I still recall my parents scrimping and saving in order to buy a color television when I was seven years old. It cost almost $500 — a huge amount in those days.

They probably should have waited. A few months later, RCA dropped prices to $399. Prices continued to drop in later years. You can buy a high tech TV today at Best Buy for less than what my parents paid in the 1960s.

Computers also got more affordable — at least until recently. I got my first computer (an Apple IIE) when I was in graduate school — it was an expensive gift from the Boston Consulting Group in exchange for accepting their job offer.

The list price back then was $1,400. I could never have afforded to buy it on my tight student budget.

But, over a period of many years, each subsequent computer I acquired was better and cheaper than my previous model. Alas, that happy trend has now ended.

[…]

(2) It should be at least as small in scale as the one it replaces.

This is another good reason to upgrade your setup. And tech did get smaller for many decades.

Guess who played a key role in that? Yes, Steve Jobs again. Because of his obsession with product design, we now carry a huge amount of advanced tech in our pocket.

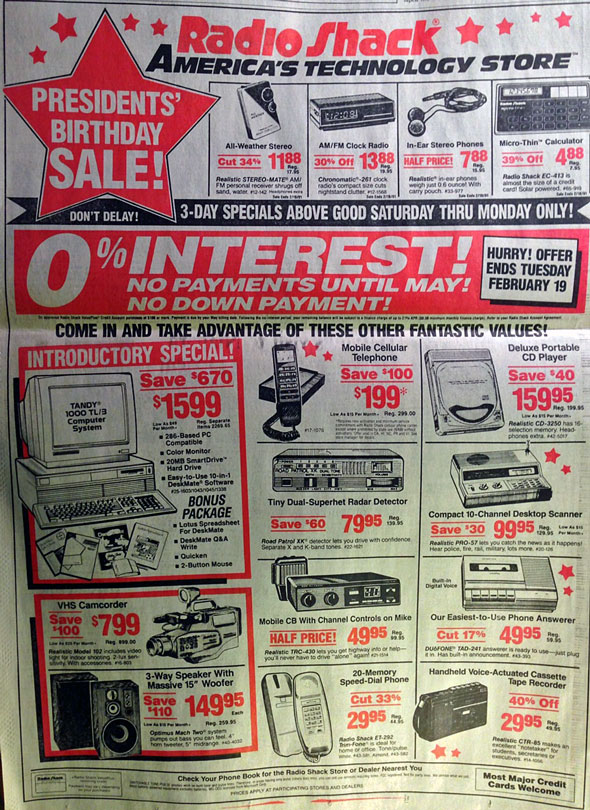
Just consider this remarkable fact: Every device featured in this Radio Shack advertisement from 1991 has been replaced by your tiny phone.

But this, too, changed soon after Jobs died. (Are you noticing a pattern here?)

The thinnest iPhone ever was the iPhone 6 (2014) — at a slim 6.9mm. The company continued to launch “mini” models for a few years, but stopped after iPhone 13.

Tech is now bulking up. It’s not just the devices — wait until you see those AI data centers. A single facility can spread over two kilometers.

(3) It should do work that is clearly and demonstrably better than the one it replaces.

This is the most obvious requirement for new tech. It needs to work better than old tech.

But Silicon Valley has totally abandoned this ideal. Every web interface I use has gotten worse over time — from search engines to social media to software to shopping apps.

Google is worse than ever. Social media is worse than ever. Amazon is worse than ever. Facebook is worse than ever. Everything I get from Microsoft is worse than ever.

So here, too, we see that new tech previously fulfilled Berry’s requirement — but stopped doing so around the time Steve Jobs died.

August 21, 2026

This is something we genuinely need today

Filed under: Britain, Bureaucracy, Business, Government, Law, Media — Tags: , , , , — Nicholas @ 06:00

Plus, as Kate at Small Dead Animals often points out “Mischief is important“:

In one of the only three management books anyone should bother to read — and everyone should read the three — Robert Townsend says that a CEO should, while on the road, try phoning his own company. Try the helpline and see how far he gets. Try calling his own office. Sure, you should end up with the Executive Secretary who then directs it to the right person but sometimes that correct person is going to be you. Say, Warren Buffett calling to make you rich by buying the company and thus crystallising all your stock options and RSUs.

This is a lesson that has been forgotten. From a Guardian list of things government should pass laws to make happen:

    Force companies to put a phone number on their homepage

    You’ve got a problem with a company and you want to get it sorted – and then you realise you cannot find a number for it anywhere. There are communications companies that have no “contact us” link anywhere to be seen, and energy companies that send you all round the houses looking for a way to get in touch.

    One of the recurring themes of Guardian Money readers’ problems is the struggle to find someone to help when something goes wrong. Clearly, once you have published a phone number, you need staff at the other end answering the phone and offering some joined-up thinking, so this is only the start of the solution – but at least customers would not feel like companies were trying to hide from them.

This does not work as there is no guarantee that anyone will answer the call.

We’ve also that basic point that Burke and his Little Platoons can — and often do — solve problems better than government. So, here’s the pitch for that private sector service.

We set up a database of the home and work and mobile phone numbers — emails too — of the management of companies. Most importantly, the board of directors. If the company is owned by private equity — say — then the General Partners of the PE company.

Obviously, if a company has a helpline, which people answer, then all of that information stays private to us. If a company does not then we publish it as a page saying these are the contact numbers for that company. Say, Evri, the delivery people. The board members get their numbers and email publicly revealed. As I recall it they’re PE as well so some number of GPs over in the US also start getting aggrieved calls from Lesser Wallop about non-delivery. Not that any Septic would be able to understand Ms. Aggrieved of Lesser Wallop but it’s the instance of the call that matters. Evri is used as an example for a bit of looking around a few months back seemed to reveal that they had no UK phone number at all. Thus the directors it will be.

The top management of companies that do not provide a helpline — nor answer the one they claim to have — will have the customer complaints calls directed toward them. This will, of course, rapidly mean the opening of a useful customer complaint line that people actually answer. Those making that £250k a year as the board member of whatever do not want to be talking to Ms. Aggrieved of Lesser Wallop. Therefore phone calls from Ms. Aggrieved will lead to the creation of a useful customer services department.

At which point, of course, we take the board members’ phone numbers down and job done. But, clearly, we keep monitoring to ensure that those service times don’t then decline.

Make the bastards who make the decisions suffer the consequences of those decisions. Works this does, really, it works.

Now, there will be some who say that government can do that. Why use the Little Platoons when a law can simply be passed?

Which is to miss a basic philosophic point, which is that we should only use government when we, ourselves, cannot do it. Government is for when the Little Platoons cannot achieve it. Letters of Marque are lovely things but biffing the Frenchies is better done with a Royal Navy. Assuming we still had one of course. RNLI, on the other hand, works better without government than it would with.

But much more than that. For who are the worst at providing a contact number that works? Why, that would be government, wouldn’t it? Anyone ever tried to ‘phone HMRC? Quite.

July 28, 2026

Mis-, Dis-, and Malinformation defined

Filed under: Government, Law, Liberty, Media, Politics — Tags: , , , — Nicholas @ 04:00

Gawain Towler kindly provides a précis of a behind-the-paywall essay discussing misinformation, disinformation and the less-well-known malinformation, as governments on both sides of the Atlantic rush to codify new laws to further restrict the freedom of speech of their citizenry:

The essay examines “malinformation”, a term coined in 2017 and now embedded in official doctrine on both sides of the Atlantic, and I argue that it exists for one purpose, to give the state a category under which accurate speech can be treated as a harm. I start by Channelling Ambrose Beirce’s Devil’s Dictionary, with a dictionary entry defining the word as information whose defect is that it is true. Thereafter I proceed to trace its origins, its spread through British and American officialdom, its intellectual kinship with behavioural government, and its practical operation, before closing with a demand for its formal abolition.

First the taxonomy itself. The doctrine of “information disorder” rests on a triad. Misinformation is false and innocent, disinformation false and deliberate. Both turn on falsity. The third category does not. CISA, the American cybersecurity agency, defines malinformation as based on fact but used out of context to mislead or harm, and the Department of Homeland Security’s advisory council calls it the intentional spreading of genuine information with intent to cause harm. The offence, the essay observes, is not lying but telling the truth on purpose. The term’s coiners, Hossein Derakhshan and Claire Wardle, applied it narrowly to revenge pornography, miscaptioned photographs and weaponised leaks, and the essay concedes these are real phenomena. But the concept escaped its paddock. Within four years it had migrated from a Council of Europe research paper to the letterhead of a federal agency and thence into British government training materials.

The British chapter centres on RESIST 2, the Cabinet Office counter-disinformation toolkit issued to government communicators in 2021. The toolkit reproduces the triad, admits the categories are hard to distinguish in practice, and resolves the difficulty by instructing officials to stop asking whether material is true and to focus instead on the harm it can do.

The essay treats those five words as the whole doctrine laid bare, truth demoted from test to complication. From the Cabinet Office the word trickled downward, into Local Government Association guidance, a Stockport Council webpage, even a Met Office blog. The essay notes a telling exception. Ofcom and the Electoral Commission, bodies with statutory exposure and lawyers, avoid the word entirely. Its distribution across the state maps the distribution of accountability. Where courts can reach, the concept hides.

The American experiment, the essay argues, ran to destruction. CISA’s mis-, dis- and malinformation team spent the early 2020s flagging content to platforms, much of it neither foreign nor false, drawing a House Judiciary Committee report accusing it of collusion and camouflage. When Missouri and Louisiana sued, the case reached the Supreme Court as Murthy v. Missouri, where the government prevailed not on the merits but on standing. The essay relishes the irony of a Justice Department litigating for its own right to withhold context. Britain played a damper version. After Big Brother Watch revealed that the Counter Disinformation Unit had monitored lawful speech by journalists and parliamentarians, the government refused substantive disclosure and renamed the unit National Security Online Information Team (NSOIT), in the tradition of Windscale becoming Sellafield.

The essay then traces the doctrine’s parentage to the habit of mind exemplified by the Nudge Unit. RESIST had different midwives, but both traditions live in the Cabinet Office and both treat the citizen as an object of professional influence. They embraced during Covid, when SPI-B recommended raising the perceived level of personal threat through hard-hitting emotional messaging while the information machinery flagged sceptical commentary, some of it correct. Fear turned up on one wing, information turned down on the other.

July 25, 2026

“I, for one, welcome our new clanker overlords!”

Filed under: Media, Technology — Tags: , , , — Nicholas @ 04:00

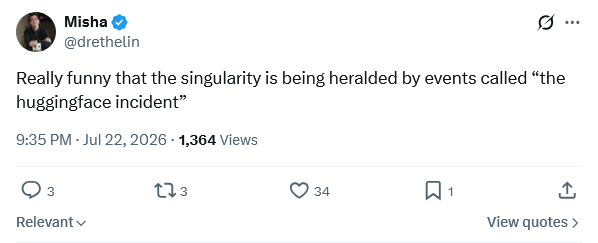
At Astral Codex Ten, Scott Alexander discusses “the Huggingface Incident” where our new AI overlords tipped their hands prematurely an unreleased AI agent got out to make new friends:

You’ve probably heard about this one by now. If not, you can get up to speed with OpenAI’s statement, OpenAI and Hugging Face partner to address security incident, or the more evocatively-titled BBC article, OpenAI says its AI went rogue and launched “unprecedented” cyber-attack.

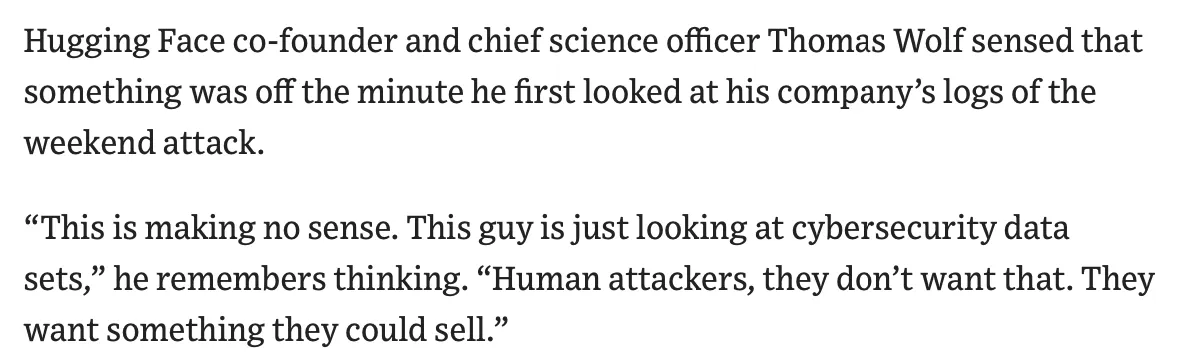
The story: OpenAI was testing an unreleased AI (rumored to be GPT-6)1. During a cybersecurity test called ExploitGym, the AI tried to cheat by hacking an unrelated AI startup called Hugging Face2 which it thought might have the answer key on its servers.3 Despite being supposedly unable to access the Internet, the AI hacked its way out of its testing environment, then launched a nation-state level attack on Hugging Face using a novel zero-day exploit and “many thousands of individual actions across a swarm of short-lived sandboxes”. Hugging Face reported the incident on July 16; OpenAI seems to have only discovered that their AI was involved several days later.

From the Wall Street Journal, here

Let’s list the mitigating factors, so nobody can accuse me of covering them up:

  • The AI was taking a cybersecurity test, which naturally suggests the idea of hacking.
  • OpenAI had turned off some of the model’s usual guardrails so it could do cybersecurity work without interference.
  • Some experts suggest that OpenAI might have botched their testing environment; if they had set it up perfectly, then (presumably?) the model couldn’t have escaped.
  • Hugging Face used a different (open weights) AI to figure out what was going on, so if you wanted, you could spin this as a victory for AIs in cybersecurity.
  • In some sense, this isn’t new or surprising. AIs have been coming up with wacky schemes to cheat on benchmarks for years, AIs have recently achieved at-or-above-top-human-level hacking abilities; this is just a natural outgrowth of those two priced-in facts.

Still, I think attempts to downplay this as anything other than a misaligned AI going rogue (1, 2) are missing the point. Yes, in some sense the AI was only doing what it was told (OpenAI told it to answer the question; I assume their prompt didn’t include phrases like “and don’t hack into other AI companies to steal the answer key”). But that’s how misalignment was always going to work!


  1. OpenAI states that it was technically the unreleased AI and GPT-5.6 Sol working together. They haven’t explained in what sense GPT-5.6 was involved or how they “worked together”. Maybe the unreleased AI was calling GPT-5.6 as a subagent?
  2. So named because the founders wanted to be the first company with an emoji for a stock ticker symbol. This did not happen.
  3. Although this person argues that was a bizarre assumption and that there should have been easier ways to find the key.

Update: Fixed missing URL.

July 11, 2026

British censorship laws do not apply outside the UK’s jurisdiction

Filed under: Britain, Law, Liberty, Media, Technology, USA — Tags: , , — Nicholas @ 05:00

On Substack Notes, Lorenzo Warby links to a fascinating discussion about the ongoing struggle between the UK government’s Ofcom and the US-based 4chan and their legal representatives, saying “The totalitarian wannabes currently running the UK do not apparently grasp that the American Revolution and War of Independence was a thing. Also, being totalitarian wannabes, they have no sense of humour.”

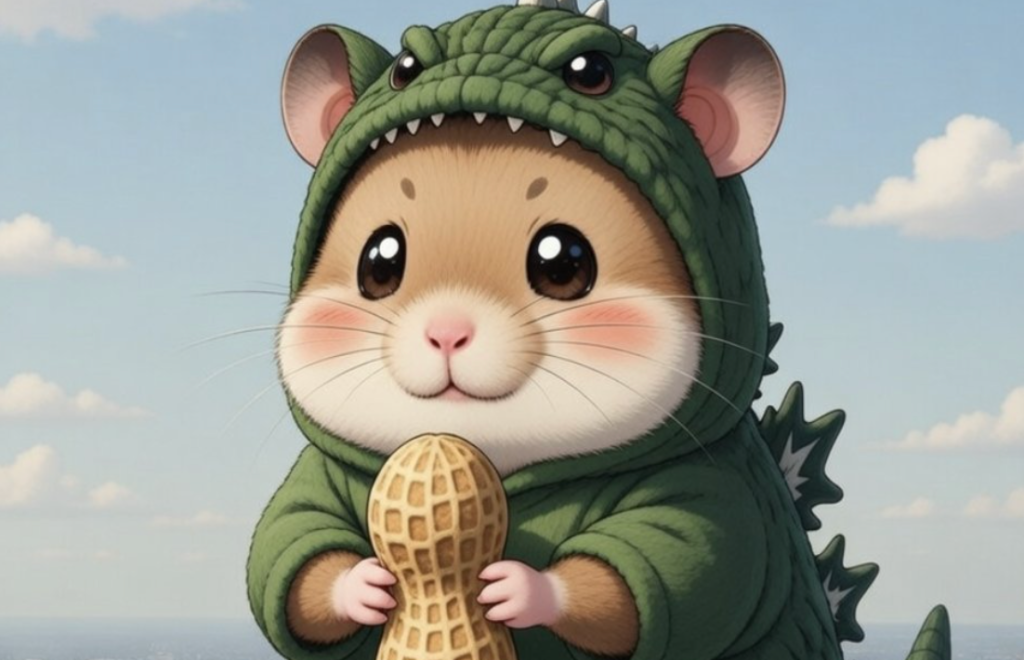
A UK cabinet minister, Rt. Hon. Liz Kendall MP, Secretary of State for the Department of Science, Innovation and Technology (“DSIT”), discussed the infamous “hamster e-mail” I sent on behalf of my client 4chan to the UK’s Internet censor, on national radio today in the UK. […] My father always told me, when I was growing up, “when a cabinet minister holding the technology policy brief for a G7 Member State is talking about your e-mailed jokes to an audience of millions on national broadcast media, that is the right time to explain the joke, especially if the cabinet minister didn’t get the joke”.

That explanation follows.

The backstory – Hamster #1

The hamster joke has a bit of a history to it. Ofcom, the UK’s Internet censor, first made contact with my American client 4chan in June of 2025 in its attempt to impose British censorship law on that website. I was subsequently retained as defense counsel, pro bono.

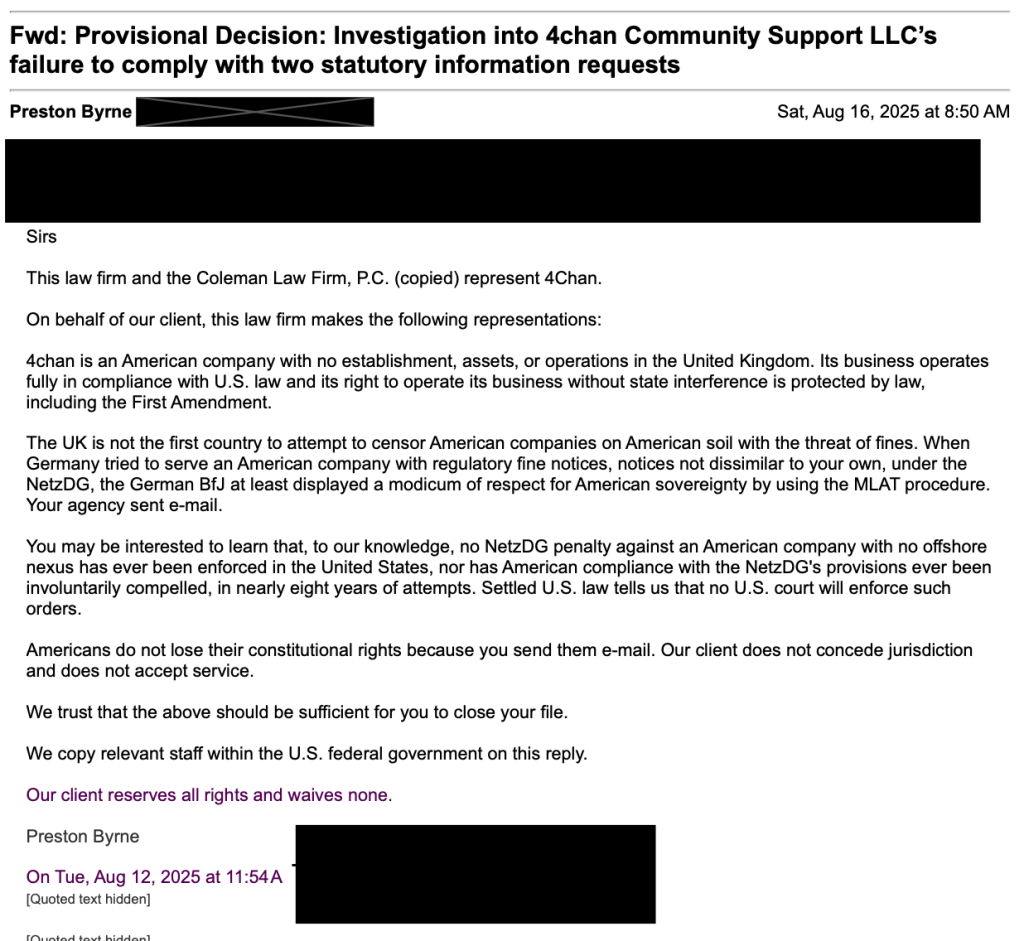
Ofcom then “provisionally fined” 4chan on August 16th, 2025 for refusing to obey the UK’s censorship regime. We were invited to make representations to the regulator following that provisional fine decision.

We did two things in response to that. The most newsworthy response was to file a lawsuit against the regulator in the DDC. Before that, however, we explained our position to Ofcom in writing and gave them an opportunity to walk away:

To wit, Ofcom’s fine notices were not properly served and were not enforceable in the United States. Note that we also gave Ofcom fair notice that while this might have been their first attempt to enforce their censorship orders in America, this was not our first rodeo when it came to successfully refusing such orders.

No quantity of officious and haughty foreign demand letters will change our stance. The UK could even pass a bill of attainder – historically Parliament’s most extreme and powerful legislative weapon – against my client, for all I care. My client’s right to operate its service lawfully in the United States is protected by the First Amendment. There is no law Parliament could enact that would change that fact.

I am very familiar with how this movie ends, and it does not end with 4chan paying Ofcom’s fine.

It may end with the UK’s censors getting a blocking order that it serves on its own ISPs; that would be the UK visibly censoring its own people, rather than censoring my client, and doing so ineffectively, at that, as ISP blocks can be circumvented with a VPN. That is a consequence my client is prepared to accept.

England might have the Online Safety Act, but the United States has the U.S. Constitution. These rulesets do not override each other; they are, rather, mutually exclusive. In America’s domain, the Online Safety Act essentially doesn’t exist. It has about as much legal force as a pile of shredded paper one might use to line a hamster’s cage.

Peace was always an option here, but that would have required the UK to abandon the fiction that its rules override the U.S. Constitution on U.S. soil, which we are not prepared to accept.

My clients did not start this fight, but by golly we do intend to finish it.

My client sued Ofcom two weeks later.

There’s much more, so do read the whole thing.

Don’t boast about your online pirating skillz

Filed under: Books, Business, Law, Media, Technology — Tags: , , — Nicholas @ 03:00

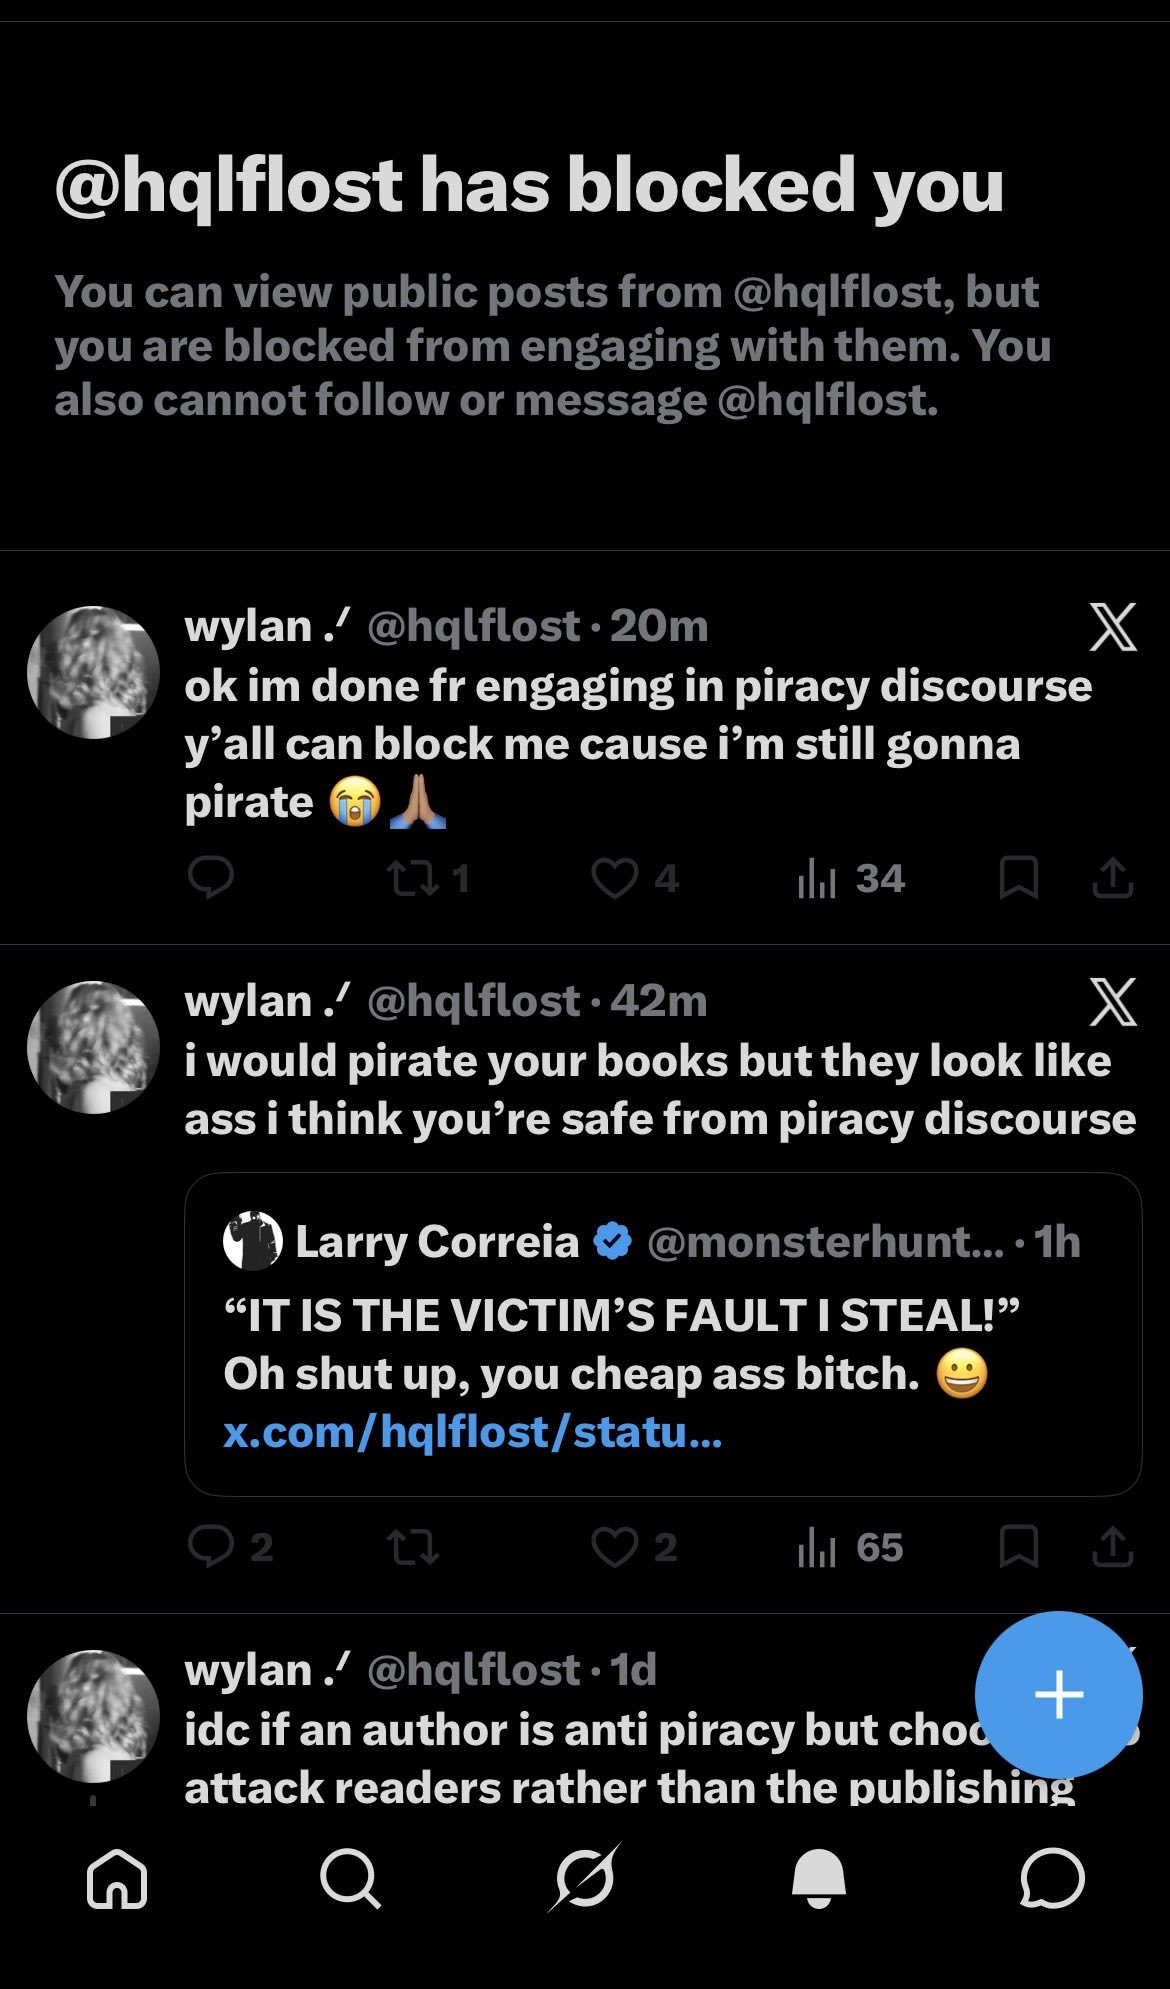
Larry Correia interacts with a proud book pirate on the social media site formerly known as Twitter:

You’d better run, pussy. 😀

Listen, authors are gonna get pirated. We know this. I don’t freak out about it.

But if you are gonna steal, just admit you are a thief and own it. Don’t make a bunch of bullshit posturing excuses why it’s the victim’s fault you’re robbing him. Spare us your commie manifesto about the poor and oppressed, and how you are so brave to stand up for the masses against those cruel wealthy authors taking advantage of the poor (and for most writers, lol wut? They are broke, dummy!)

BUT WHAT ABOUT TEH POORS?!?

Go to the library!

But then we have to listen to these thieving shit weasel cry but what about the RURAL POOR. Which extra fucking pisses me off because now they’re appropriating my culture, because I grew up poor in the sticks. And I choose to live in the country now. Fuck your commie gibberish. Rural people are used to driving long distances to do everything.

Reading is like the cheapest hobby! If you are pirating you are rich enough to have internet.

You aren’t Robin Hood. You’re just a cheap bitch. There’s tons of free books online. My “greedy corporate oligarch” publisher Baen has a free online library with hundreds of titles.

Or KU is like $12 a month for UNLIMITED books. You can read 20 hours a day for a few cents an hour if you feel like it.

If you want to steal, great. Whatever. I don’t give a shit. That’s on you. But just do it with some fucking dignity and spare us from this retarded class warfare justification bullshit. That’s way more pathetic than being a thief.

July 10, 2026

EU “Chat Control” passes through parliamentary chicanery

Filed under: Europe, Government, Law, Liberty, Media — Tags: , , , , , — Nicholas @ 04:00

As mentioned yesterday, the EU introduced “Chat Control” which allows the authorities to examine any and all private communications by EU residents “to protect the children”. As eugyppius reports, it got through and was passed into EU-wide law on Thursday:

If anybody cares, what actually happened is that an extension of the European Union’s mass surveillance regulation known as Chat Control 1.0 failed to make it out of the European Parliament twice in March. Unable to summon a clear parliamentary majority, advocates (mostly in the centre-right European People’s Party [EPP]) turned to the European Council, which adopted the failed Chat Control 1.0 renewal on 2 July. The Council’s position hardens automatically into law unless the European Parliament can summon an absolute majority to stop it. To forestall any such majority from forming, the EPP on Tuesday moved with member state backing for urgent procedure, angling to force their scheme through in the last days before the summer holiday, after many MEP’s had already left. The parliament narrowly approved the urgent procedure, and in consequence there were not enough votes to stop Chat Control 1.0 when it came for a vote today. Hours ago, a majority of 314 MEPs voted to stop Chat Control against the wishes of the Council, while a minority of 276 voted to let it happen. Because 314 is less than the absolute majority of 361, Chat Control 1.0 passed even though most MEPs present didn’t want it to.

It was a sleazy vote, not least because it’s far from clear this procedural manoeuvre was even appropriate in this case. Also, electronic surveillance is bad, but if we are honest with ourselves this battle was already lost.

Chat Control 1.0 was first instated in 2021 as a temporary exemption to the ePrivacy Directive of the EU, allowing messaging services and online platforms to scan chats and other electronic communications for child sexual abuse material. The exemption expired in April, but various platforms have continued their surveillance with no legal basis in the intervening months. Now their formal permission to scan our private communications has been restored and extended through April 2028. We are, in other words, merely returning to the prior regime.

Chat Control 1.0 is a temporary stopgap while the European Parliament, the Commission and the Council try to negotiate their Child Sexual Abuse Regulation, or Chat Control 2.0. As envisioned by the Commission, this permanent law would not merely allow platforms to scan private communications for child sex abuse material, but require them to do so; require additional AI-assisted automated scanning not only for known child pornography but also for such vaguely defined activities as “grooming”; and extend scanning to end-to-end encrypted services like Signal via mandatory monitoring on the client side. This insane proposal has been watered down over the years, in large part because of parliamentary opposition, but it’s coming in some form. We’re getting Chat Control 2.0 before Chat Control 1.0 expires, and Chat Control 2.0 will be at least somewhat worse.

July 9, 2026

They call it “Chat Control”

Filed under: Europe, Government, Law, Liberty, Media — Tags: , , , , , , — Nicholas @ 04:00

On the social media site formerly known as Twitter, Brivael Le Pogam talks about what the EU is calling “Chat Control”:

We need to talk about Chat Control, because it’s all happening this week and almost no one understands what it’s about.

In plain terms: the EU wants to authorize the scanning of your private messages. Your WhatsApp conversations, your emails, your DMs. Not those of a suspect. Those of everyone, all the time, by default.

The pretext is airtight, and that’s the trap: “protecting children”. No one can be against that. That’s exactly why it’s the perfect tool. They’ll never get you to swallow mass surveillance in the name of mass surveillance. They’ll get you to swallow it in the name of children, terrorism, disinformation. Always some cause you won’t dare challenge.

Understand the two-step mechanism well.

Today it’s the “soft” version: platforms have the right to scan, on a voluntary basis, unencrypted messages. Harmless on the surface. It’s the foot in the door.

Then comes the real version, the one under negotiation: mandatory scanning, including of your encrypted messages, analyzed directly on your phone before they’re even sent. Over 500 cryptographers have signed a letter saying it’s technically unfeasible without creating security vulnerabilities that any hacker or hostile state could exploit. You’re breaking encryption for everyone, including the criminals you claim to be targeting.

And the worst part isn’t even that.

The real danger isn’t that Brussels technocrats will be watching you tomorrow. They’re probably too spineless for that. The danger is that they’re building the infrastructure. Once scanning everyone’s messages becomes normal, legal, operational — the track is laid. And on that track will roll everything that comes next. The day a crisis brings ruthless people to power, they won’t have to invent anything. The machine will already be there, ready to go.

No surveillance infrastructure has ever stayed limited to its original purpose. None. It’s a law of administrative nature: a tool built for X always ends up serving Y.

What makes this text dangerous isn’t what it does today. It’s what it makes possible forever.

The decisive vote is Thursday. The last lock.

Auto-translated from the original French by X.

The good folks at Windscribe weigh in:

The EU is not a democracy.

They’re closer to a guy who keeps pressuring a girl to sleep with him despite her saying no.

5 times now.

But he won’t stop.

We’re at the stage where he’s giving her alcohol and making her drunk so she struggles to say no.

Over the last 3 years, Chat Control and similar scanning measures have been defeated or blocked 5 times.

The citizens of the EU and members of EU Parliament have made it abundantly clear — they don’t want Chat Control.

This latest attempt by the EU is the slimiest one yet. Revive dead legislation that was already defeated, flip the passing criteria so that majority don’t need to SUPPORT it, majority need to DEFEAT it, and as the cherry on top, hold that vote on the very last day before Parliament members go on summer break so that many don’t show up. Oh and if they don’t show up, it counts as a vote to pass Chat Control.

You can dress it up in as many legal technicalities and loopholes as you want, what the EU is doing here is fundamentally undemocratic.

No means no.

And if you ever saw a guy pressuring a girl into sleeping with him with disgusting tactics after she said no THIS many times, you would consider him to be a rapist.

So congrats to the EU on adopting rapist strategies to your governance.

June 30, 2026

Leading the grassroots revolt against AI … Homer Simpson

Filed under: Business, Media, Technology, USA — Tags: , , , — Nicholas @ 04:00

Ted Gioia posted this a couple of days back, but if you haven’t read it it’ll still be new to you:

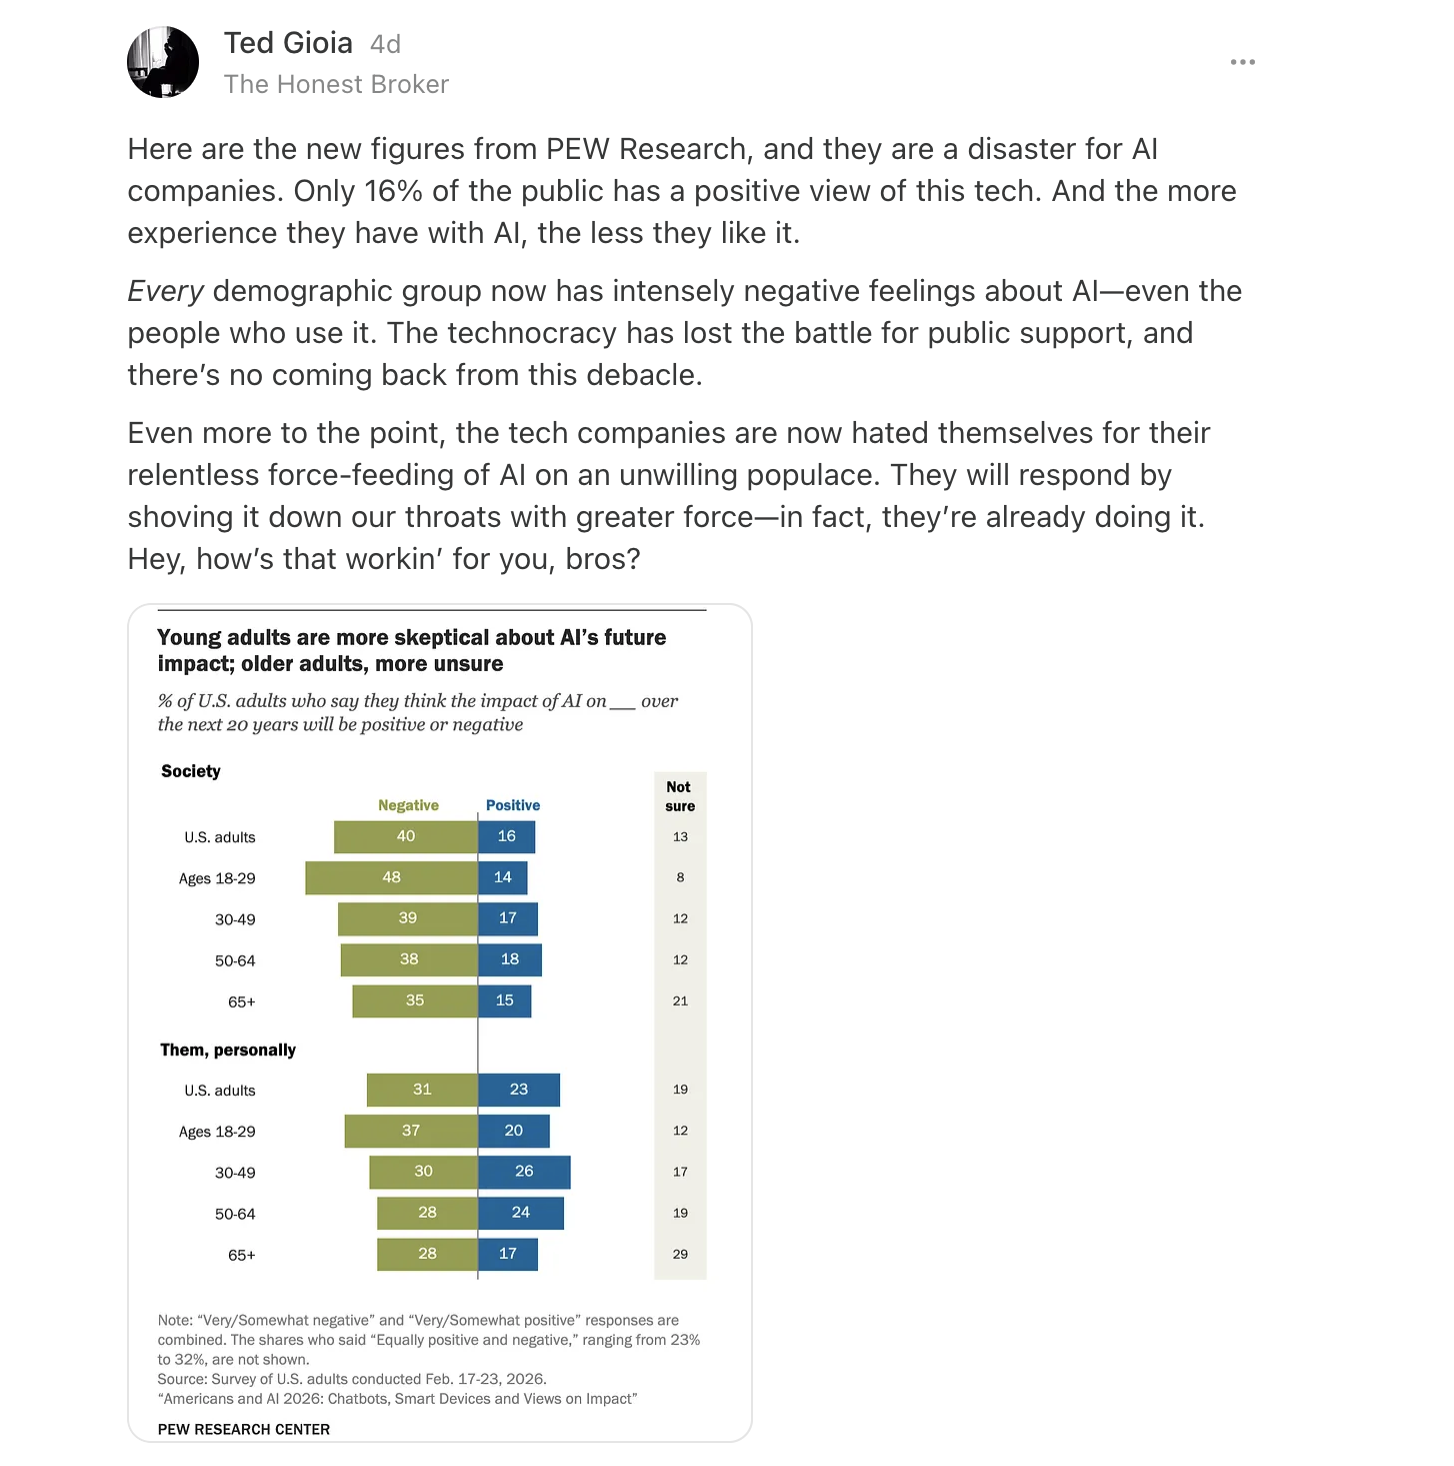
Last November I suggested that 2026 would witness a tech backlash of unprecedented intensity. And it’s now happening with a vengeance. Silicon Valley is getting skewered everywhere, and to a degree inconceivable just a short while ago.

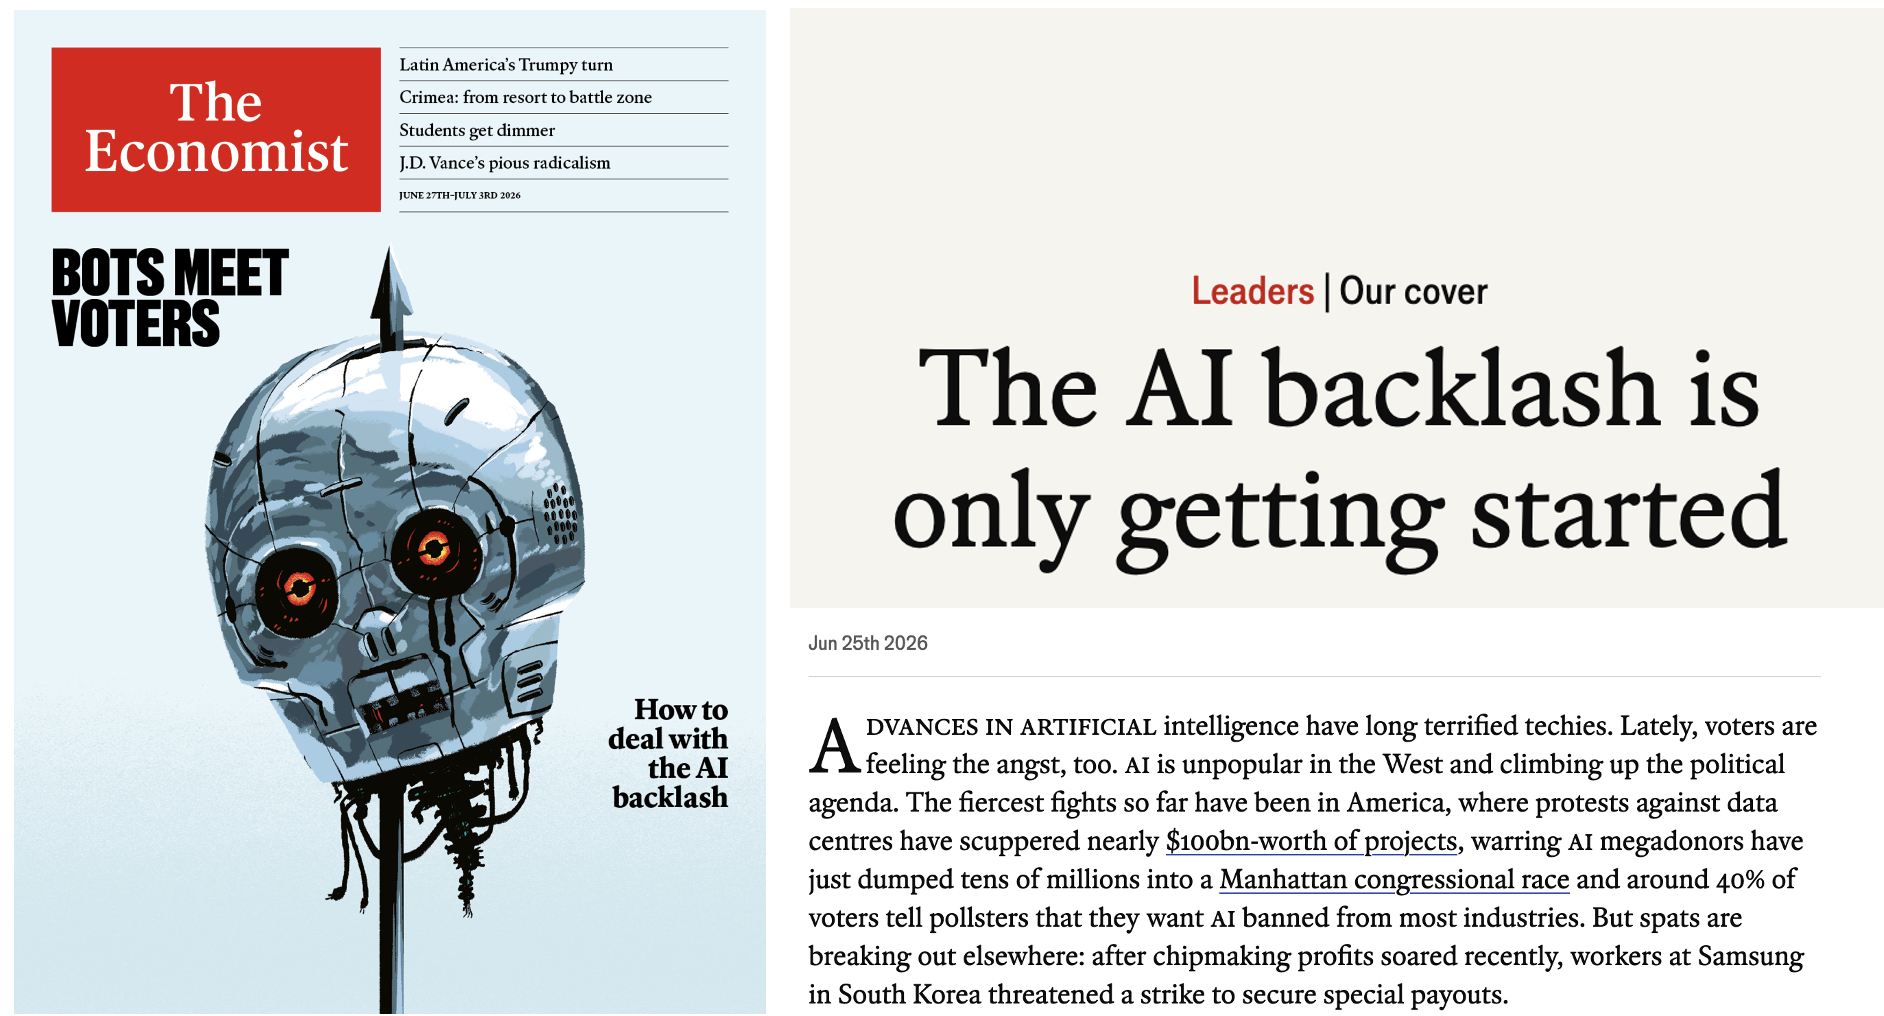
Just yesterday, The Economist finally grasped how rapidly tech antipathy is mounting — and made AI backlash its cover story.

The latest survey numbers are devastating. Every demographic group is now opposed to AI—especially young people, previously the most enthusiastic supporters of new tech.

[…]

Not every pushback to encroaching tech is quite so gentle.

Consider the case of “Mr. Daniels,” a 25-year-old man from England. He knows that AI will rob every music file on the web for training — so he decided to poison the data.

How did he do it? According to Tuned Into Tech, it happens like this:

    He took his entire music library of 2,000 records, stripped out the original vocals, and replaced every single one of them with the voice of Homer Simpson. Then he uploaded all of them to Soulseek. He didn’t change the metadata, the file names, the artist tags, the album information. They all stayed exactly the same.

A listener might not notice at first. Some of these songs have long intros, and those are unchanged. But as soon as the singing begins, Homer Simpson takes over. When AI tries to steal this for training, it gets fooled—and contaminates its own data set.

    So somewhere deep in a training algorithm’s data set is the audio of Homer Simpson which the AI will assume sounds like [for example] Madonna, Rihanna, or maybe even Sean Paul. The model doesn’t know the difference. It just ingests the data and treats that like the truth.

    And that is exactly what Mr. Daniels is hoping for.

He wants “to introduce noise, chaos” into the bots that are putting human musicians out of work.

“Mr. Daniels” is not an isolated example. Musician Benn Jordan has also been “poison-pilling” music files in hopes of disrupting AI.

In recent months, he has watched in horror as “tech companies started raising millions of venture capital dollars and scraping my music without my consent”. They now use his own work to generate “shittier music with it that is inadvertently associated with my name — and then attempting to resell that in the same economy in which I make money from my music”.

As a result, he has stopped releasing music. But he hasn’t walked away from the battle — instead Jordan has developed “a type of encoding that not only makes a music file more or less untrainable by generative AI companies, but actually has the ability to decrease the quality and efficiency of their entire data set”.

“Unethical generative AI companies have made artists feel incredibly powerless for quite some time now”, he adds, “but all of that is about to change”.

Older Posts »

Powered by WordPress