Quotulatiousness

March 3, 2014

The origins of hacking and the myth of a lost Eden of open source code

Filed under: History, Technology — Tags: , , , — Nicholas @ 09:40

Gather round you kids, ’cause Uncle Eric is going to tell you about the dim, distant days of hacking before open source:

I was a historian before I was an activist, and I’ve been reminded recently that a lot of younger hackers have a simplified and somewhat mythologized view of how our culture evolved, one which tends to back-project today’s conditions onto the past.

In particular, many of us never knew – or are in the process of forgetting – how dependent we used to be on proprietary software. I think by failing to remember that past we are risking that we will misunderstand the present and mispredict the future, so I’m going to do what I can to set the record straight.

[…]

Without the Unix-spawned framework of concepts and technologies, having source code simply didn’t help very much. This is hard for younger hackers to realize, because they have no experience of the software world before retargetable compilers and code portability became relatively common. It’s hard for a lot of older hackers to remember because we mostly cut our teeth on Unix environments that were a few crucial years ahead of the curve.

But we shouldn’t forget. One very good reason is that believing a myth of the fall obscures the remarkable rise that we actually accomplished, bootstrapping ourselves up through a series of technological and social inventions to where open source on everyone’s desk and in everyone’s phone and ubiquitous in the Internet infrastructure is now taken for granted.

We didn’t get here because we failed in our duty to protect a prelapsarian software commons, but because we succeeded in creating one. That is worth remembering.

Update: In a follow-up post, ESR talks about closed source “sharecroppers” and Unix “nomads”.

Like the communities around SHARE (IBM mainframe users) and DECUS (DEC minicomputers) in the 1960s and 1970s, whatever community existed around ESPOL was radically limited by its utter dependence on the permissions and APIs that a single vendor was willing to provide. The ESPOL compiler was not retargetable. Whatever community developed around it could neither develop any autonomy nor survive the death of its hardware platform; the contributors had no place to retreat to in the event of predictable single-point failures.

I’ll call this sort of community “sharecroppers”. That term is a reference to SHARE, the oldest such user group. It also roughly expresses the relationship between these user groups and contributors, on the one hand, and the vendor on the other. The implied power relationship was pretty totally asymmetrical.

Contrast this with early Unix development. The key difference is that Unix-hosted code could survive the death of not just original hardware platforms but entire product lines and vendors, and contributors could develop a portable skillset and toolkits. The enabling technology – retargetable C compilers – made them not sharecroppers but nomads, able to evade vendor control by leaving for platforms that were less locked down and taking their tools with them.

I understand that it’s sentimentally appealing to retrospectively sweep all the early sharecropper communities into “open source”. But I think it’s a mistake, because it blurs the importance of retargetability, the ability to resist or evade vendor lock-in, and portable tools that you can take away with you.

Without those things you cannot have anything like the individual mental habits or collective scale of contributions that I think is required before saying “an open-source culture” is really meaningful.
February 21, 2014

Online bounty hunting

Filed under: Business, Gaming, Law, Technology — Tags: , , — Nicholas @ 09:10

BBC News on a bounty being offered to track down and prosecute those involved in the DDoS attack on the game Wurm:

A bounty of 10,000 euros (£8,200) is being offered to catch the people who took the online multiplayer game Wurm offline.

The game’s servers were victim of a distributed denial of service (DDoS) attack this week and the game remains offline.

A DDoS attack forces a website offline by overloading the site’s servers with more data than it can process.

The bounty is being offered for any “tips leading to a conviction”.

Wurm is a massively multiplayer online role-playing game (MMORPG) that is played on personal computers.

The game takes place in virtual realms and everything in it is created by the players who are taking part. They can compete against each other or combine forces to defend a realm.

The attack happened just after an update to the game.

Writing on Wurm‘s website, one of its creators said it would be back online as soon as possible.

“We were the target of a DDoS attack and our hosting provider had to pull us off the grid for now.

“We will be back as soon as possible, but things are out of our hands since their other customers are affected.

“We can offer 10,000 euros for any tips or evidence leading to a conviction of the person responsible for this attack,” he wrote.

H/T to Hunter for the link.

February 20, 2014

Anti-tobacco campaigners – “a great bunch of puritanical Cnuts”

Filed under: Britain, Business, Health, Technology — Tags: , , , , — Nicholas @ 08:37

In sp!ked, Rob Lyons looks at the way e-cigarettes are being marketed in the UK and how it’s driving anti-tobacco campaigners absolutely insane:

For the tobacco-control lobby, an advert like Dorff’s is an absolute nightmare. It makes no health claims. It is clearly targeted at adults. It plays to the fact that even smokers dislike aspects of old-fashioned cigarettes, and are happy to compromise in order to get most of the pleasure of smoking without the hassle or the irritation to others. And then – God forbid – it even plays to the annoyance of smokers at the health fanatics. The last thing smoke dodgers want is for anyone to be able to take their freedom back. Even the existence of the sanitised offer from Vype’s say-nothing advert is anathema.

This was made abundantly clear in a report published by Cancer Research UK last year, The marketing of electronic cigarettes in the UK [PDF]. The authors are forced to admit that e-cigs ‘are accepted as being much safer than their conventional equivalents, so if smokers can be encouraged to switch there is the potential for significant public health gain’.

However, this message is quickly lost in a cloud of public-health cant. The threats, say the authors, include concerns that ‘hard-won tobacco-control policies (smokefree public places, the ad ban, age restricted sales, tobacco industry denormalisation, POS [point-of-sale] restrictions) are being undermined’ and that ‘there is evidence that young people, who have always been the key to the long-term viability of the tobacco industry, may be being pulled into the market’. The danger, say the authors, is that tobacco companies don’t want you to give up your addiction, just switch to a different delivery system. The problem with this argument is that the new delivery system is much, much safer. Why shouldn’t corporations try to sell us safe products?

[…]

In reality, what the anti-tobacco lobbyists (and their fans in Westminster and Whitehall) are really afraid of is the loss of their power and influence over our lives. They fear they will be helpless against the tide of e-cigs, like a great bunch of puritanical Cnuts. (Note to sub-editor: that’s definitely ‘Cnuts’, as in the Danish king who famously – probably apocryphally – tried to turn back the sea. Honest.)

E-cigs are a safe, practical alternative to smoking. For all the huffing and putting-a-stop-to-puffing, tobacco control has been an illiberal failure. E-cigs are encouraging smokers to switch, cut down or stop altogether far more successfully than all the bans, taxes, restrictions and useless nicotine-replacement therapies that have gone before. ‘Vaping’ is an unexpected but nonetheless happy success story.

February 17, 2014

Looking forward by looking backward – military evolution

Filed under: History, Military, Technology, Weapons — Tags: , , , — Nicholas @ 11:52

Strategy Page discusses the problems of predicting the future … which isn’t just a task for science fiction writers:

How will warfare change in the next 30 years? Military leaders, and the people they protect, are always trying to figure this out. There’s an easy way to get some good insight on the future. Simply go back 120 years (1894) and note the state of warfare and military technology at the time, then advance, 30 years at a time, until you reach 2014. At that point, making an educated guess at what 2044 will be like will like will be, if not easy, at least a lot less daunting.

In 1894, many infantry were still using single shot black powder rifles. Change was in the air though, and the United States had just begun to adopt the newfangled smokeless powder, a few years after it became widely available. In 1894 American troops were still replacing their black power rifles with a smokeless powder model (the Krag-Jorgensen). The modern machine-gun had been invented in 1883 but armies took about two decades before they began adopting them on a large scale. Most artillery was still short ranged, not very accurate, and could only fire at targets the crew could see. Horses pulled or carried stuff and the infantry marched a lot when they were not being moved long distances by railroad or steamships. But the modern, quick-firing artillery was recently introduced and still unproven in battle. Communications still relied on the telegraph, a half century old invention that revolutionized, in only a few decades, the way commanders could talk to each other over long distances. They could now do it in minutes. This was a big change for warfare. Very big. At this time telephones were all local and not portable. Cavalry was still important for scouting, although less useful for charging infantry (a trend that began when infantry got muskets with bayonets two centuries earlier).

[…]

So what does this portend for 2044? Faster and deadlier, for sure. Information war will be more than a buzzword by then because better sensors and data processing technology will make situational awareness (knowing where you and your enemy are, knowing it first, and acting on it before the other guy does) more decisive than ever.

If the expected breakthrough in batteries (fuel cells) evolves as reliably and cheaply as expected, the 2040s infantryman will be something of a cyborg. In addition to carrying several computers and sensor systems, he might wear body armor that also provides air conditioning. Satellite communications, of course, and two way video. Exoskeletons are already in the works and may mature by then. A lot depends on breakthroughs in battery tech although engineers are also finding to do more with just a little juice. Historians tend to constantly underestimate the cleverness of engineers and inventors in general.

But the big new development will be the continued evolution of robotic weapons. The World War II acoustic torpedo (used by the Germans and the allies, from subs as well as the air) was the first truly robotic weapon. You turned it lose and it would hunt down its prey and attack. There may be a lot of public uproar over land based systems that have sensors, can use them to hunt, and have weapons that can be used without human intervention. But those systems will be easy and cheap to build by 2044, and as soon as one nation builds them others will have to follow. By 2044, machines will be fighting other machines more often than they will be looking for the stray human on the battlefield.

But there will be other developments that are more difficult to anticipate. In 1894 most of the 1924 technologies were already known in a theoretical sense. Same with the 1954 technologies in 1924 and so on. What is most difficult to predict is exactly how new tech will be employed. There will be imagination and ingenuity involved there, and that sort of thing is, by its very nature, resistant to prediction.

February 15, 2014

South Korea’s high-speed broadband (censored) internet

Filed under: Asia, Technology — Tags: , , — Nicholas @ 10:43

The Economist looks at the gosh-wow technical specs of South Korean internet access, governed by the sensibilities of a restrictive, censorious regime:

Why South Korea is really an internet dinosaur

SOUTH KOREA likes to think of itself as a world leader when it comes to the internet. It boasts the world’s swiftest average broadband speeds (of around 22 megabits per second). Last month the government announced that it will upgrade the country’s wireless network to 5G by 2020, making downloads about 1,000 times speedier than they are now. Rates of internet penetration are among the highest in the world. There is a thriving startup community (Cyworld, rolled out five years before Mark Zuckerberg launched Facebook, was the most popular social network in South Korea for a decade) and the country leads the world in video games as spectator sports. Yet in other ways the futuristic country is stuck in the dark ages. Last year Freedom House, an American NGO, ranked South Korea’s internet as only “partly free”. Reporters without Borders has placed it on a list of countries “under surveillance”, alongside Egypt, Thailand and Russia, in its report on “Enemies of the Internet”. Is forward-looking South Korea actually rather backward?

Every week portions of the Korean web are taken down by government censors. Last year about 23,000 Korean webpages were deleted, and another 63,000 blocked, at the request of the Korea Communications Standards Commission (KCSC), a nominally independent (but mainly government-appointed) public body. In 2009 the KCSC had made just 4,500 requests for deletion. Its filtering chiefly targets pornography, prostitution and gambling, all of which are illegal in South Korea. But more wholesome pursuits are also restricted: online gaming is banned between midnight and 6am for under-16s (users must input their government-issued ID numbers to prove their age). Sites from North Korea, including its state newspaper, news agency and Twitter feed, are blocked, as are those of North Korea’s sympathisers. A law dating back to the Korean war forbids South Korean maps from being taken out of the country. Because North and South are technically still at war, the law has been expanded to include electronic mapping data—which means that Google, for instance, cannot process South Korean mapping data on its servers and therefore cannot offer driving directions inside the country. In 2010 the UN determined that the KCSC “essentially operates as a censorship body”.

February 11, 2014

Michael Geist on what Canadians can do about mass surveillance

Filed under: Cancon, Government, Liberty, Technology — Tags: , , — Nicholas @ 12:21

A post at Michael Geist’s website advises Canadians about their options to protest the government’s role in internet surveillance:

… we know that U.S. law provides fewer protections to personal information of non-U.S. citizens, suggesting that Canadian data residing in cloud-based servers in the U.S. are particularly vulnerable. Meanwhile, the Canadian legal rules remain largely shrouded in secrecy, with officials maintaining that programs fall within the law despite the obvious privacy interests in metadata and statutory restrictions on domestic surveillance.

[…]

Today is the day that Canadians can send a message that this official is wrong. The Day We Fight Back Against Mass Surveillance is a global effort to galvanize people around the world to speak out against ubiquitous surveillance. Canadians can learn more here, but the key ask is to contact your Member of Parliament. If you are concerned with widespread surveillance in Canada, take a couple of moments to send an email or letter (no stamp required) to your MP and let them know how you feel (alternatively, you can fill out the form at this site). In addition, you can sign onto a global petition supported by hundreds of groups around the world.

I’ve written about the need for changes here and many others — including Interim Privacy Commissioner Chantal Bernier, Kent Roach, Wesley Wark, Ron Diebert, David Fraser, Ontario Privacy Commissioner Ann Cavoukian and Avner Levin, Craig Forcese, and Lisa Austin — have highlighted other potential changes. There are no shortage of ideas for reform. What we need now are Canadians to speak out to demand an open review and reform of Canadian surveillance law and policy.

February 9, 2014

“A car is a mini network … and right now there’s no security implemented”

Filed under: Technology — Tags: , , , — Nicholas @ 11:48

Driving your car anywhere soon? Got anti-hacking gear installed?

Spanish hackers have been showing off their latest car-hacking creation; a circuit board using untraceable, off-the-shelf parts worth $20 that can give wireless access to the car’s controls while it’s on the road.

The device, which will be shown off at next month’s Black Hat Asia hacking conference, uses the Controller Area Network (CAN) ports car manufacturers build into their engines for computer-system checks. Once assembled, the smartphone-sized device can be plugged in under some vehicles, or inside the bonnet of other models, and give the hackers remote access to control systems.

“A car is a mini network,” security researcher Alberto Garcia Illera told Forbes. “And right now there’s no security implemented.”

Illera and fellow security researcher Javier Vazquez-Vidal said that they had tested the CAN Hacking Tool (CHT) successfully on four popular makes of cars and had been able to apply the emergency brakes while the car was in motion, affect the steering, turn off the headlights, or set off the car alarm.

The device currently only works via Bluetooth, but the team says that they will have a GSM version ready by the time the conference starts. This would allow remote control of a target car from much greater distances, and more technical details of the CHT will be given out at the conference.

February 7, 2014

Hackers, “technologists”, … and girls

Filed under: Technology — Tags: , , , , — Nicholas @ 13:35

An interesting post by Susan Sons illustrating some of the reasons women do not become hackers in the same proportion that men do:

Looking around at the hackers I know, the great ones started before puberty. Even if they lacked computers, they were taking apart alarm clocks, repairing pencil sharpeners or tinkering with ham radios. Some of them built pumpkin launchers or LEGO trains. I started coding when I was six years old, sitting in my father’s basement office, on the machine he used to track inventory for his repair service. After a summer of determined trial and error, I’d managed to make some gorillas throw things other than exploding bananas. It felt like victory!

[…]

Twelve-year-old girls today don’t generally get to have the experiences that I did. Parents are warned to keep kids off the computer lest they get lured away by child molesters or worse — become fat! That goes doubly for girls, who then grow up to be liberal arts majors. Then, in their late teens or early twenties, someone who feels the gender skew in technology communities is a problem drags them to a LUG meeting or an IRC channel. Shockingly, this doesn’t turn the young women into hackers.

Why does anyone, anywhere, think this will work? Start with a young woman who’s already formed her identity. Dump her in a situation that operates on different social scripts than she’s accustomed to, full of people talking about a subject she doesn’t yet understand. Then tell her the community is hostile toward women and therefore doesn’t have enough of them, all while showing her off like a prize poodle so you can feel good about recruiting a female. This is a recipe for failure.

[…]

I’ve never had a problem with old-school hackers. These guys treat me like one of them, rather than “the woman in the group”, and many are old enough to remember when they worked on teams that were about one third women, and no one thought that strange. Of course, the key word here is “old” (sorry guys). Most of the programmers I like are closer to my father’s age than mine.

The new breed of open-source programmer isn’t like the old. They’ve changed the rules in ways that have put a spotlight on my sex for the first time in my 18 years in this community.

When we call a man a “technologist”, we mean he’s a programmer, system administrator, electrical engineer or something like that. The same used to be true when we called a woman a “technologist”. However, according to the new breed, a female technologist might also be a graphic designer or someone who tweets for a living. Now, I’m glad that there are social media people out there — it means I can ignore that end of things — but putting them next to programmers makes being a “woman in tech” feel a lot like the Programmer Special Olympics.

February 6, 2014

TAFTA/TTIP – The US is negotiating from a position of unassailable strength

Filed under: Europe, Technology, USA — Tags: , , , , , — Nicholas @ 11:02

At Techdirt, Glyn Moody explains why the EU is insane not to demand that the negotiations with the US government over TAFTA/TTIP be made fully public:

On the one side is the US, on the other, the 28 nations that go to make up the European Union. Because they have differing views on the TAFTA/TTIP negotiations, it’s necessary to pass around many documents conveying information about the current negotiations, and seek to obtain some kind of consensus on future EU proposals and flexibilities.

In the wake of Snowden’s revelations, security will doubtless be much better than during the Copenhagen Summit, when supposedly secret messages were sent using unencrypted emails. But it only needs one weak link in the European Union’s security chain — somebody who forgets to encrypt his or her message, or who leaves it on a system that has been compromised — and the NSA will be able to access that information, and pass it on to the US negotiators, just as it did in Copenhagen.

The key point is that there is a profound information asymmetry in the TAFTA/TTIP talks. Although the spy agencies of the EU countries will doubtless be trying their best to obtain confidential information about US negotiating tactics, it will be much harder than it is for the US to do the same about EU positions. That’s because the NSA is far larger, and far more expert than the EU agencies. GCHQ is probably the nearest in terms of capabilities, but is so closely allied with the NSA in other areas that it probably won’t be trying too hard so as not to annoy its paymaster.

This more or less guarantees that the US will know everything about the EU’s negotiating plans during TAFTA/TTIP, while the EU will remain in the dark about the US intentions. That not only undercuts the European Commission’s argument that releasing documents is not possible because they must remain secret during the negotiations — they won’t be — it also gives the EU a huge incentive to insist on full transparency for the talks. That way, the EU negotiators would be able to see at least some US documents that currently are hidden from them, whereas the US would gain little that it didn’t already know through more dubious means.

E-cigarettes – growth industry or doomed by regulatory overstretch

Filed under: Business, Health, Technology — Tags: , , , — Nicholas @ 09:03

Megan McArdle discusses the past, present, and potential future for the e-cigarette industry:

In its simplest form, an e-cigarette is a cartridge filled with a nicotine solution and a battery powering a coil that heats the solution into vapor, which one sucks in and exhales like smoke. Typically, it looks like a regular cigarette, except the tip, embedded with an LED, often glows blue instead of red. The active ingredient in e-cigarettes is the same nicotine found in cigarettes and nicotine patches.

The effects of inhaling nicotine vapor are not totally understood, but there is no evidence to date that it causes cancer. Experts and logic seem to agree that it’s a lot better than setting chopped-up tobacco leaves on fire and inhaling the nicotine along with thousands of combustion byproducts, some of which are definitely carcinogenic. Because cancer is the main drawback of smoking for a lot of people, the delivery of nicotine without lighting a cigarette is very attractive. And because it produces a wispy vapor instead of acrid smoke, an e-cigarette lets you bring your smoking back indoors, where lighting up in an enclosed space is no longer socially, or legally, acceptable.

[…]

A primitive, battery-operated “smokeless non-tobacco cigarette” was patented as early as 1963 and described in Popular Mechanics in 1965. Thomas Schelling, a Nobel prize-winning economist who helped start the Institute for the Study of Smoking Behavior and Policy at Harvard University’s Kennedy School in the 1980s, recalls that people in the 1960s were talking about a charcoal-based vaporizer that would heat some sort of nicotine solution. While those early versions might have been safer than a regular cigarette, they were too expensive and cumbersome to become a substitute for a pack of Camels in a country where, as Schelling notes, “you’re never more than 5 or 10 minutes away from a smoke.”

In a way, electronic cigarettes were made possible by cell phones. The drive to make phones smaller and lengthen their battery life led to the development of batteries and equipment small enough to fit in a container the size and shape of a cigarette. There’s some dispute over who invented the modern e-cigarette, but the first commercially marketed device was created by a Chinese pharmacist, Hon Lik, and introduced to the Chinese market as a smoking cessation device in 2004.

In the same way that alcohol comes in various guises (many carefully crafted to appeal to beginners: sweet as soda pop, for example), e-cigarettes are available in many different flavours:

E-cigarette cartridges come in classic tobacco and menthol flavors — Verleur’s company even offers V2 Red, Sahara, and Congress, clearly aimed at loyal smokers of Marlboros, Camels, and Parliaments. But most companies also have less conventional flavors. Blu offers Peach Schnapps, Java Jolt, Vivid Vanilla, Cherry Crush, and Piña Colada, presumably for people who don’t just like a drink with a cigarette, but in one.

February 5, 2014

The Internet and the defenestration of the gatekeepers

Filed under: Government, Liberty, Technology — Tags: , , , — Nicholas @ 08:51

In the latest Libertarian Enterprise, L. Neil Smith talks about the recent movie The Fifth Estate, prominent whistleblowers, and how the Internet upset so many top-down information models:

The top three “whistle-blowers”, of course, in no particular order, are Assange himself, Bradley/Chelsea Manning, and Edward Snowden. I’m interested in these individuals for a number of reasons, not the least of which, is that I wrote about them (actually, I anticipated them) long before most people in the world ever knew they existed.

Including me.

Eleven years ago, in a speech I delivered to the Libertarian Party of New Mexico entitled “Empire of Lies“, I asserted that every human being on Earth is swimming — drowning — in an ocean of lies, mostly told by governments of one variety or another. I pointed out that lies of that kind — for example, the Gulf of Tonkin “incident” that never happened, and yet cost the lives of 60,000 Americans and 2,000,000 Vietnamese — are deadly. I proposed, therefore, that any politician, bureaucrat, or policeman caught telling a lie to any member of the public for any reason — a well as any among their ilk keeping secrets — ought to be subject to capital punishment, preferably by public hanging.

On network television.

Some time later, I stumbled on what I think is the true historical significance of the Internet. For as long as human beings have been communicating with one another, except among family and friends (and even then, sometimes) communications have been vertical and one-way, from the top down. Just to take it back to the Middle Ages, you can’t talk back to, or argue with a church bell. You either do what you are trained to do when it rings — wake, pray, eat, go to bed — or you do not, and suffer whatever consequences society has arranged for you to suffer.

This sorry situation was not improved materially by later “great” inventions like the printing press, movies, radio, or television. Such innovations only made it easier and more convenient to issue orders. The elite laid down the law to the peons (that’s us) and there was no way of contradicting them. Letters to the Editor are limited to 400 words.

But the Internet, and all of the technical, political, and social phenomena associated with it, turned this communications hierarchy sideways. Almost overnight, it was now possible for anybody on the planet to talk to anybody else, and to speak privately with a single individual, or to millions, without obtaining anyone’s permission, judged not by their power or authority, but by the cogency of their arguments.

Atlas didn’t shrug, Authority wigged.

Traditional Big Media, newspaper, magazine, and book publishers, movie studios, radio and television network executives, held onto their monopoly gatekeeper position, inherited from a more primitive era, desperately and at any cost. Only they were fit to judge what word could be sent by mere individuals to the Great Unwashed (that’s us, again). What it cost them is their very existence. They were incapable of divining that the Age of Authority, including theirs, was over.

For governments all over the world, subsisting as they all do on lies, intimidation, and violence, it was a nightmare. They have tried to fight back, but they will lose. The tide of history is against them. The idea of “peer-to-peer” communication is out there, and — short of the mass slaughter some of them seem to be preparing against us: a measure of their utter despair — it can never be called back or contained.

February 3, 2014

New technology invades the vineyards – is it now the Côte-du-Drône?

Filed under: Europe, France, Technology, Wine — Tags: , — Nicholas @ 09:48

Jack Flanagan talks about the most recent technological intrusions into innovations being introduced into traditional European winemaking:

It is a new age in winemaking. The old days of doing everything by hand is ending. And while large-scale harvesters and flood-lights might not be news, the vintners of tomorrow have a few tricks up their sleeves.

[…]

And yet as advanced technology, the sort-of thing that requires a Masters of Science to understand, becomes available at lower prices (well, hovering among the thousands), vineyards in France and areas outside are adopting them.

Perhaps least surprising, if you’ve noticed a trend lately, is the addition of drones. Right now, they have a simple task: flying over vineyards, checking for damage or anything suspicious.

In the future, however, they may be required to do more labour-intensive tasks such as vine maintenance, e.g. pruning and checking how ripe the grapes are. This, specifically, is the task of a little droid resembling a rover: it skates along the vineyard floor, analysing and remembering the details of the vines. If they’re getting too long, the robot prunes them back.

January 31, 2014

(Micro-)Break it to make a material stronger

Filed under: Science, Technology — Tags: , , — Nicholas @ 14:18

Another example of how sometimes we can benefit by using biomimicry:

Engineers intrigued by the toughness of mollusc shells, which are composed of brittle minerals, have found inspiration in their structure to make glass 200 times stronger than a standard pane.

Counter-intuitively, the glass is strengthened by introducing a network of microscopic cracks, according to a study published in the journal Nature Communications on Tuesday.

A team at McGill University in Montreal began their research with a close-up study of natural materials like mollusc shells, bone and nails which are astonishingly resilient despite being made of brittle minerals.

The secret lies in the fact that the minerals are bound together into a larger, tougher unit.

The binding means the shell contains abundant tiny fault lines called interfaces. Outwardly, this might seem a weakness, but in practice it is a masterful deflector of external pressure.

To take one example, the shiny, inner shell layer of some molluscs, known as nacre or mother of pearl, is some 3,000 times tougher than the minerals it is made of.

The maple-flavoured NSA used airport Wi-Fi to track travellers

Filed under: Cancon, Government, Technology — Tags: , , , — Nicholas @ 09:17

With so much talk about the NSA and GCHQ using every electronic means at their disposal, it was inevitable that some of the documents being released by Edward Snowden would implicate Canadian intelligence in similar activities:

A top secret document retrieved by U.S. whistleblower Edward Snowden and obtained by CBC News shows that Canada’s electronic spy agency used information from the free internet service at a major Canadian airport to track the wireless devices of thousands of ordinary airline passengers for days after they left the terminal.

After reviewing the document, one of Canada’s foremost authorities on cyber-security says the clandestine operation by the Communications Security Establishment Canada (CSEC) was almost certainly illegal.

Ronald Deibert told CBC News: “I can’t see any circumstance in which this would not be unlawful, under current Canadian law, under our Charter, under CSEC’s mandates.”

The spy agency is supposed to be collecting primarily foreign intelligence by intercepting overseas phone and internet traffic, and is prohibited by law from targeting Canadians or anyone in Canada without a judicial warrant.

As CSEC chief John Forster recently stated: “I can tell you that we do not target Canadians at home or abroad in our foreign intelligence activities, nor do we target anyone in Canada.

“In fact, it’s prohibited by law. Protecting the privacy of Canadians is our most important principle.”

But security experts who have been apprised of the document point out the airline passengers in a Canadian airport were clearly in Canada.

CSEC said in a written statement to CBC News that it is “mandated to collect foreign signals intelligence to protect Canada and Canadians. And in order to fulfill that key foreign intelligence role for the country, CSEC is legally authorized to collect and analyze metadata.”

Metadata reveals a trove of information including, for example, the location and telephone numbers of all calls a person makes and receives — but not the content of the call, which would legally be considered a private communication and cannot be intercepted without a warrant.

“No Canadian communications were (or are) targeted, collected or used,” the agency says.

In the case of the airport tracking operation, the metadata apparently identified travelers’ wireless devices, but not the content of calls made or emails sent from them.

January 28, 2014

3D printing about to get more colourful

Filed under: Technology — Tags: — Nicholas @ 09:49

In The Register, Lester Haines looks at a new 3D printer that promises a lot more colour:

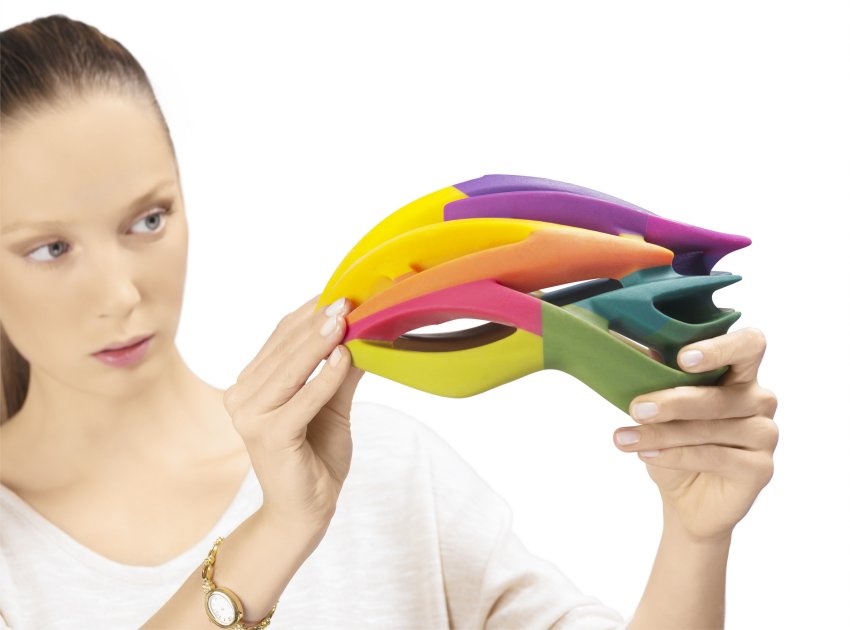
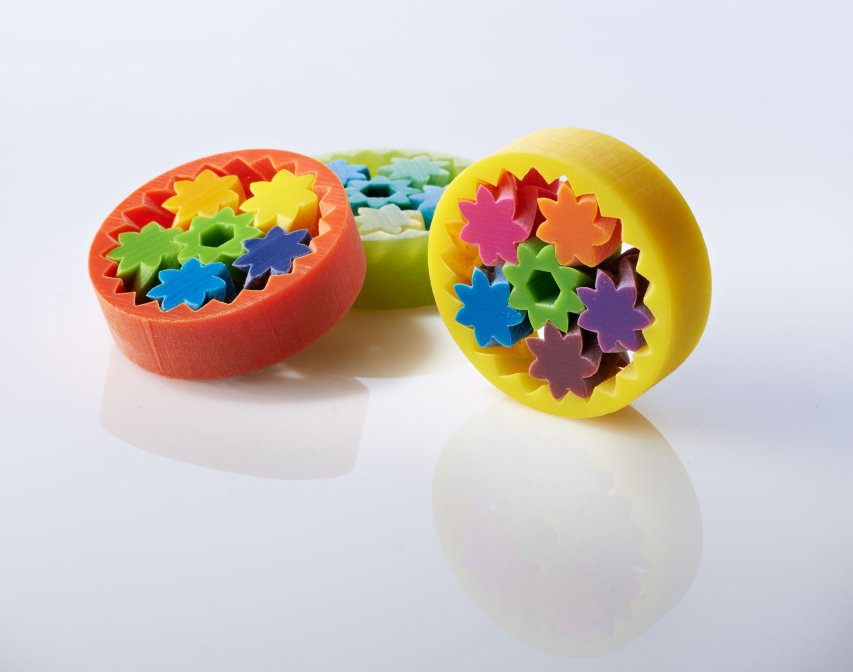
Those of you frustrated by the monochrome, single material output of 3D printers, and who happen to have very deep pockets, are directed to the Stratasys Objet500 Connex3, hailed as the world’s first full-colour machine.

Stratasys colour 3D printed helmet

The tech behind these impressive capabilities is Stratysys’s proprietary “PolyJet 3D“. The company explains this is “similar to inkjet document printing, but instead of jetting drops of ink onto paper, PolyJet 3D Printers jet layers of liquid photopolymer onto a build tray and instantly cure them with UV light”.

It continues: “The most advanced PolyJet systems combine diverse 3D printing materials in one model by jetting multiple materials simultaneously. This means you can selectively position multiple materials in one printed prototype and even combine two or three materials to create composite digital materials with distinct, predictable properties.”

Stratasys colour 3D printed gears

However, as you might expect, the new printer isn’t cheap — £200,000 ($330,000) is the quoted starting price.

« Newer PostsOlder Posts »

Powered by WordPress