Published on 30 Dec 2013
A web app that works out how many seconds ago something happened. How hard can coding that be? Tom Scott explains how time twists and turns like a twisty-turny thing. It’s not to be trifled with!
H/T to Jeremy for the link.
Published on 30 Dec 2013
A web app that works out how many seconds ago something happened. How hard can coding that be? Tom Scott explains how time twists and turns like a twisty-turny thing. It’s not to be trifled with!
H/T to Jeremy for the link.
In The Atlantic, Ingrid Burrington tries to persuade her editor that the submarine cable network is still of critical importance to understanding the cloud:
“So Ingrid,” Sam asked, “how exactly will you convince your editor that submarine cables are relevant to The Cloud?”
We were maybe still in New Mexico or somewhere in Kansas. It was a night drive. Time moves weirdly during night drives. All roads basically become the closing moments of Terminator 2. Whenever it was and wherever it was, it was apparently a good time for my driving partner to pose questions about some of the stories I had lined up for this series, including one exceptionally long piece about a submarine cable (which, dear reader, will run later this week).
“Well,” I replied, “clouds are just evaporated molecules of water that emerge from larger bodies of water. Oceans are bodies of water. It’s … it’s relevant.”
Look, I was pretty tired. But if there is a case to be made for placing submarine cables within the landscape of The Cloud, it’s more a case for historical continuity and resonance. Cloud infrastructure is a landscape of interdependent systems, submarine cables among them.
Submarine cables don’t come up in the news that often, but if they do it seems to be in two forms: short articles reminding everyone that the Telegeography Submarine Cable Map exists, and short articles of hand-wavey reminders that submarine cables are vulnerable to harm (from tectonic plates, ship anchors, sharks, and terrorists, among others).
While these are totally valid topics to explore, I often find these stories lacking in context about the various systems, geographies, and politics that shape submarine networks. While there are lots of other super compelling aspects of submarine-cable law and policy (says the person who owns a copy of Submarine Cables: The Handbook of Law and Policy), here are two questions that might help readers take in Telegeography takes with a little less gee-whiz and a little more clarity.
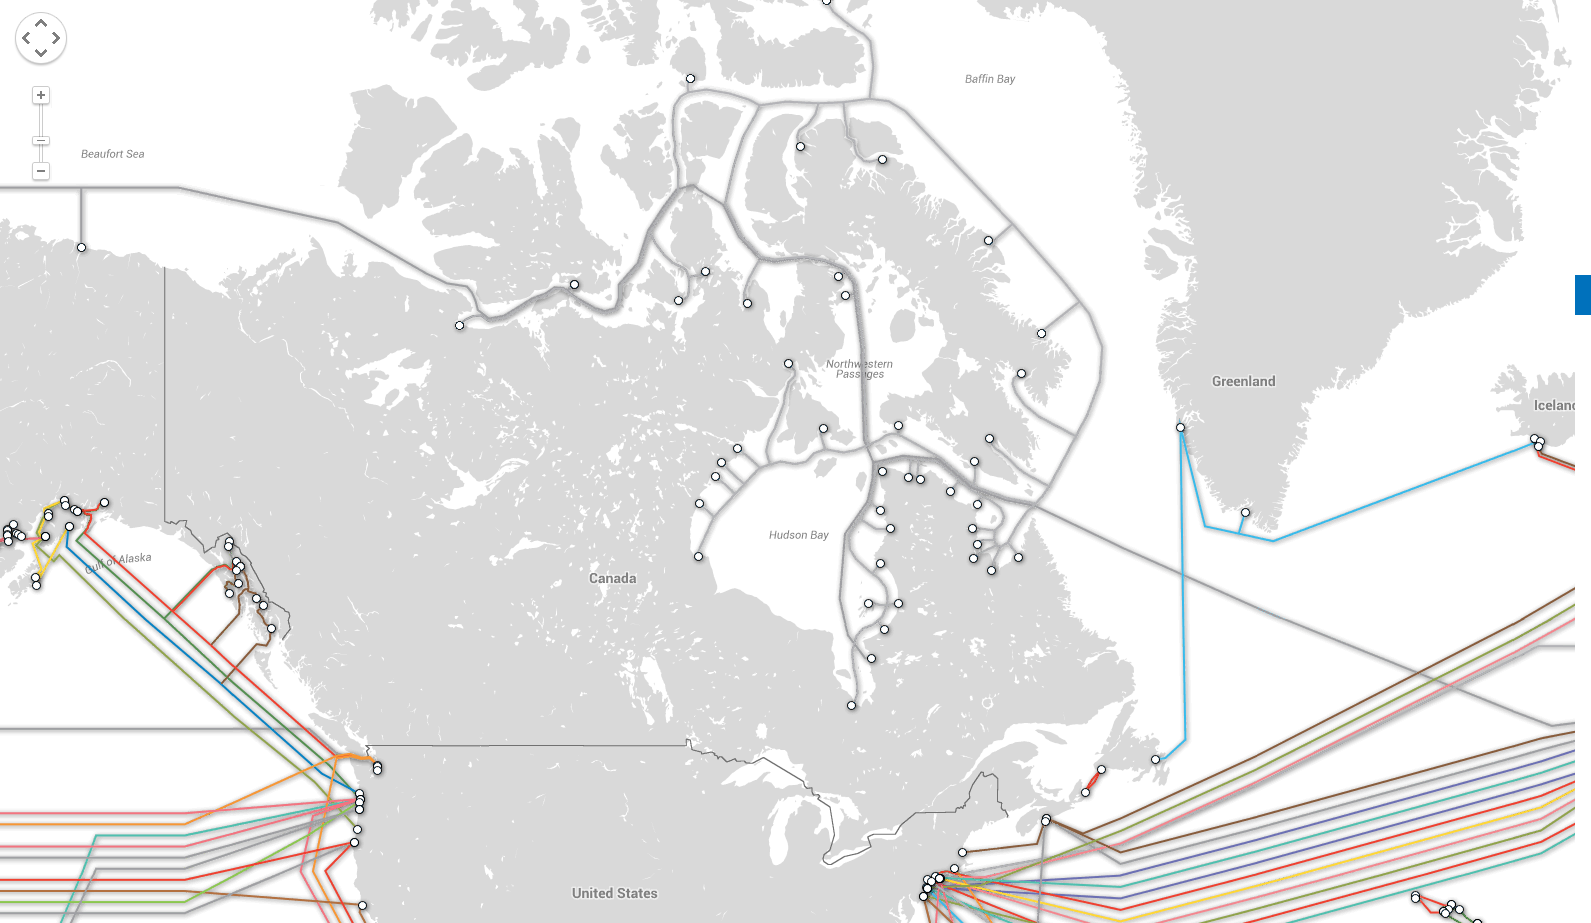
Speaking of submarine cables, I was unaware of how many northern Canadian communities are connected via that method:
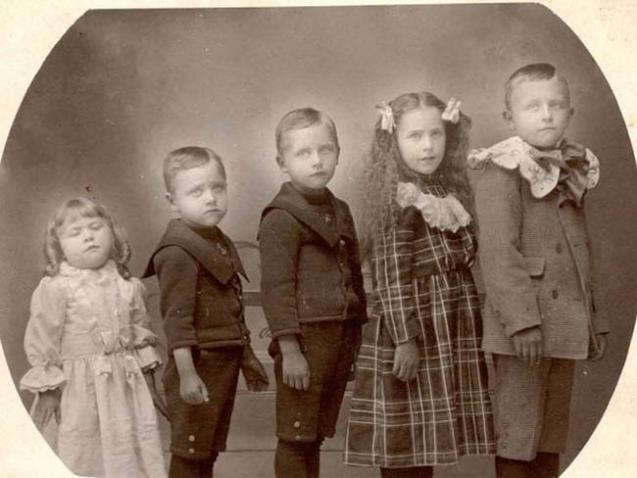
Open Culture on the thankfully brief popularity of post-mortem photography (photos of the recently deceased as if they were merely sleeping):
The 19th century witnessed the birth of photography. And, before too long, Victorian society found important applications for the new medium — like memorializing the dead. A recent post on a Dutch version of National Geographic notes that “Photographing deceased family members just before their burial was enormously popular in certain Victorian circles in Europe and the United States. Although adults were also photographed, it was mainly children who were commemorated in this way. In a period plagued by unprecedented levels of infant mortality, post-mortem pictures often provided the only tangible memory of the deceased child.”
Eric S. Raymond explains how technical documentation can manage the difficult task of being both demonstrably complete and technically correct and yet totally fail to meet the needs of the real audience:
I was using “hieratic” in a sense like this:
hieratic, adj. Of computer documentation, impenetrable because the author never sees outside his own intimate knowledge of the subject and is therefore unable to identify or meet the expository needs of newcomers. It might as well be written in hieroglyphics.
Hieratic documentation can be all of complete, correct, and nearly useless at the same time. I think we need this word to distinguish subtle disasters like the waf book – or most of the NTP documentation before I got at it – from the more obvious disasters of documentation that is incorrect, incomplete, or poorly written simply considered as expository prose.
Published on 16 Nov 2015
If one thing was vital to the the new kind of modern warfare in the First World War, it was communications. The Industrial Revolution had brought wireless transmission of signals with it and the huge armies of World War 1 needed to be in contact constantly to be successful in the field. In this special episode we introduce you to the birth hour of modern military communication and signals.
Tyler Rogoway recounts the set of formal and informal rules Kelly Johnson used while running the famous “Skunk Works”:
Clarence “Kelly” Johnson is the Babe Ruth of aerospace design. Aircraft programs under Johnson were so cutting edge and historically influential, and his cult of personality and management strategy so effective, that he and Lockheed’s Skunk Works (which he also founded) are forever enshrined in mankind’s technological hall of fame.
[…]
Kelly’s Rules
1. The Skunk Works manager must be delegated near complete control of his program in all aspects. He should report to a division president or higher.
2. Strong but small project offices must be provided both by the military and industry.
3. The number of people having any connection with the project must be restricted in an almost vicious manner. Use a small number of good people (10% to 25% compared to the so-called normal systems).
4. A very simple drawing and drawing release system with great flexibility for making changes must be provided.
5. There must be a minimum number of reports required, but important work must be recorded thoroughly.
6. There must be a monthly cost review covering not only what has been spent and committed but also projected costs to the conclusion of the program.
7. The contractor must be delegated and must assume more than normal responsibility to get good vendor bids for subcontract on the project. Commercial bid procedures are often better than military ones.
8. The inspection system as currently used by the Skunk Works, which has been approved by both the Air Force and Navy, meets the intent of existing military requirements and should be used on new projects. Push more basic inspection responsibility back to subcontractors and vendors. Don’t duplicate so much inspection.
9. The contractor must be delegated the authority to test his final product in flight. He can and must test it in the initial stages. If he doesn’t, he rapidly loses his competency to design other vehicles.
10. The specifications applying to the hardware, including rationale for each point, must be agreed upon well in advance of contracting.
11. Funding a program must be timely so that the contractor doesn’t have to keep running to the bank to support government projects.
12. There must be mutual trust between the military project organization and the contractor, and there must be very close cooperation and liaison on a day-to-day basis. This cuts down misunderstanding and correspondence to an absolute minimum.
13. Access by outsiders to the project and its personnel must be strictly controlled by appropriate security measures.
14. Because only a few people will be used in engineering and most other areas, ways must be provided to reward good performance by pay not based on the number of personnel supervised.
Kelly also had a unofficial 15th, 16th, and 17th rules, which he is known to have stated repeatedly to his subordinates:
15. Never do business with the Navy!
16. No reports longer than 20 pages or meetings with more than 15 people.
17. If it looks ugly, it will fly the same.
It is amazing to think that one man did so much to advance mankind’s aerospace capability. Even his few dead-ends and failures had key technologies that would lead to wins or lessons learned down the road.
H/T to @NavyLookout for the link.
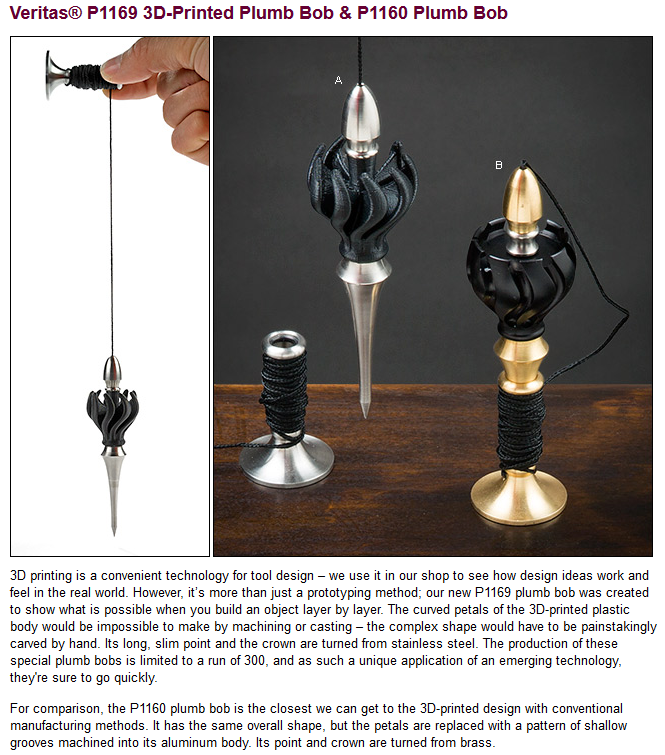
Lee Valley now offers a 3D-printed plumb bob and shows the advantages of using 3D print capabilities:
Five years back, there were interesting reports about a prototype weapon that seemed to have an inside edge for getting into the hands of front-line troops in Afghanistan for specific bunker-busting and similar missions. Then it went silent. Recently, Strategy Page says it may be back in the running:
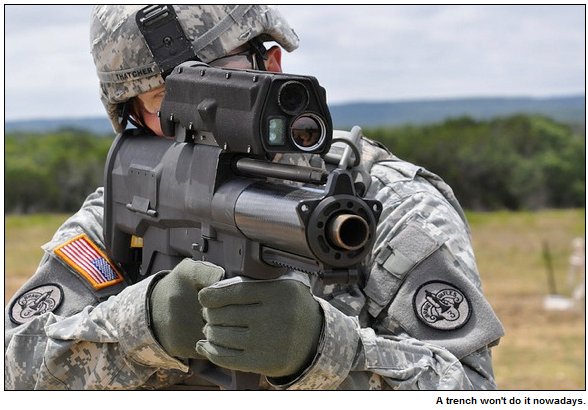
Two years after having its budget sharply cut in 2013 the U.S. Army XM25 grenade launcher is back on track and is now expected to enter service by 2017. It’s been a long road from concept to acceptance and mass production. The army began working on this type of weapon back in the 1990s as the OICW (Objective Individual Combat Weapon) and that mutated into the XM25 (the “X” in XM25 designates a system that is still in development). Since then the similar South Korean K11 and Chinese ZH05 have appeared. The XM25 is the only one of three to have been tested extensively in combat but because of a misfire during a demonstration, budget cuts and some troops finding there were not really that many situations calling for the XM25, the system was thought to be cancelled (development funding was eliminated) in 2013. But the army managed to keep the project on life support. That was mainly because a lot of troops who got to use it in combat liked it a lot and even gave it a nickname; “punisher.”
The initial spectacular success and popularity of the XM25 grenade launchers in Afghanistan led the army to request that the weapon enter regular service as the M25 in 2014. But Congress, looking for ways to reduce military spending in 2013 cut all money for the M25. The army never gave up and managed to scrounge enough cash to build 1,100 of them. Currently the XM25 cost $35,000 each with the 25mm ammo going for $55 per round. Initially SOCOM (Special Operations Command) had some XM25s and some enthusiastic users but in 2013, with few American troops in combat there is not a lot of demand for a weapon like this. The resumption of counter-terrorism efforts in the Middle East and Afghanistan changed that led to more support for reviving the project.
When the first evaluation models of the XM25 arrived in Afghanistan in 2011 the weapon soon became much sought after by infantry troops. There were never more than a few dozen XM25s in Afghanistan and limited supplies of ammunition. Despite that the weapon quickly developed a formidable reputation. The Special Forces had priority on the weapon because it is very useful for special operations missions. The army planned to buy enough so that they could issue one per infantry squad. There are 27 squads in an infantry battalion.
Elizabeth and I spent the weekend in the Bay of Quinte area, visiting Prince Edward County, Belleville, and Trenton. While we were in Trenton, we stopped in at the National Air Force Museum of Canada. While the Sea King may not be in the collection yet (at least, not in the collection visible to the public), many other Canadian Armed Forces aircraft are, including the prize of the museum, the Handley Page Halifax heavy bomber:
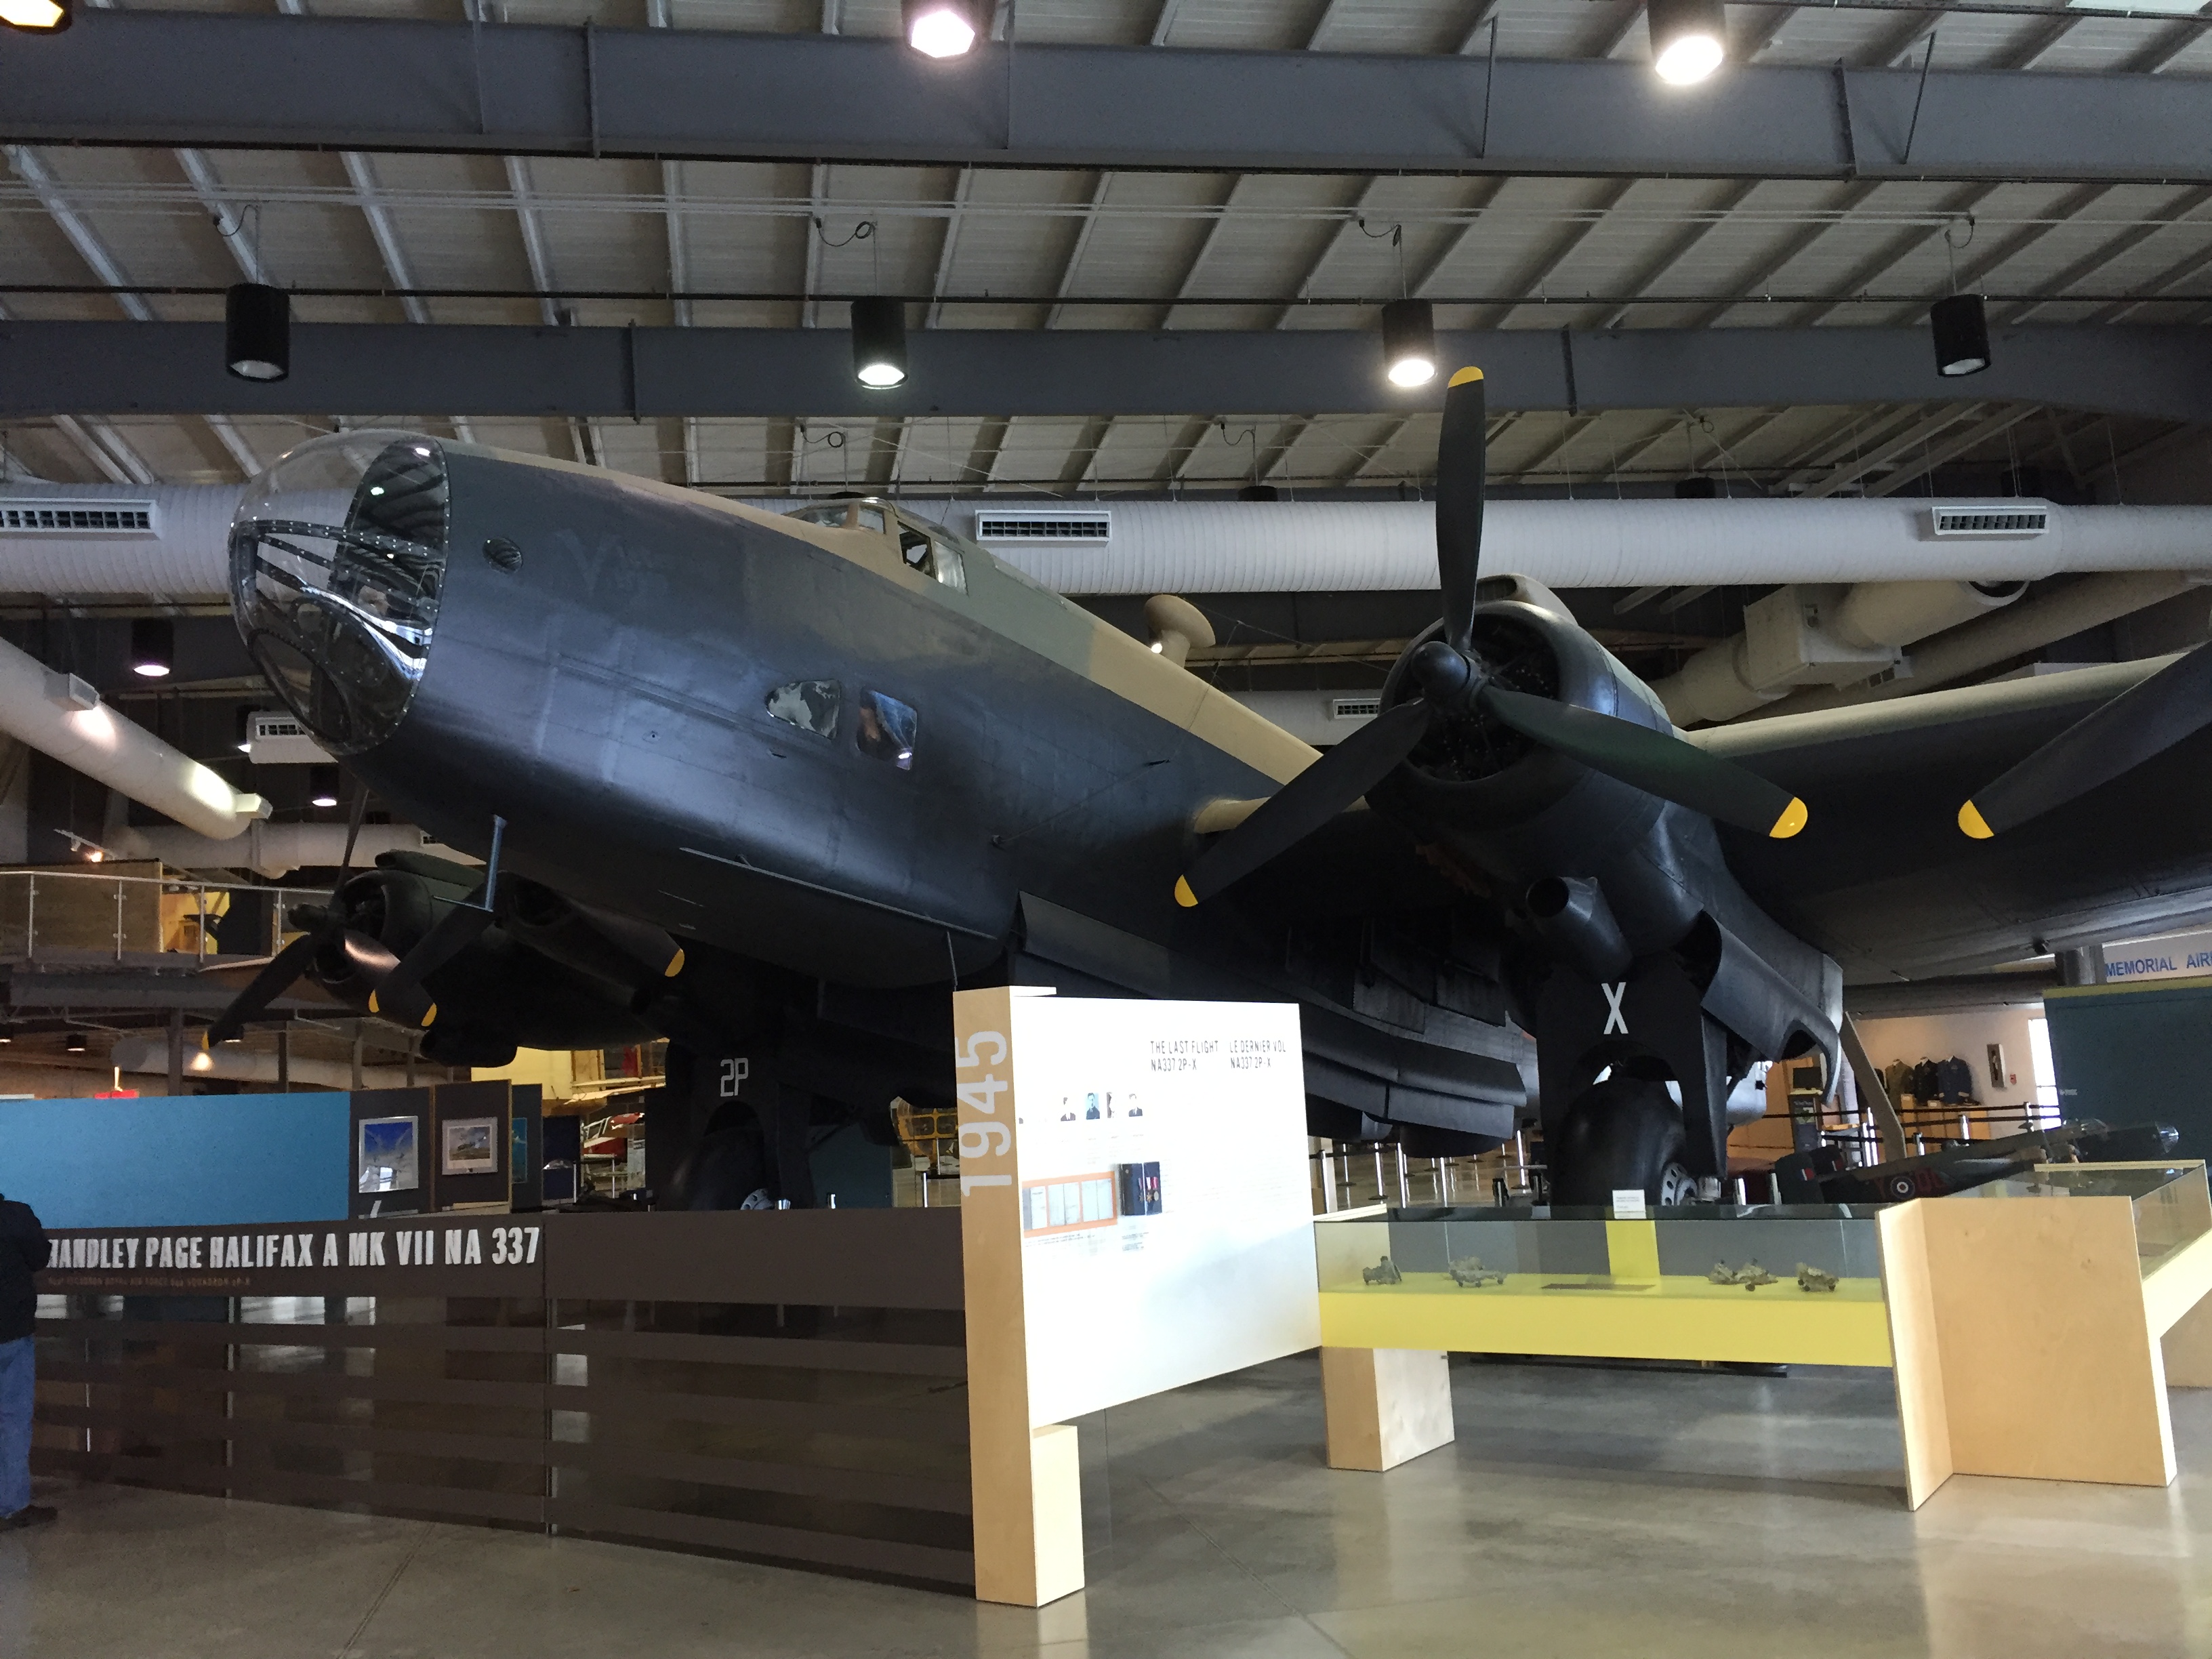
It’s a big enough aircraft that it’s hard to do it justice in a photograph.
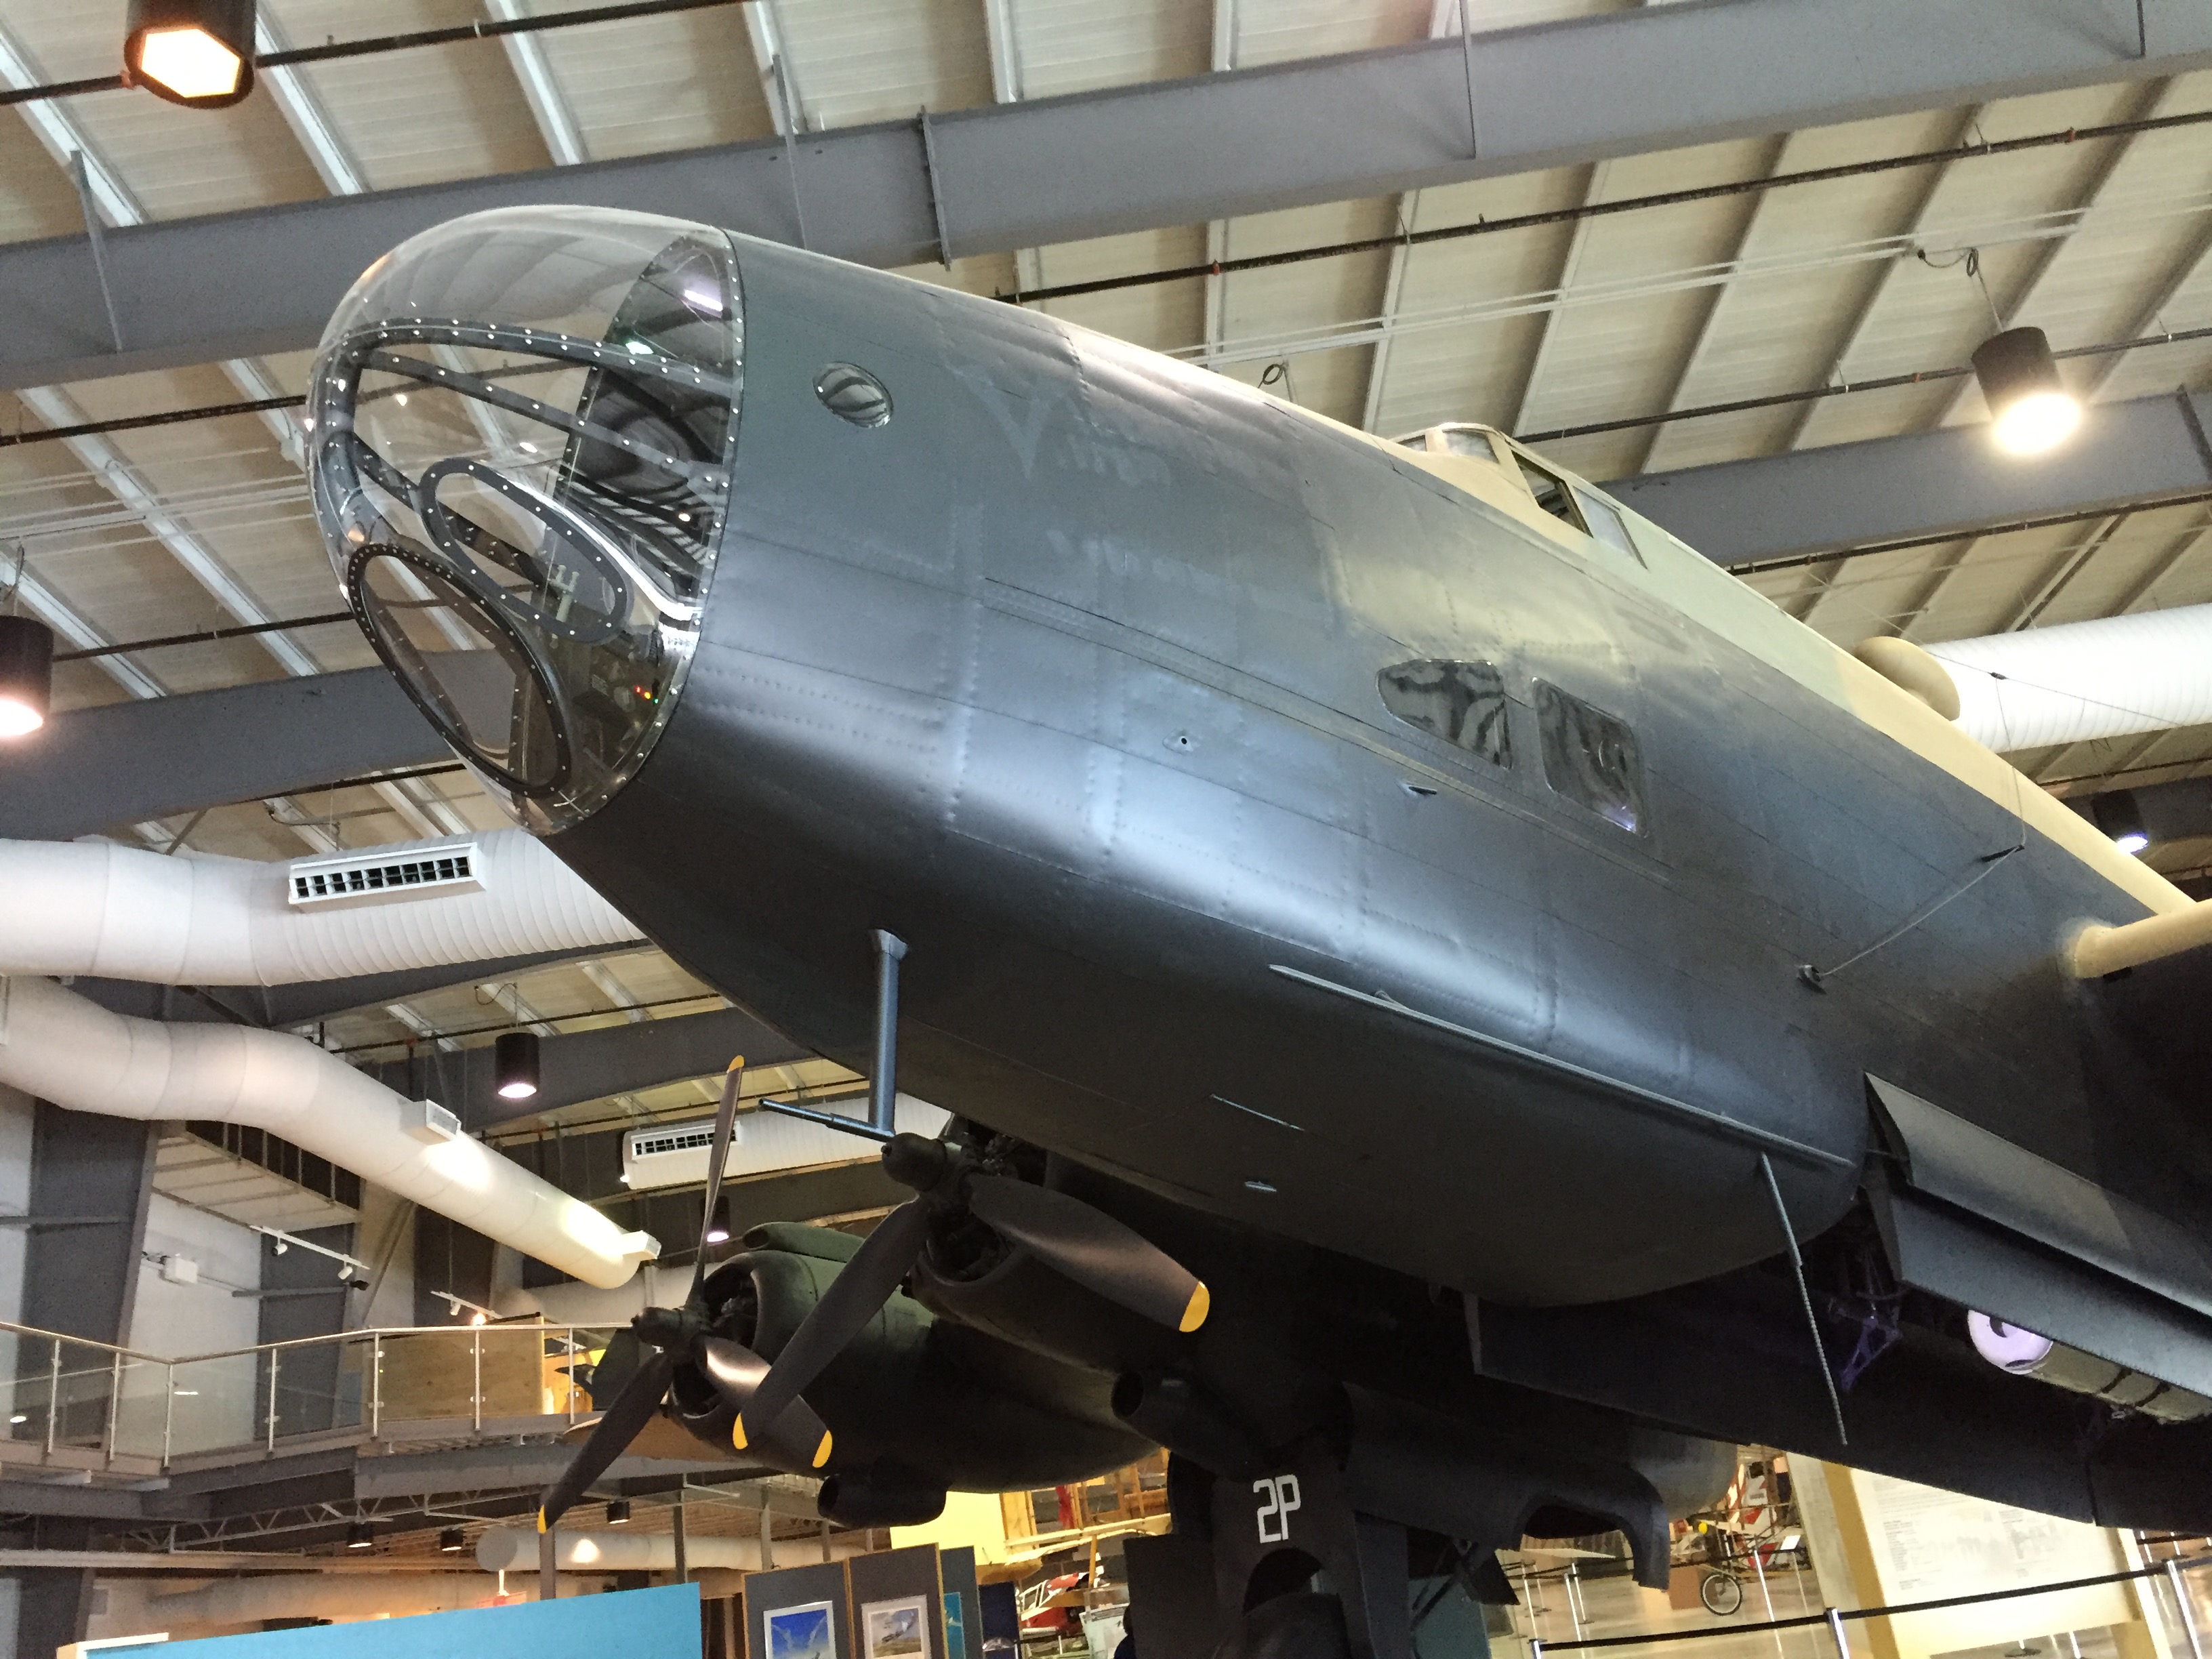
This particular restored aircraft was shot down late in the war on a mission to deliver supplies to Norwegian resistance fighters and later recovered from a Norwegian lake.
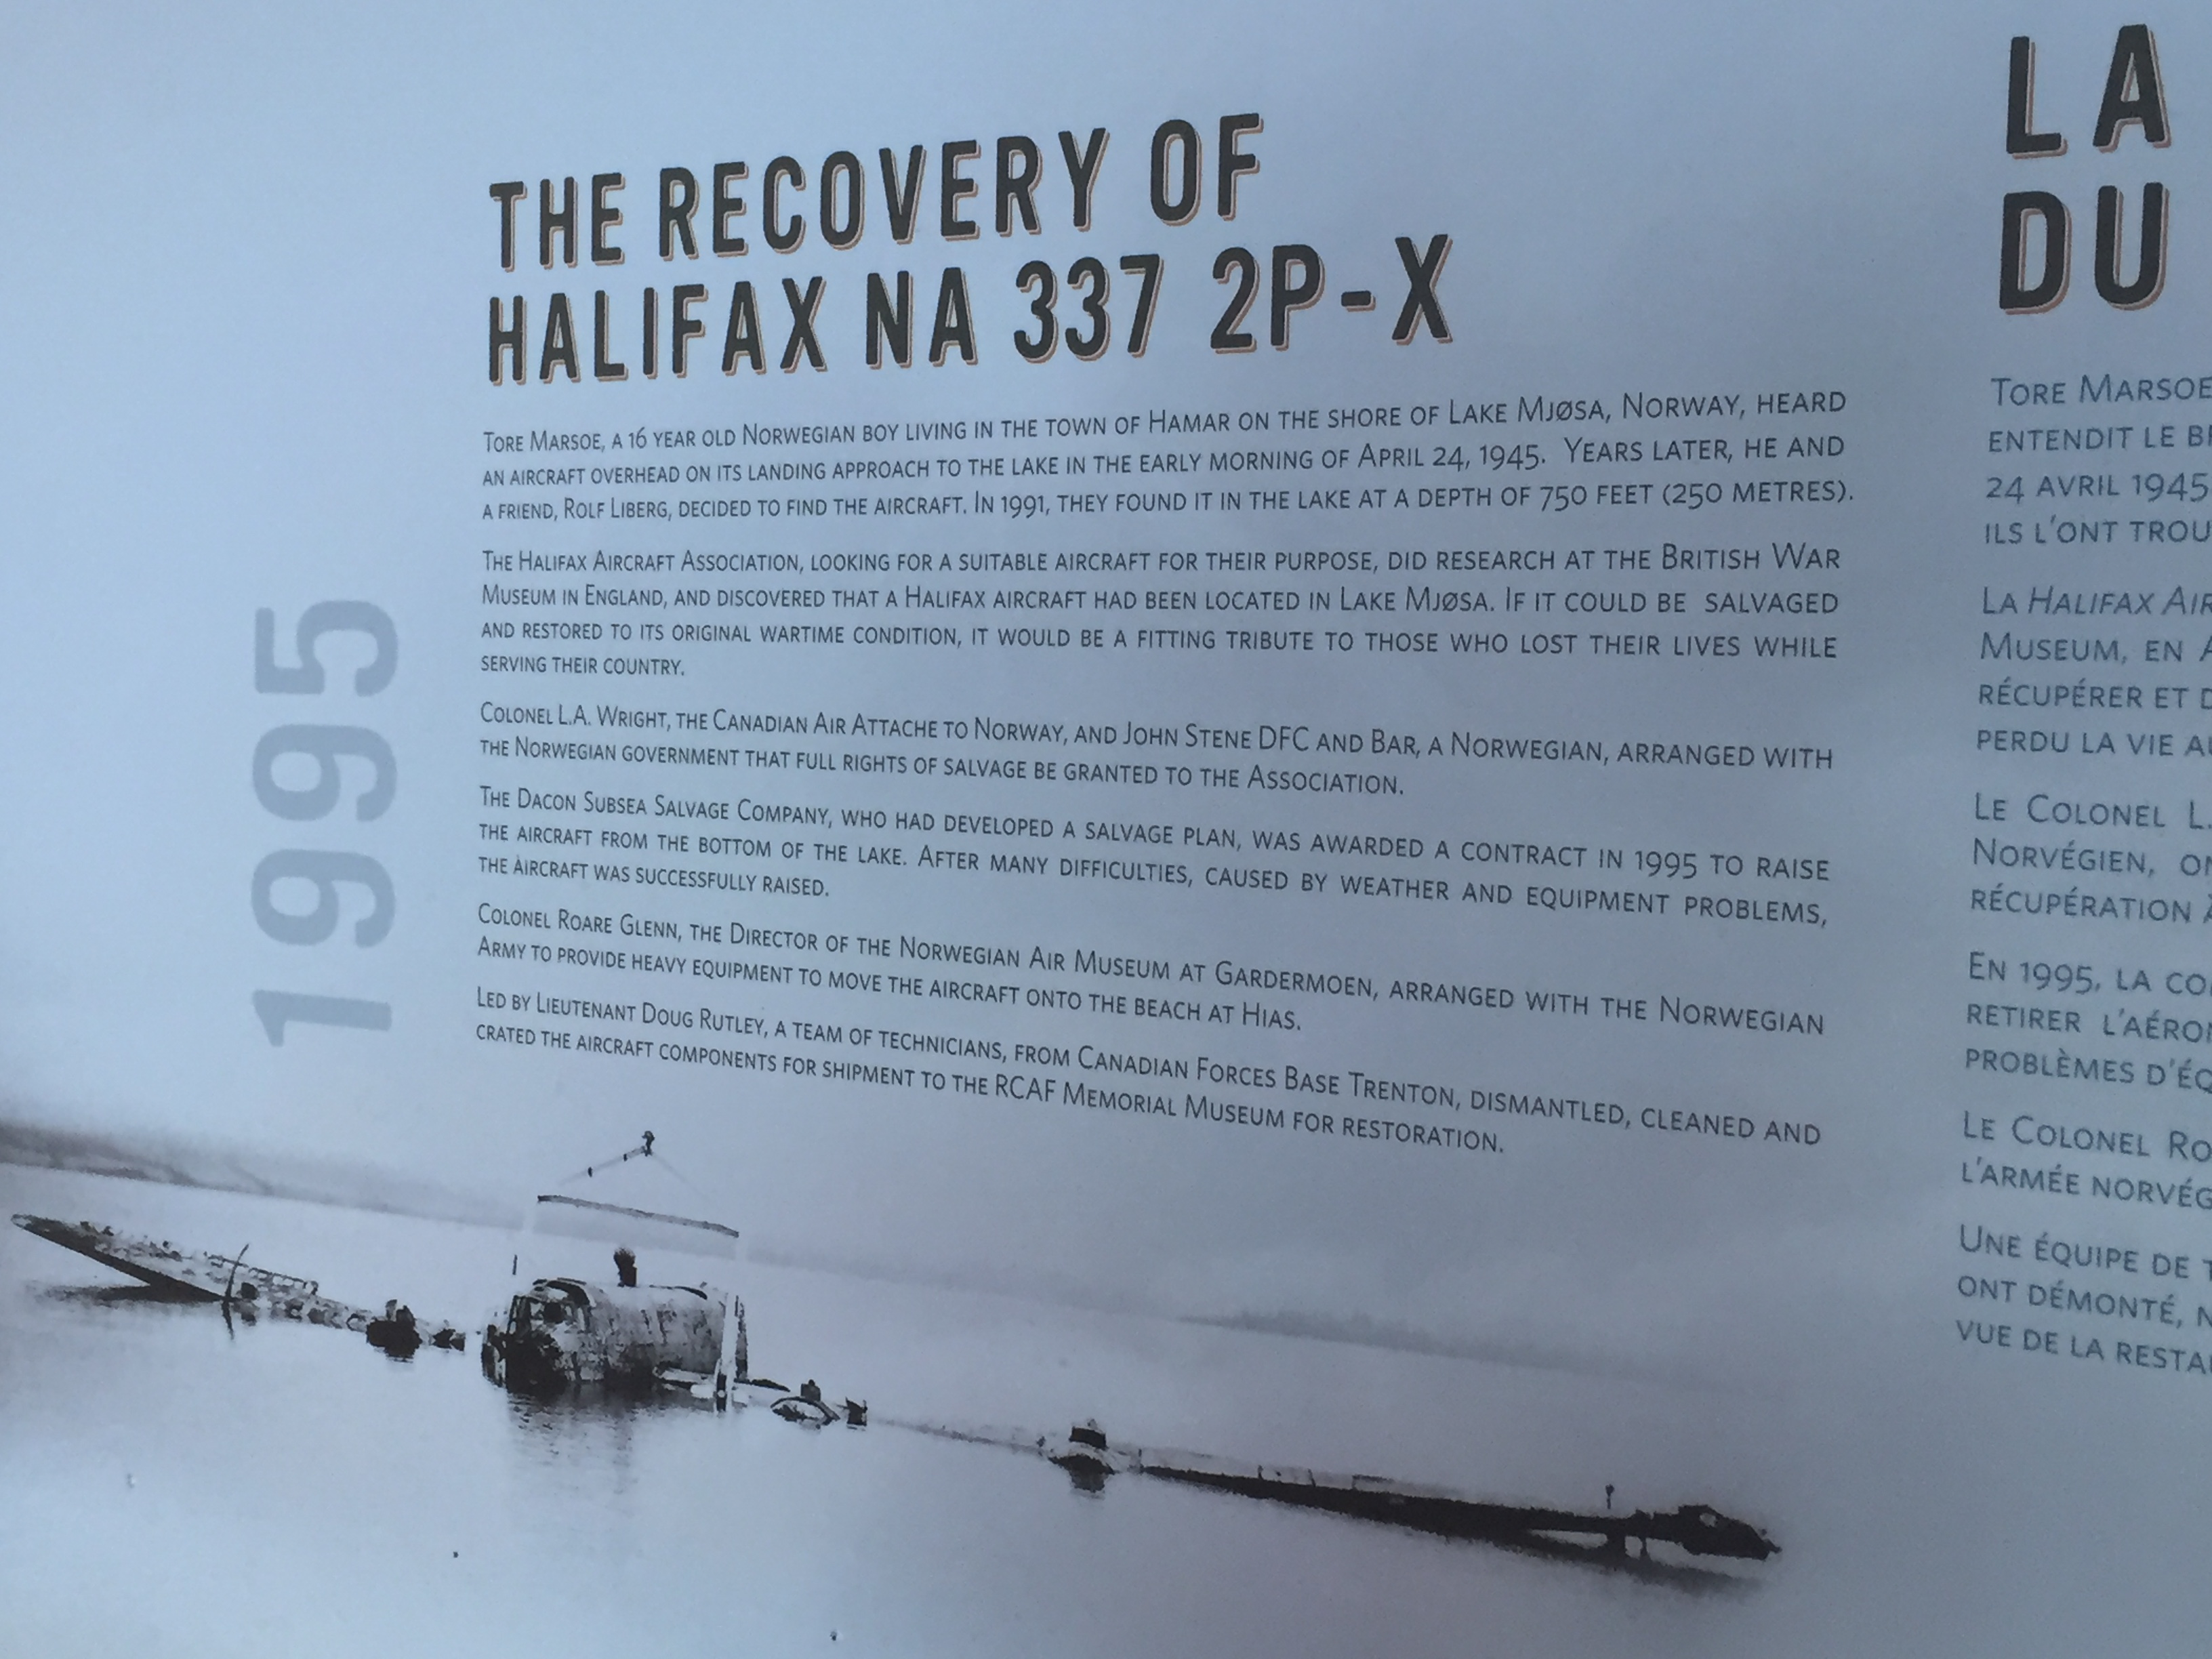
Other aircraft in the collection include a replica of the Silver Dart, the first powered aircraft to fly in Canada (February 23, 1909), a replica of the Burgess-Dunne floatplane, the first aircraft purchased for the Canadian military (September, 1914), a CF-86 Sabre, a CF-100 Canuck, a CF-5 Freedom Fighter, a CF-104 Starfighter, a CF-101 Voodoo, a CF-18 Hornet, a CP-107 Argus, a CC-130 Hercules, and a CP-102 Tracker among other aircraft.
At Ars Technica, Dan Goodin discussed the imminent availability of free HTTPS certificates to all registered domain owners:
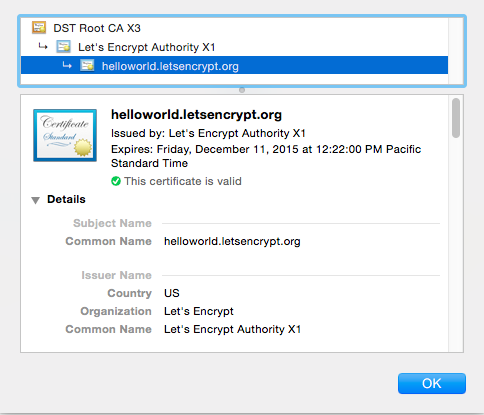
A nonprofit effort aimed at encrypting the entire Web has reached an important milestone: its HTTPS certificates are now trusted by all major browsers.
The service, which is backed by the Electronic Frontier Foundation, Mozilla, Cisco Systems, and Akamai, is known as Let’s Encrypt. As Ars reported last year, the group will offer free HTTPS certificates to anyone who owns a domain name. Let’s Encrypt promises to provide open source tools that automate processes for both applying for and receiving the credential and configuring a website to use it securely.
HTTPS uses the transport layer security or secure sockets layer protocols to secure websites in two important ways. First, it encrypts communications passing between visitors and the Web server so they can’t be read or modified by anyone who may be monitoring the connection. Second, in the case of bare bones certificates, it cryptographically proves that a server belongs to the same organization or person with control over the domain, rather than an imposter posing as that organization. (Extended validation certificates go a step beyond by authenticating the identity of the organization or individual.)
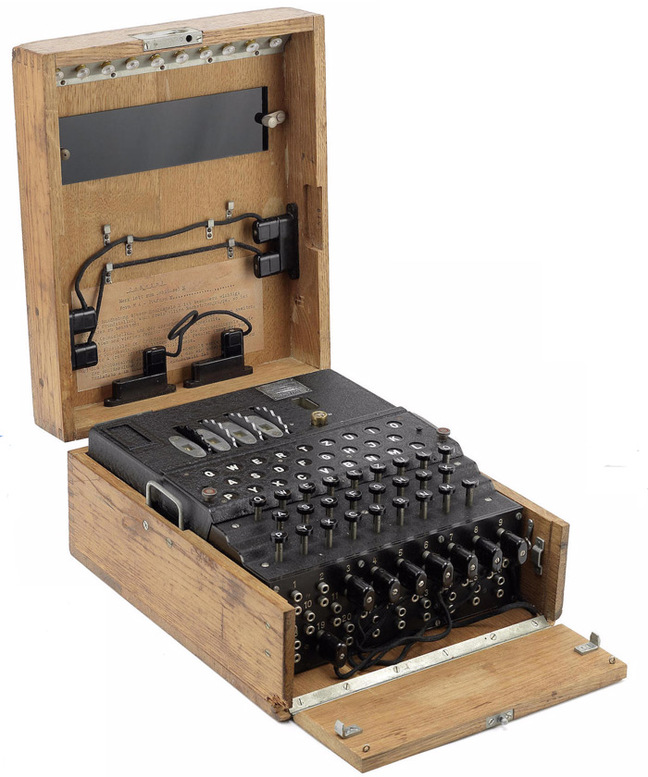
Lester Haines reports on a recent record auction price for an Enigma machine:
A fully-functioning four-rotor M4 Enigma WW2 cipher machine has sold at auction for $365,000.
The German encryption device, as used by the U-Boat fleet and described as “one of the rarest of all the Enigma machines”, went under the hammer at Bonham’s in New York last night as part of the “Conflicts of the 20th Century” sale.
The M4 was adopted by the German Navy, the Kriegsmarine, in early 1942 following the capture of U-570 in August 1941*. Although the crew of U-570 had destroyed their three-rotor Enigma, the British found aboard written material which compromised the security of the machine.
The traffic to and from the replacement machines was dubbed “Shark” by codebreakers at Bletchley Park. Decryption proved troublesome, due in part to an initial lack of “cribs” (identified or suspected plaintext in an encrypted message) for the new device, but by December 1942, the British were regularly cracking M4 messages.
I recently read David O’Keefe’s One Day in August, which seems to explain the otherwise inexplicable launch of “Operation Jubilee”, the Dieppe raid … in his reading, the raid was actually a cover-up operation while British intelligence operatives tried to snatch one or more of the new Enigma machines (like the one shown above) without tipping off the Germans that that was the actual goal. Joel Ralph reviewed the book when it was released:
One Day in August, by David O’Keefe, takes a completely different approach to the Dieppe landing. With significant new evidence in hand, O’Keefe seeks to reframe the entire raid within the context of the secret naval intelligence war being fought against Nazi Germany.
On February 1, 1942, German U-boats operating in the Atlantic Ocean switched from using a three-rotor Enigma code machine to a new four-rotor machine. Britain’s Naval Intelligence Division, which had broken the three-rotor code and was regularly reading German coded messages, was suddenly left entirely in the dark as to the positions and intentions of enemy submarines. By the summer of 1942, the Battle of the Atlantic had reached a state of crisis and was threatening to cut off Britain from the resources needed to carry on with the war.
O’Keefe spends nearly two hundred pages documenting the secret war against Germany and the growth of the Naval Intelligence Division. What ties this to Dieppe and sparked O’Keefe’s research was the development of a unique naval intelligence commando unit tasked with retrieving vital code-breaking material. As O’Keefe’s research reveals, the origins of this unit were at Dieppe, on an almost suicidal mission to gather intelligence they hoped would crack the four-rotor Enigma machine.
O’Keefe has uncovered new documents and first-hand accounts that provide evidence for the existence of such a mission. But he takes it one step further and argues that these secret commandos were not simply along for the ride at Dieppe. Instead, he claims, the entire Dieppe raid was cover for their important task.
It’s easy to dismiss O’Keefe’s argument as too incredible (Zuehlke does so quickly in his brief conclusion [in his book Operation Jubilee, August 19, 1942]). But O’Keefe would argue that just about everything associated with combined operations defied conventional military logic, from Operation Ruthless, a planned but never executed James Bond-style mission, to the successful raid on the French port of St. Nazaire only months before Dieppe.
Clearly this commando operation was an important part of the Dieppe raid. But, while the circumstantial evidence is robust, there is no single clear document that directly lays out the Dieppe raid as cover for a secret “pinch by design” operation to steal German code books and Enigma material.
John Turner sent me this link on a remarkably adept (and technologically sophisticated) hack the Soviets slipped over the US government at their Moscow embassy:
A National Security Agency memo that recently resurfaced a few years after it was first published contains a detailed analysis of what very possibly was the world’s first keylogger — a 1970s bug that Soviet spies implanted in US diplomats’ IBM Selectric typewriters to monitor classified letters and memos.
The electromechanical implants were nothing short of an engineering marvel. The highly miniaturized series of circuits were stuffed into a metal bar that ran the length of the typewriter, making them invisible to the naked eye. The implant, which could only be seen using X-ray equipment, recorded the precise location of the little ball Selectric typewriters used to imprint a character on paper. With the exception of spaces, tabs, hyphens, and backspaces, the tiny devices had the ability to record every key press and transmit it back to Soviet spies in real time.
The Soviet implants were discovered through the painstaking analysis of more than 10 tons’ worth of equipment seized from US embassies and consulates and shipped back to the US. The implants were ultimately found inside 16 typewriters used from 1976 to 1984 at the US embassy in Moscow and the US consulate in Leningrad. The bugs went undetected for the entire eight-year span and only came to light following a tip from a US ally whose own embassy was the target of a similar eavesdropping operation.
“Despite the ambiguities in knowing what characters were typed, the typewriter attack against the US was a lucrative source of information for the Soviets,” an NSA document, which was declassified several years ago, concluded. “It was difficult to quantify the damage to the US from this exploitation because it went on for such a long time.” The NSA document was published here in 2012. Ars is reporting the document because it doesn’t appear to have been widely covered before and generated a lively conversation Monday on the blog of encryption and security expert Bruce Schneier.
The question, raised by Robert Farley at The National Interest is “Is it time to bring back the Battleships?”
Is it time to bring back the battleship?
For decades, naval architects have concentrated on building ships that, by the standards of the World Wars, are remarkably brittle. These ships can deal punishment at much greater ranges than their early 20th century counterparts, but they can’t take a hit. Is it time to reconsider this strategy, and once again build protected ships? This article examines how these trends came about, and what might change in the future.
The label “battleship” emerges from the older “ship of the line” formulation, in the sense that a navy’s largest ships participated in the “line of battle” formation that allowed them to bring their broadsides to bear on an opposing line. After the development of ironclad warships, the “battle ship” diverged from the armored cruiser based on expectations of usage; “battleships” were expected to fight enemy “battleships.” The modern battleship form settled around 1890, with the British Royal Sovereign class. These ships displaced about 15,000 tons, with two heavy guns each in turrets fore and aft, and steel armor. The rest of the navies of the world adopted these basic design parameters, which provided a ship that could both deal out and absorb punishment. The process of ensuring survivability was simplified, in these early battleships, by the predictability of the threat. The most likely vector of attack in the late 1890s came from large naval artillery carried by other ships, and consequently protective schemes could concentrate on that threat.
From the American perspective, even if through some collective congressional brain-fart the US Navy was compelled to build and deploy modern analogues to the classic battleship, what the hell would they be used for? China and Russia are not going to build opposing battleships, and it’s difficult to imagine anyone else on the planet who would have both the economic resources and the strategic desire to go toe-to-toe in Jutland fashion against the USN.
Tesla does over-the-air updates for their electric cars (which is kinda neat). The latest update includes an almost-but-not-quite self-driving feature:
Tonight, Tesla makes its cars autonomous. Well, semi-autonomous. And it did it with an over-the-air update, effectively making tens of thousands of cars already sold to customers way better.
There are two things to talk about here. There’s the small story about the features and what the upgrade actually looks like and how it works. That’s a good place to start: This is the biggest change to the visual display of the Model S and X ever. There are new instrument panels, app windows are larger and take up more of the 17-inch touchscreen. Drivers will now get more information about what their cars are doing when in Autopilot, they can lock and unlock their car from the status bar. There’s a new clock!
These are simple cosmetic changes. The Big Story is that all of this—and really, who cares about anything beyond autopilot mode?—is being pushed through to customers’ Teslas overnight. The update will begin being pushed out tonight, and will hit every Tesla made and sold in the US in the past year over the course of this week.
Before you get too excited about an autonomous, hands-free present, you need to know that you can’t nap in the back, chauffeured around in beautiful, electric silence.
Even in Autopilot, you keep your hands on the steering wheel. Well… you don’t have to keep your hands on the steering wheel. You can rest them on your knees (resting on knees, palms up, fingertips touching the wheel is advised), or keep one pinky on the wheel. And okay, you can take your hands off altogether for a moment. But after a few seconds, your car will give you a little message, asking you to touch the wheel in some capacity.
Powered by WordPress