Quotulatiousness

November 21, 2013

Unexploded shells, submunitions and the “dud” rate

Filed under: History, Military, Technology, Weapons — Tags: , — Nicholas @ 10:56

Strategy Page discusses one of the problems of wars long-gone, but still dangerous today:

These are the many bombs, shells, grenades, and other explosive devices that did not go off when they were supposed to. In the first half of the 20th century, over a billion fuzed devices were used in combat, and five to ten percent of them were duds. In Europe, the site of heavy fighting in two world wars, dozens of people are still killed or injured each year by duds.

In the last few decades of the 20th century it got worse, and the reason was submunitions. These were smaller bombs carried inside a container. The idea was that when the shell or bomb carrying submunitions was used, it would spread these smaller bombs over a larger area and do more damage than one large explosion. It worked, but it also created more duds. Not just more but smaller duds. Small enough for children to pick up and start playing with. Kids are more adventurous and less well informed than adults. A dud submunition looked like a new toy.

[…]

In actual use submunitions turned out to have a higher dud rate than any previous weapon. New artillery shells have a dud rate of about two percent. Israel went so far as to fire 10,000 new shells to confirm that dud rate. But many nations stockpile shells and as these grow older, their dud rate increases. Shells actually have an expiration date, reflecting the fact that the chemicals in the explosives and the fuzes grow more unstable as they age. The Third World and communist nations often had poor quality control to begin with and were more prone to keep old ammunition. During the Afghanistan war of the 1980s, Russian shells appeared to have a dud rate of some thirty percent. And even the United States would sometimes use submunitions that had exceeded their recommended shelf life.

Submunitions were originally designed to have a dud rate similar to that of artillery shells. But in practice it was much higher, closer to five percent. Part of reason for this is the lighter weight of submunitions. Shell fuzes detonate a shell when the shell hits the ground. The impact sends a pretty strong message to the fuze that now is the time to do it, and go bang. But submunitions, weighing from a few ounces to a few pounds, can make a soft landing and not generate enough force to activate the fuze. These make even deadlier duds, for the fuze is not defective, just deceived. When enough force is applied to activate the fuze, you have an explosion. The dud rate got higher depending on where the submunitions landed. When there is a lot of snow or mud on the ground, the dud rate was as high as fifteen percent.
November 20, 2013

An app like this may justify the existence of Google Glass

Filed under: Randomness, Technology — Tags: , , , , , — Nicholas @ 08:38

I have a terrible memory for people’s names (and no, it’s not just early senility … I’ve always had trouble remembering names). For example, I’ve been a member of the same badminton club for nearly 15 years and there are still folks there whose names just don’t register: not just new members, but people I’ve played with or against on dozens of occasions. I know them … I just can’t remember their names in a timely fashion. David Friedman suggests that Google Glass might be the solution I need:

I first encountered the solution to my problem in Double Star, a very good novel by Robert Heinlein. It will be made possible, in a higher tech version, by Google glass. The solution is the Farley File, named after FDR’s campaign manager.

A politician such as Roosevelt meets lots of people over the course of his career. For each of them the meeting is an event to be remembered and retold. It is much less memorable to the politician, who cannot possibly remember the details of ten thousand meetings. He can, however, create the illusion of doing so by maintaining a card file with information on everyone he has ever met: The name of the man’s wife, how many children he has, his dog, the joke he told, all the things the politician would have remembered if the meeting had been equally important to him. It is the job of one of the politician’s assistants to make sure that, any time anyone comes to see him, he gets thirty seconds to look over the card.

My version will use more advanced technology, courtesy of Google glass or one of its future competitors. When I subvocalize the key word “Farley,” the software identifies the person I am looking at, shows me his name (that alone would be worth the price) and, next to it, whatever facts about him I have in my personal database. A second trigger, if invoked, runs a quick search of the web for additional information.

Evernote has an application intended to do some of this (Evernote Hello), but it still requires the immersion-breaking act of accessing your smartphone to look up your contact information. Something similar in a Google Glass or equivalent environment might be the perfect solution.

November 18, 2013

Lifelogging in 30-second intervals

Filed under: Media, Technology — Tags: , , , — Nicholas @ 15:38

Jerry Brito is a sousveillance fan and he thinks you should be too:

The Narrative Clip is a digital camera about the size of a postage stamp that clips to one’s breast pocket or shirt collar and takes a photo every thirty seconds of whatever one’s seeing. The photos are uploaded to the cloud and can be accessed on demand with a smartphone app, making it easy to look up any moment in one’s life. When the project to mass-produce these cameras first hit Kickstarter, I knew I had to have one, and with any luck mine will be arriving in a couple of weeks.

The prospect of having a complete photographic record of my life is compelling for many reasons. I have a terrible memory, especially for faces, so it will be interesting to see if this device can help. There are also moments in life that would be great to relive, but that one can’t – or one doesn’t know one should – be photographing. Narrative’s Instagram feed has some good examples of these. But most importantly, I want to help hasten our inevitable sousveillance future.

[…]

Being monitored in everyday life has become inescapable. So, as David Brin points out in The Transparent Society, the question is not whether there should be pervasive monitoring, but who will have access to the data. Will it only be the powerful, who will use the information to control? Or will the rest of us also be able to watch back?

Ideally, perhaps, we would all be left alone to live private lives under no one’s gaze. Short of halting all technological progress, however, that ship has sailed. Mass surveillance is the inevitable result of smaller cameras and microphones, faster processors, and incredibly cheap storage. So if I can’t change that reality, I want to be able to watch back as well.

November 15, 2013

Near-future investment advice – get out of retail clothing businesses

Filed under: Business, Technology — Tags: , , — Nicholas @ 16:19

As Charles Stross makes clear in his most recent blog post, the way we buy clothes will be changing markedly in the near future:

Fabrican is a unlikely-sounding spin-off of the Department of Chemical Engineering, at Imperial College (which in case you’re not familiar with it is one of the top engineering/science colleges in the UK; formerly part of the University of London) — at least, it’s unlikely until you begin thinking in terms of emulsions, colloids, and the physical chemistry of nanoscale objects. It’s basically fabric in a spray can. Tiny fibres suspended in liquid are ejected through a fine nozzle and, as the supernatant evaporates, they adhere to one another. If at this point you’re thinking The Jetsons and spray-on clothing, have a cigar: you’ve fallen for the obvious marketing angle, because if you’re trying to market a new product and raise brand awareness among the public, what works better than photographs of serious-faced scientists with paint guns spray-painting hot-looking models with skin-tight instant leotards? (Note: the technical term for this sort of marketing gambit is, or really ought to be, bukake couture.)

[…]

What are the implications?

If you don’t think printing woven fabric is a big deal, DARPA beg to differ; DARPA is pumping serious money into robot sewing machines. But automating garment assembly from traditional fabric components turns out to be a really hard problem (as this possibly-paywalled New Scientist article on a €23M project to build a sewbot explains). Cloth is slippery, changes shape if you drop it, wrinkles, and has to be stretched and twisted and folded as it is sewn. Note that final word: sewn. If you can print fabric in situ out of fibres in a liquid form, you don’t need to sew components to shape—especially if you can print more than one type and colour of fibre at a time: you can fabricate your “stitches” (inter-layer connections) as part of the process, with minimal hand-finishing to possibly add fasteners (zips or buttons).

Add in a left-field extra: the rapid spread of millimeter wave scanners for airport security. These devices caused a bit of a to-do, earning them the nick-name “perv scanner” in some circles, because of their ability to see through clothing to the skin beneath, in order to check passengers for hidden contraband. But if you put the same machine in a clothes shop, it allows the establishment to obtain extremely accurate measurements of its customers without requiring a strip-tease and manual measurement of all the relevant saggy, lumpy bits and pieces. By use of surface-penetrating wavelengths (possibly high-intensity laser light, or infrared) it may also be possible to automatically distinguish between fatty tissue, musculature, and underlying bone structure. All of which are relevant to the construction of clothing.

So here’s my picture of the chain store of the future. You go in, go to the scanning booth, and do the airport-equivalent thing in a variety of positions — stretch and bend as well as hands-up. You then look at the styles on display on the shop floor, pick out what you like, and see it as it will appear on your own body on an avatar on a computer screen. You buy it, and a machine in the back of the store (or an out-of-town lights out 24×7 robotic garment factory) begins to print it. Some time later — maybe minutes, maybe hours or a day or two — the outfit you ordered comes to you. And it fits perfectly, every time. Some items are probably still off-the-shelf (socks, hosiery, maybe even those cheap tee shirts), but anything major is printed, unless you can afford to go to the really high end and pay a human being to make it for you out of natural fibres. Oh, and the printed stuff doesn’t have seams in places that chafe or bind.

November 14, 2013

If you like DRM in your computer, you’ll love it in your car

Filed under: Law, Technology, USA — Tags: , , , , , — Nicholas @ 09:05

The Electronic Frontier Foundation thinks that extending the DRM regime to cars (as in the latest vehicle from Renault) will drive consumers crazy:

Forget extra cupholders or power windows: the new Renault Zoe comes with a “feature” that absolutely nobody wants. Instead of selling consumers a complete car that they can use, repair, and upgrade as they see fit, Renault has opted to lock purchasers into a rental contract with a battery manufacturer and enforce that contract with digital rights management (DRM) restrictions that can remotely prevent the battery from charging at all.

We’ve long joined makers and tinkerers in warning that, as software becomes a part of more and more everyday devices, DRM and the legal restrictions on circumventing it will create hurdles to standard repairs and even operation. In the U.S., a car manufacturer who had wrapped its onboard software in technical restrictions could argue that attempts to get around those are in violation of the Digital Millennium Copyright Act (DMCA) — specifically section 1201, the notorious “anti-circumvention” provisions. These provisions make it illegal for users to circumvent DRM or help others do so, even if the purpose is perfectly legal otherwise. Similar laws exist around the world, and are even written into some international trade agreements — including, according to a recently leaked draft, the Trans-Pacific Partnership Agreement.

Since the DMCA became law in 1998, Section 1201 has resulted in countless unintended consequences. It has chilled innovation, stifled the speech of legitimate security researchers, and interfered with consumer rights. Section 1201 came under particular fire this year because it may prevent consumers from unlocking their own phones to use with different carriers. After a broadly popular petition raised the issue, the White House acknowledged that the restriction is out of line with common sense.

How the internet was “weaponized”

Filed under: Government, Technology, USA — Tags: , , , , , — Nicholas @ 07:45

In Wired, Nicholas Weaver looks back on the way the internet was converted from a passive network infrastructure to a spy agency wonderland:

According to revelations about the QUANTUM program, the NSA can “shoot” (their words) an exploit at any target it desires as his or her traffic passes across the backbone. It appears that the NSA and GCHQ were the first to turn the internet backbone into a weapon; absent Snowdens of their own, other countries may do the same and then say, “It wasn’t us. And even if it was, you started it.”

If the NSA can hack Petrobras, the Russians can justify attacking Exxon/Mobil. If GCHQ can hack Belgicom to enable covert wiretaps, France can do the same to AT&T. If the Canadians target the Brazilian Ministry of Mines and Energy, the Chinese can target the U.S. Department of the Interior. We now live in a world where, if we are lucky, our attackers may be every country our traffic passes through except our own.

Which means the rest of us — and especially any company or individual whose operations are economically or politically significant — are now targets. All cleartext traffic is not just information being sent from sender to receiver, but is a possible attack vector.

[…]

The only self defense from all of the above is universal encryption. Universal encryption is difficult and expensive, but unfortunately necessary.

Encryption doesn’t just keep our traffic safe from eavesdroppers, it protects us from attack. DNSSEC validation protects DNS from tampering, while SSL armors both email and web traffic.

There are many engineering and logistic difficulties involved in encrypting all traffic on the internet, but its one we must overcome if we are to defend ourselves from the entities that have weaponized the backbone.

November 12, 2013

Useful answer sheet for new technology effects

Filed under: Humour, Media, Technology — Tags: — Nicholas @ 09:06

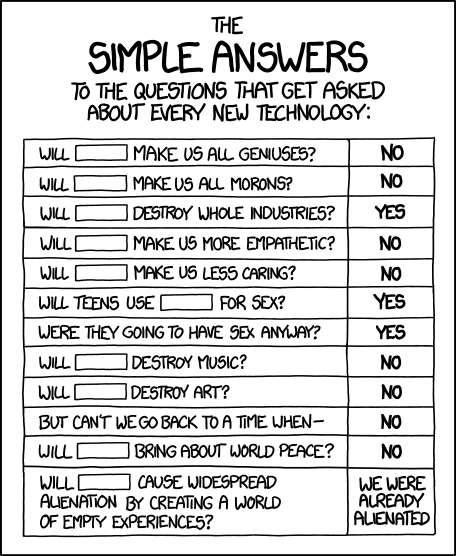
Every time a new technological gizmo comes along, there are some questions which immediately start to be asked (usually by non-tech-savvy journalists). Here’s the XKCD summary sheet of simple answers for technology questions:

Simple Answers

November 11, 2013

The newest menace of the waterways – private submarines

Filed under: Australia, Business, Technology — Tags: , — Nicholas @ 12:24

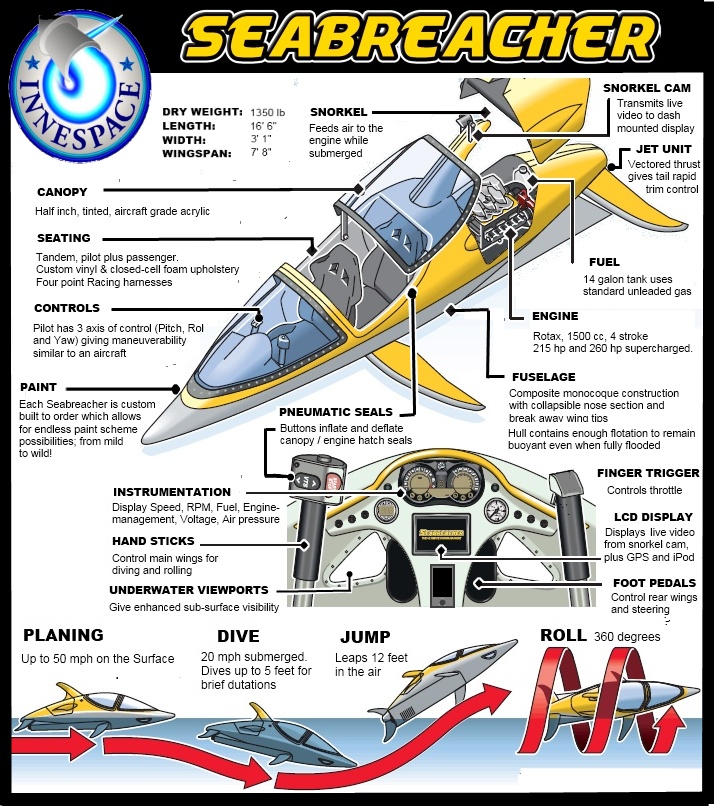
Keeping up with the Joneses has always been a popular hobby among the nouveau riche, and topping the neighbours’ fancy car is only the start of it for some people. If your particular Jones just bought a lovely new pleasure boat, here’s a possible riposte — the Seabreacher J:

Seabreacher J

The Seabreacher J was designed and engineered exclusively for the recreational boating market. This model incorporates a jet drive for increased safety and better surface performance. The J model is able to be registered as a conventional powerboat. It is powered by a Rotax engine which is available in 155hp or 215hp supercharged variants. The engine and jet drive can be easily maintained at any personal watercraft dealership, making it a very basic watercraft to own and operate. The Seabreacher J combines the thrill of flying a submersible watercraft with the practicality and dependability of a conventional personal watercraft. The J model can be custom built with a host of available options that can personalize your Seabreacher to your desires.

The Seabreacher J isn’t a true submarine, but it’s priced for a larger market. To see what they look like in use, a quick Google Image Search turns up lots of “action shots”. True submersibles are also available for more wealthy customers, as Strategy Page explains:

Since the 1990s there have been a lot of recreational submarines. Luxury boat builders have even built submarine yachts. Submarine construction technology has come a long way in the past century, and it’s possible to build these boats at an affordable ($10-200 million) cost. They are safe and there are over a hundred of them out there.

A few companies have gained a lot of experience building subs for non-military underwater operations (academic research, oil exploration), which has created a body of information and cadre of technicians who can build these recreational subs. One of the largest civilian submarine yards is in Dubai, where dozens have been built so far and construction continues. Another large operation in the U.S. has built most of the scientific subs over the last two decades.

The submersible pleasure craft look like streamlined yachts while on the surface. The upper deck, including the bridge, is outside the pressure hull. When submerging, everyone goes below and the upper deck gets flooded. If you get close to one of these yachts it becomes obvious that they are built to dive. Military subs are still not used to encountering this civilian traffic underwater. The military boats have the right of way, but military boats are now warned to exercise extra care when approaching coastal areas used by civilian subs.

Owners of these luxury subs tend to be secretive, and the builders have agreed to some government oversight, especially to make sure militarized subs, that can carry torpedoes or mines, are not built. But there is no law against anyone owning one of these submarines, and it’s feared that it’s only a matter of time before drug dealers, gun runners, or even terrorists, get their hands on some of them. Some police officials believe this has already happened, but no one is saying much. The civilian subs don’t dive as deep as military subs and are not built for combat. They have staterooms and large windows. But they do have carrying capacity, and that could be put to criminal uses. Already, Colombian gangs have been caught trying to build subs, using Russian advisors initially and later just employing the same tech used for recreational subs. Over a hundred submersibles (a sub that travels just below the surface) have been caught carrying cocaine. The age of privately owned subs is here.

November 9, 2013

Barack Obama on the difference between private enterprise and government

Filed under: Bureaucracy, Business, Government, Technology, USA — Tags: , , , — Nicholas @ 11:43

Ann Althouse finds it amazing that President Obama clearly understands why his campaign website was so effective and why the Obamacare website fails on so many levels, but can’t generalize that knowledge to the whole public/private sphere:

In yesterday’s interview with Chuck Todd, Obama said:

    You know, one of the lessons — learned from this whole process on the website — is that probably the biggest gap between the private sector and the federal government is when it comes to I.T. …

    Well, the reason is is that when it comes to my campaign, I’m not constrained by a bunch of federal procurement rules, right?

That is, many have pointed out that his campaign website was really good, so why didn’t that mean that he’d be good at setting up a health insurance website? The answer is that the government is bad because the government is hampered by… government!

    And how we write — specifications and — and how the — the whole things gets built out. So part of what I’m gonna be looking at is how do we across the board, across the federal government, leap into the 21st century.

I love the combination of: 1. Barely able to articulate what the hell happens inside these computer systems, and 2. Wanting to leap!

    Because when it comes to medical records for veterans, it’s still done in paper. Medicaid is still largely done on paper.

    When we buy I.T. services generally, it is so bureaucratic and so cumbersome that a whole bunch of it doesn’t work or it ends up being way over cost.

This should have made him sympathetic to the way government burdens private enterprise, but he’s focused on liberating government to take over more of what has been done privately. And yet there’s no plan, no idea about what would suddenly enable government to displace private businesses competing to offer a product people want to buy.

November 6, 2013

Taiwan suffers espionage leak

Filed under: China, Military, Technology, USA — Tags: , , , , — Nicholas @ 09:17

Strategy Page on the most recent intelligence coup by the Chinese military:

Taiwan recently admitted that it had suffered some serious damage when it discovered that one of its air force officers (identified only as “Major Hao”) sold many technical details of the new E-2K AWACS (Airborne Warning and Control System) aircraft to China. Hao did it for money, and Taiwanese counterintelligence found over a dozen other Chinese intel operatives during the investigation that uncovered the E-2K leaks. Since the E-2K contains mostly American technology and is based on the E-2C use on American aircraft carriers, this intelligence disaster is going to cost America a lot as well. Since China now knows the details of how the E-2 electronics work, they can develop better ways to deceive and disrupt E-2 operations.

Earlier this year Taiwan received the last two of four E-2K aircraft from the U.S., where they have been sent for upgrading to the E-2C 2000 standard. The first two E-2Ks were sent in 2009. The upgrade cost about $63 million per aircraft. Taiwan bought two E-2Ks new in 2006 as well.

The Taiwanese E-2K is very similar to the American E-2C, which is being replaced with a newer model. In 2010 the U.S. Navy received its first E-2D aircraft. This is the latest version of the E-2 Hawkeye radar aircraft that was originally introduced in 1964. The two engine, 24 ton E-2 was never produced in large quantities (fewer than a hundred are in use). Six years ago the E-2 fleet reached a milestone of a million flight hours.

[…]

The U.S. usually does not export the latest versions of electronic equipment. Thus the Taiwan leak means the older American E-2C is compromised but not (to a great extent) the most recent E-2D model. But the Taiwanese are justifiably afraid that there will be even more reluctance by the United States to sell Taiwan the latest versions of anything because of the successful Chinese espionage efforts in Taiwan. Then again, maybe not. That’s because that espionage works both ways. The Taiwanese have been very successful using the same tactics (offering cash or using blackmail and other threats) against the Chinese. While the American and Taiwanese tech is more valuable (because it is more advanced) it’s useful to know the details of the best stuff the Chinese have.

November 4, 2013

QotD: Software quality assurance

Filed under: Business, Government, Quotations, Technology — Tags: , , , — Nicholas @ 10:13

The fundamental purpose of testing—and, for that matter, of all software quality assurance (QA) deliverables and processes — is to tell you just what you’ve built and whether it does what you think it should do. This is essential, because you can’t inspect a software program the same way you can inspect a house or a car. You can’t touch it, you can’t walk around it, you can’t open the hood or the bedroom door to see what’s inside, you can’t take it out for spin. There are very few tangible or visible clues to the completeness and reliability of a software system — and so we have to rely on QA activities to tell us how well built the system is.

Furthermore, almost any software system developed nowadays for production is vastly more complex than a house or car — it’s more on the same order of complexity of a large petrochemical processing and storage facility, with thousands of possible interconnections, states, and processes. We would be (rightly) terrified if, say, Exxon build such a sprawling oil refining complex near our neighborhood and then started up production having only done a bare minimum of inspection, testing, and trial operations before, during and after construction, offering the explanation that they would wait until after the plant went into production and then handle problems as they crop up. Yet too often that’s just how large software development projects are run, even though the system in development may well be more complex (in terms of connections, processes, and possible states) than such a petrochemical factory. And while most inadequately tested software systems won’t spew pollutants, poison the neighborhood, catch fire, or explode, they can cripple corporate operations, lose vast sums of money, spark shareholder lawsuits, and open the corporation’s directors and officers to civil and even criminal liability (particularly with the advent of Sarbanes-Oxley).

And that presumes that the system can actually go into production. The software engineering literature and the trade press are replete with well-documented case studies of “software runaways”: large IT re-engineering or development projects that consume tens or hundreds of millions of dollars, or in a few spectacular (government) cases, billions of dollars, over a period of years, before grinding to a halt and being terminated without ever having put a usable, working system into production. So it’s important not to skimp on testing and the other QA-related activities.

Bruce F. Webster, “Obamacare and the Testing Gap”, And Still I Persist…, 2013-10-31

Living in a Surveillance State: Mikko Hypponen at TEDxBrussels

Filed under: Liberty, Technology, USA — Tags: , , , , — Nicholas @ 00:01

November 1, 2013

Let’s hope badBIOS is an elaborate Halloween hoax

Filed under: Technology — Tags: , , , , , — Nicholas @ 08:05

Dan Goodin posted a scary Halloween tale at Ars Technica yesterday … at least, I’m hoping it’s just a scary story for the season:

In the intervening three years, Ruiu said, the infections have persisted, almost like a strain of bacteria that’s able to survive extreme antibiotic therapies. Within hours or weeks of wiping an infected computer clean, the odd behavior would return. The most visible sign of contamination is a machine’s inability to boot off a CD, but other, more subtle behaviors can be observed when using tools such as Process Monitor, which is designed for troubleshooting and forensic investigations.

Another intriguing characteristic: in addition to jumping “airgaps” designed to isolate infected or sensitive machines from all other networked computers, the malware seems to have self-healing capabilities.

“We had an air-gapped computer that just had its [firmware] BIOS reflashed, a fresh disk drive installed, and zero data on it, installed from a Windows system CD,” Ruiu said. “At one point, we were editing some of the components and our registry editor got disabled. It was like: wait a minute, how can that happen? How can the machine react and attack the software that we’re using to attack it? This is an air-gapped machine and all of a sudden the search function in the registry editor stopped working when we were using it to search for their keys.”

Over the past two weeks, Ruiu has taken to Twitter, Facebook, and Google Plus to document his investigative odyssey and share a theory that has captured the attention of some of the world’s foremost security experts. The malware, Ruiu believes, is transmitted though USB drives to infect the lowest levels of computer hardware. With the ability to target a computer’s Basic Input/Output System (BIOS), Unified Extensible Firmware Interface (UEFI), and possibly other firmware standards, the malware can attack a wide variety of platforms, escape common forms of detection, and survive most attempts to eradicate it.

But the story gets stranger still. In posts here, here, and here, Ruiu posited another theory that sounds like something from the screenplay of a post-apocalyptic movie: “badBIOS,” as Ruiu dubbed the malware, has the ability to use high-frequency transmissions passed between computer speakers and microphones to bridge airgaps.

October 31, 2013

A garage of historical significance

Filed under: History, Technology, USA — Tags: , , — Nicholas @ 08:28

In The Register, a remarkably blasé report on the designation of the house where Jobs and Wozniak created the first Apple computers:

The house where Steve Jobs built his first computers has been added to a list of historic buildings in Los Altos.

The Los Altos Historical Commission voted unanimously to add the home at 2066 Crist Drive as a historic resources, since its hallowed garage was where Jobs made his first computers and co-founded Apple, the San Jose Mercury News reported.

The commission’s report said that it had been reviewing the property for potential designation for the past two years due to its “association with an event and an individual of historic significance”.

From other discussion on the topic, this will require the current owner of the property (Patricia Jobs, the sister of the late Steve Jobs) to get the commission’s advance permission to do any kind of work on the house … including ordinary maintenance. No funds from the municipality go along with this designation: once your house has been so designated, you no longer exercise full rights of ownership, but you still are required to pay for any work the commission deems necessary or desirable. Ms Jobs apparently still has a right to appeal, but I don’t know what her chances of success might be.

The drug-running submarine squadron

Filed under: Americas, Law, Technology — Tags: , , , — Nicholas @ 07:25

Strategy Page reports that the set of almost-complete submarines built by a drug cartel in Colombia were much more sophisticated and capable than first thought:

The leader (Mauner Mahecha) of the project was a guy in his early 30s with no boat building experience but excellent organizational and leadership skills.

Mahecha had a huge budget and used it to find and hire men with the needed skills or experience with submarines. Mahecha also quickly recruited additional specialists as needed and obtained whatever materials the builders called for. His project built three submarines, and the project was shut down because one of the men recruited (an experienced engine mechanic working for the Colombian Navy) managed to tip off the Colombian Navy intelligence and then the U.S. about the project.

[…]

The Mahecha submarines, when closely examined by experts, turned out to be more sophisticated than first thought. The outer hull was made out of strong, lightweight, Kevlar/carbon fiber that was sturdy enough to keep the sub intact but very difficult to detect with most sensors. The hull could not survive deep dives but this boat didn’t have to go deep to get the job done. The diesel-electric power supply (up to two-hundred and forty-nine lead-acid batteries), diving and surfacing system, and navigational systems of captured subs were all in working order. Those who built these boats apparently borrowed much from recreational subs. The sub builders also had impressive knowledge of the latest materials used to build exotic boats.

The three fiberglass/Kevlar submarines were obviously built to transport cocaine to North America and the existence of a building effort had been detected by intel agencies. For several years before the submarine boat yard was discovered the U.S. Navy, in cooperation with some Central and South American navies, have been looking for these subs, at sea and on land. While these submarines didn’t run very deep (less than twenty meters/sixty-two feet), they are invisible to most sensors when completely submerged. These subs were designed to run on batteries for up to eighteen hours, before having to surface and recharge. When they are at sea, they usually operate their diesel engines. These are noisy. Sonar can pick up this noise over a long distance. By capturing these subs it was possible to run the engines and get a sound profile of this type of boat and equip American sonar systems with this data. These subs had a range (on internal fuel) of about twelve-thousand kilometers. Thus, the boat could get from Colombia to southern California and back. These drug gangs spent over two million on each of these subs.

The most potent weapon the U.S. Navy has against these tiny (less than thirty-four meters/one-hundred foot long) subs is heat sensors, but even that may have had limited effectiveness. That’s because one of the subs captured had a snorkel type device (a tall structure extending from the conning tower, which contained pipes allowing diesel exhaust to escape and fresh air to be brought into the submerged boat.) It’s this heat that airborne sensors can detect. All surface (or semi-submerged) ships at sea display this kind of “heat signature”, and capturing working examples of these cocaine smuggling subs makes it possible to get a better idea of what the airborne heat sensors should be looking for. A snorkel, however, puts out less heat that a sub running on the surface would and is harder to detect. When running on batteries there is no heat to detect.

« Newer PostsOlder Posts »

Powered by WordPress