Quotulatiousness

June 13, 2014

Supreme Court rules unanimously in favour of internet privacy

Filed under: Cancon, Law, Liberty, Technology — Tags: , , , , — Nicholas @ 13:11

Some great news on the privacy front, this time a decision handed down by the Supreme Court of Canada, as reported by Michael Geist:

This morning another voice entered the discussion and completely changed the debate. The Supreme Court of Canada issued its long-awaited R. v. Spencer decision, which examined the legality of voluntary warrantless disclosure of basic subscriber information to law enforcement. In a unanimous decision written by (Harper appointee) Justice Thomas Cromwell, the court issued a strong endorsement of Internet privacy, emphasizing the privacy importance of subscriber information, the right to anonymity, and the need for police to obtain a warrant for subscriber information except in exigent circumstances or under a reasonable law.

I discuss the implications below, but first some of the key findings. First, the Court recognizes that there is a privacy interest in subscriber information. While the government has consistently sought to downplay that interest, the court finds that the information is much more than a simple name and address, particular in the context of the Internet. As the court states:

    the Internet has exponentially increased both the quality and quantity of information that is stored about Internet users. Browsing logs, for example, may provide detailed information about users’ interests. Search engines may gather records of users’ search terms. Advertisers may track their users across networks of websites, gathering an overview of their interests and concerns. “Cookies” may be used to track consumer habits and may provide information about the options selected within a website, which web pages were visited before and after the visit to the host website and any other personal information provided. The user cannot fully control or even necessarily be aware of who may observe a pattern of online activity, but by remaining anonymous – by guarding the link between the information and the identity of the person to whom it relates – the user can in large measure be assured that the activity remains private.

Given all of this information, the privacy interest is about much more than just name and address.

Second, the court expands our understanding of informational privacy, concluding that there three conceptually distinct issues: privacy as secrecy, privacy as control, and privacy as anonymity. It is anonymity that is particularly notable as the court recognizes its importance within the context of Internet usage. Given the importance of the information and the ability to link anonymous Internet activities with an identifiable person, a high level of informational privacy is at stake.

Third, not only is there a significant privacy interest, but there is also a reasonable expectation of privacy by the user. The court examines both PIPEDA and the Shaw terms of use (the ISP in this case) and concludes that PIPEDA must surely be understood within the context of protecting privacy (not opening the door to greater disclosures) and that the ISP agreement was confusing at best and may support the expectation of privacy. With those findings in mind:

    in the totality of the circumstances of this case, there is a reasonable expectation of privacy in the subscriber information. The disclosure of this information will often amount to the identification of a user with intimate or sensitive activities being carried out online, usually on the understanding that these activities would be anonymous. A request by a police officer that an ISP voluntarily disclose such information amounts to a search.

Fourth, having concluded that obtaining subscriber information was a search with a reasonable expectation of privacy, the information was unconstitutionally obtained therefore led to an unlawful search. Addressing the impact of the PIPEDA voluntary disclosure clause, the court notes:

    Since in the circumstances of this case the police do not have the power to conduct a search for subscriber information in the absence of exigent circumstances or a reasonable law, I do not see how they could gain a new search power through the combination of a declaratory provision and a provision enacted to promote the protection of personal information.

Update, 7 July: A few weeks later, the US Supreme Court also made a strong pro-privacy ruling, this one mandating a warrant for police to search the contents of a cellphone.

Politico‘s Josh Gerstein has more on the ruling in in Riley v. California:

The Supreme Court’s blunt and unequivocal decision Wednesday giving Americans strong protection against arrest-related searches of their cell phones could also give a boost to lawsuits challenging the National Security Agency’s vast collection of phone call data.

Chief Justice John Roberts’s 28-page paean to digital privacy was like music to the ears of critics of the NSA’s metadata program, which sweeps up details on billions of calls and searches them for possible links to terrorist plots.

“This is a remarkably strong affirmation of privacy rights in a digital age,” said Marc Rotenberg of the Electronic Privacy Information Center. “The court found that digital data is different and that has constitutional significance, particularly in the realm of [the] Fourth Amendment…I think it also signals the end of the NSA program.”

Roberts’s opinion is replete with rhetoric warning about the privacy implications of access to data in individuals’ smart phones, including call logs, Web search records and location information. Many of the arguments parallel, or are virtually identical to, the ones privacy advocates have made about the dangers inherent in the NSA’s call metadata program.
June 12, 2014

Winnipeg Grade 9 students successfully hack Bank of Montreal ATM

Filed under: Business, Cancon, Technology — Tags: , , , , — Nicholas @ 08:00

“Hack” is the wrong word here, as it implies they did something highly technical and unusual. What they did was to use the formal documentation for the ATM and demonstrate that the installer had failed to change the default administrator password:

Matthew Hewlett and Caleb Turon, both Grade 9 students, found an old ATM operators manual online that showed how to get into the machine’s operator mode. On Wednesday over their lunch hour, they went to the BMO’s ATM at the Safeway on Grant Avenue to see if they could get into the system.

“We thought it would be fun to try it, but we were not expecting it to work,” Hewlett said. “When it did, it asked for a password.”

Hewlett and Turon were even more shocked when their first random guess at the six-digit password worked. They used a common default password. The boys then immediately went to the BMO Charleswood Centre branch on Grant Avenue to notify them.

When they told staff about a security problem with an ATM, they assumed one of their PIN numbers had been stolen, Hewlett said.

“I said: ‘No, no, no. We hacked your ATM. We got into the operator mode,'” Hewlett said.

“He said that wasn’t really possible and we don’t have any proof that we did it.

“I asked them: ‘Is it all right for us to get proof?’

“He said: ‘Yeah, sure, but you’ll never be able to get anything out of it.’

“So we both went back to the ATM and I got into the operator mode again. Then I started printing off documentation like how much money is currently in the machine, how many withdrawals have happened that day, how much it’s made off surcharges.

“Then I found a way to change the surcharge amount, so I changed the surcharge amount to one cent.”

As further proof, Hewlett playfully changed the ATM’s greeting from “Welcome to the BMO ATM” to “Go away. This ATM has been hacked.”

They returned to BMO with six printed documents. This time, staff took them seriously.

A lot of hardware is shipped with certain default security arrangements (known admin accounts with pre-set passwords, for example), and it’s part of the normal installation/configuration process to change them. A lazy installer may skip this, leaving the system open to inquisitive teens or more technically adept criminals. These two students were probably lucky not to be scapegoated by the bank’s security officers.

June 8, 2014

Modern weapons would make a D-Day style landing almost impossible

Filed under: Military, Technology, Weapons — Tags: , , , — Nicholas @ 11:34

At The Diplomat, Zachary Keck looks at how the evolution of military technology would make future D-Day style invasions much more difficult:

Seaborne invasions are one of, if not the most, difficult kind of military operation. That is partially why, as Mearsheimer points out, the great stopping power of water is so consequential in international politics. At first glance, it might seem like the innovations in transportation and communication technology that have triggered globalization would make contemporary amphibious assaults easier

Not so, however. To begin with, many of the basic challenges that have always plagued seaborne invasions are rooted in geography, which remains relatively fixed. Namely, the defending force in amphibious invasions are usually heavily fortified while the landing force typically has to initially fight in the open. The landing force also remains extremely vulnerable before actually reaching land, especially since the defending force can rely on land-based defense systems.

In fact, as Stratfor, a private global intelligence firm, points out, modern defense technologies have made amphibious assaults much more difficult. The most “significant development” since World War II, Stratfor points out, is precision-guided munitions (these did exist in rudimentary form during the conflict). The analysis goes to explain:

“A contemporary landing force would approach the beachhead in an amphibious landing vehicle such as the U.S. Assault Amphibious Vehicle, which moves at around 13 kph (8 mph). This would be vulnerable to anti-tank guided missiles fired from positions onshore. On D-Day, ships in the Allied invasion fleet were also able to come relatively close to shore to deploy landing craft. The deadly threat of anti-ship cruise missiles in modern warfare would force a modern fleet to remain farther out to sea, leaving amphibious vehicles even more exposed.”

This last point is especially important. As Sydney Freedberg noted back in April, “The new [Marine] Corps concept, Expeditionary Force 21, predicts long-range threats will force the fleet to stay at least 65 nautical miles offshore, a dozen times the distance that existing Marine amphibious vehicles are designed to swim.”

Smaller invasions against undefended coastline — think of both the initial Argentinian attack on the Falkland Islands and the British counter-attack as examples — are still possible, especially in bolt-from-the-blue surprise fashion, but an attack against an active defence with modern weapons might well be unacceptably hard for even the US Marine Corps.

June 5, 2014

Living in a post-Snowden world, under the gaze of the Five Eyes

Filed under: Australia, Cancon, Government, Technology, USA — Tags: , , , , — Nicholas @ 07:12

It’s been a year since the name Edward Snowden became known to the world, and it’s been a bumpy ride since then, as we found out that the tinfoil-hat-wearing anti-government conspiracy theorists were, if anything, under-estimating the actual level of organized, secret government surveillance. At The Register, Duncan Campbell takes us inside the “FIVE-EYED VAMPIRE SQUID of the internet”, the five-way intelligence-sharing partnership of US/UK/Canada/Australia/New Zealand:

One year after The Guardian opened up the trove of top secret American and British documents leaked by former National Security Agency (NSA) sysadmin Edward J Snowden, the world of data security and personal information safety has been turned on its head.

Everything about the safety of the internet as a common communication medium has been shown to be broken. As with the banking disasters of 2008, the crisis and damage created — not by Snowden and his helpers, but by the unregulated and unrestrained conduct the leaked documents have exposed — will last for years if not decades.

Compounding the problem is the covert network of subornment and control that agencies and collaborators working with the NSA are now revealed to have created in communications and computer security organisations and companies around the globe.

The NSA’s explicit objective is to weaken the security of the entire physical fabric of the net. One of its declared goals is to “shape the worldwide commercial cryptography market to make it more tractable to advanced cryptanalytic capabilities being developed by the NSA”, according to top secret documents provided by Snowden.

Profiling the global machinations of merchant bank Goldman Sachs in Rolling Stone in 2009, journalist Matt Taibbi famously characterized them as operating “everywhere … a great vampire squid wrapped around the face of humanity, relentlessly jamming its blood funnel into anything that smells like money”.

The NSA, with its English-speaking “Five Eyes” partners (the relevant agencies of the UK, USA, Australia, New Zealand and Canada) and a hitherto unknown secret network of corporate and government partners, has been revealed to be a similar creature. The Snowden documents chart communications funnels, taps, probes, “collection systems” and malware “implants” everywhere, jammed into data networks and tapped into cables or onto satellites.

June 4, 2014

Sarcasm-detecting software wanted

Filed under: Media, Technology — Tags: , , , , — Nicholas @ 09:02

Charles Stross discusses some of the second-order effects should the US Secret Service actually get the sarcasm-detection software they’re reportedly looking for:

… But then the Internet happened, and it just so happened to coincide with a flowering of highly politicized and canalized news media channels such that at any given time, whoever is POTUS, around 10% of the US population are convinced that they’re a baby-eating lizard-alien in a fleshsuit who is plotting to bring about the downfall of civilization, rather than a middle-aged male politician in a business suit.

Well now, here’s the thing: automating sarcasm detection is easy. It’s so easy they teach it in first year computer science courses; it’s an obvious application of AI. (You just get your Turing-test-passing AI that understands all the shared assumptions and social conventions that human-human conversation rely on to identify those statements that explicitly contradict beliefs that the conversationalist implicitly holds. So if I say “it’s easy to earn a living as a novelist” and the AI knows that most novelists don’t believe this and that I am a member of the set of all novelists, the AI can infer that I am being sarcastic. Or I’m an outlier. Or I’m trying to impress a date. Or I’m secretly plotting to assassinate the POTUS.)

Of course, we in the real world know that shaved apes like us never saw a system we didn’t want to game. So in the event that sarcasm detectors ever get a false positive rate of less than 99% (or a false negative rate of less than 1%) I predict that everybody will start deploying sarcasm as a standard conversational gambit on the internet.

Wait … I thought everyone already did?

Trolling the secret service will become a competitive sport, the goal being to not receive a visit from the SS in response to your totally serious threat to kill the resident of 1600 Pennsylvania Avenue. Al Qaida terrrrst training camps will hold tutorials on metonymy, aggressive irony, cynical detachment, and sarcasm as a camouflage tactic for suicide bombers. Post-modernist pranks will draw down the full might of law enforcement by mistake, while actual death threats go encoded as LOLCat macros. Any attempt to algorithmically detect sarcasm will fail because sarcasm is self-referential and the awareness that a sarcasm detector may be in use will change the intent behind the message.

As the very first commenter points out, a problem with this is that a substantial proportion of software developers (as indicated by their position on the Asperger/Autism spectrum) find it very difficult to detect sarcasm in real life…

Bruce Schneier on the human side of the Heartbleed vulnerability

Filed under: Technology — Tags: , , , — Nicholas @ 07:24

Reposting at his own site an article he did for The Mark News:

The announcement on April 7 was alarming. A new Internet vulnerability called Heartbleed could allow hackers to steal your logins and passwords. It affected a piece of security software that is used on half a million websites worldwide. Fixing it would be hard: It would strain our security infrastructure and the patience of users everywhere.

It was a software insecurity, but the problem was entirely human.

Software has vulnerabilities because it’s written by people, and people make mistakes — thousands of mistakes. This particular mistake was made in 2011 by a German graduate student who was one of the unpaid volunteers working on a piece of software called OpenSSL. The update was approved by a British consultant.

In retrospect, the mistake should have been obvious, and it’s amazing that no one caught it. But even though thousands of large companies around the world used this critical piece of software for free, no one took the time to review the code after its release.

The mistake was discovered around March 21, 2014, and was reported on April 1 by Neel Mehta of Google’s security team, who quickly realized how potentially devastating it was. Two days later, in an odd coincidence, researchers at a security company called Codenomicon independently discovered it.

When a researcher discovers a major vulnerability in a widely used piece of software, he generally discloses it responsibly. Why? As soon as a vulnerability becomes public, criminals will start using it to hack systems, steal identities, and generally create mayhem, so we have to work together to fix the vulnerability quickly after it’s announced.

May 30, 2014

“French spies [are] number two in the world of industrial cyber-espionage”

Filed under: China, Europe, France, Government, Technology, USA — Tags: , — Nicholas @ 08:11

High praise indeed for French espionage operatives from … former US Secretary of Defence Robert Gates:

Former spy and defense department secretary Robert Gates has identified France as a major cyber-spying threat against the US.

In statements that are bound to raise eyebrows on both sides of the Atlantic, Gates (not Bill) nominated French spies as being number two in the world of industrial cyber-espionage.

“In terms of the most capable, next to the Chinese, are the French – and they’ve been doing it a long time” he says in this interview at the Council on Foreign Relations.

Rather than a precis, The Register will give you some of Gates’s (not Bill) words verbatim, starting just after 21 minutes in the video, when he answers a question about America’s recent indictment of five Chinese military hackers.

“What we have accused the Chinese of doing – stealing American companies’ secrets and technology – is not new, nor is it something that’s done only by the Chinese,” Gates tells the interviewer. “There are probably a dozen or fifteen countries that steal our technology in this way.

“In terms of the most capable, next to the Chinese, are probably the French, and they’ve been doing it a long time.

May 27, 2014

Internet privacy advice for kids (who are not “Digital Natives”)

Filed under: Business, Media, Technology — Tags: , , , , , — Nicholas @ 13:15

Cory Doctorow sympathizes with young people who have literally grown up with the internet:

The problem with being a “digital native” is that it transforms all of your screw-ups into revealed deep truths about how humans are supposed to use the Internet. So if you make mistakes with your Internet privacy, not only do the companies who set the stage for those mistakes (and profited from them) get off Scot-free, but everyone else who raises privacy concerns is dismissed out of hand. After all, if the “digital natives” supposedly don’t care about their privacy, then anyone who does is a laughable, dinosauric idiot, who isn’t Down With the Kids.

“Privacy” doesn’t mean that no one in the world knows about your business. It means that you get to choose who knows about your business.

It’s difficult to explain to people just how open their online “secrets” really are … and that’s not even covering the folks who are specifically targets of active surveillance … just being on Facebook or other social media sites hands over a lot of your personal details without your direct knowledge or (informed) consent. But you can start to take back some of your own privacy online:

If you start using computers when you’re a little kid, you’ll have a certain fluency with them that older people have to work harder to attain. As Douglas Adams wrote:

  1. Anything that is in the world when you’re born is normal and ordinary and is just a natural part of the way the world works.
  2. Anything that’s invented between when you’re fifteen and thirty-five is new and exciting and revolutionary and you can probably get a career in it.
  3. Anything invented after you’re thirty-five is against the natural order of things.

If I was a kid today, I’d be all about the opsec — the operational security. I’d learn how to use tools that kept my business between me and the people I explicitly shared it with. I’d make it my habit, and get my friends into the habit too (after all, it doesn’t matter if all your email is encrypted if you send it to some dorkface who keeps it all on Google’s servers in unscrambled form where the NSA can snaffle it up).

Here’s some opsec links to get you started:

  • First of all, get a copy of Tails, AKA “The Amnesic Incognito Live System.” This is an operating system that you can use to boot up your computer so that you don’t have to trust the OS it came with to be free from viruses and keyloggers and spyware. It comes with a ton of secure communications tools, as well as everything you need to make the media you want to send out into the world.
  • Next, get a copy of The Tor Browser Bundle, a special version of Firefox that automatically sends your traffic through something called TOR (The Onion Router, not to be confused with Tor Books, who publish my novels). This lets you browse the Web with a much greater degree of privacy and anonymity than you would otherwise get.
  • Learn to use GPG, which is a great way to encrypt (scramble) your emails. There’s a Chrome plugin for using GPG with Gmail, and another version for Firefox
  • If you like chatting, get OTR, AKA “Off the Record,” a very secure private chat tool that has exciting features like “perfect forward secrecy” (this being a cool way of saying, even if someone breaks this tomorrow, they won’t be able to read the chats they captured today).

Once you’ve mastered that stuff, start to think about your phone. Android phones are much, much easier to secure than Apple’s iPhones (Apple tries to lock their phones so you can’t install software except through their store, and because of a 1998 law called the DMCA, it’s illegal to make a tool to unlock them). There are lots of alternative operating systems for Android, of varying degrees of security. The best place to start is Cyanogenmod, which makes it much easier to use privacy tools with your mobile device.

WSJ – “…the Canadian government is paying almost 80% of his developers’ salaries”

Filed under: Business, Cancon, Economics, Government, Technology — Tags: , , — Nicholas @ 07:32

Stephen Gordon linked to this rather boggling Wall Street Journal article that outlines how the Canadian and provincial governments are attempting to lure start-up technology businesses to locate in Canada with vast bribes of taxpayer money:

Imagine you are launching or running a startup and there’s a place where all of your developers — the biggest expense for most tech companies — cost one quarter what they do in Silicon Valley. Sure, it’s cold there, but talent is plentiful and the locals are friendly. Would you trade your hash browns for poutine?

Adam Adelman, co-founder of Mighty Cast, a startup working on a new kind of wearable technology, recently told me the Canadian government is paying almost 80% of his developers’ salaries. And that’s not a tax credit. It’s a rebate, a check he gets from the government whether or not his startup makes money.

Even at Mighty Cast, a two-year-old hardware startup, salaries have been 80% of expenses. Combine that with the lower salaries demanded by engineers in Montreal, where Mighty Cast moved its headquarters after its genesis in Silicon Valley, and Mr. Adelman says he’s able to stretch his angel round of investment four times as far.

So the federal government is literally giving away money to start-up tech companies to compete at a huge advantage against actual Canadian companies? Nearly 80% of the payroll is funded from taxes, partly collected from the domestic competition? Does this seem like a good idea to anyone who isn’t already drawing 100% of their income from Ottawa?

The government is particularly badly suited to picking technology winners, and this program sounds like a vast give-away for the well-connected few, literally at the expense of everyone else. Maple-flavoured crony capitalism, with the official stamp of approval of Stephen Harper’s “conservative” government.

May 25, 2014

Russian rocket export ban means increasing opportunities for private enterprise in space

Filed under: Russia, Space, Technology, USA — Tags: , , , , — Nicholas @ 09:46

Strategy Page looks at the knock-on effects of the Russian government banning the export of rocket engines to the United States:

The U.S. government is being forced to use satellite launchers developed without government financing because the usual methods of obtaining these launchers is falling apart and currently is unable to supply enough rockets to get all American military satellites into orbit. The immediate cause of this problem is the recent (since earlier this year) Russian aggression against Ukraine. The U.S. responded to this aggression by placing sanctions on some Russian officials and firms. Russia responded to that by halting RD-180 shipments to the United States. That’s breach of contract and it will do enormous damage to Russian exports in the future because now many countries and firms realize that a contract with a Russian firm can be cancelled by the Russian government for any reason. This was always seen as a risk when doing business with Russia and many Western firms declined to do so or have pulled out of Russia in the last decade because of the growing unreliability of Russia as a business partner. The RD-180 affair got a lot of publicity, all of it bad with regard to future Russian exports of high-end industrial items. Europe, which gets about a third of its natural gas from Russia, is already looking for alternate sources and investors are fleeing Russia (and taking their money with them).

[…]

This is good news for the new private firms that are developing rockets for launching stuff into orbit. One such firm is SpaceX (Space Exploration Technologies Corporation) and is has been trying to break the current cartel controlling U.S. government satellite launch services. Since 2006 all this business has gone to a government-approved monopoly called the ULA (United Launch Alliance) which is composed of Lockheed Martin (Atlas 5 rocket) and Boeing (Delta 4). These two firms have dominated U.S. space launches for over half a century. Because of the RD-180 the Atlas 5 is more attractive (in terms of performance and price) than the Delta 4. Meanwhile SpaceX expects to have Atlas 5 competitor ready in a few years.

In 2012 SpaceX obtained its first contract to launch U.S. military cargo into space. SpaceX had earlier obtained a NASA contract which included 12 deliveries to the International Space Station (at $134 million each). What makes all this so noteworthy is that SpaceX developed its own launch rockets without any government help. SpaceX also developed the Dragon space vehicle, for delivering personnel and supplies to the International Space Station.

SpaceX has since proved that its rockets work and is pointing out that the SpaceX rockets can do the job cheaper that ULA. Currently ULA gets a billion dollar a year subsidy from the government that SpaceX would not require. SpaceX still has to get all the paperwork and approvals done so that they can handle classified missions. SpaceX does not see this as a problem, it’s simply going to take another year to satisfy all the bureaucrats and regulations.

May 24, 2014

The technological democratization of law enforcement and the rise of “Little Brother”

Filed under: Liberty, Technology, USA — Tags: , , , , — Nicholas @ 09:44

If you care about your privacy, you’re equally worried about the intrusive surveillance state and the unconstrained snooping of corporations. You may now need to worry about your snoopy neighbours also getting in on the act, as Declan McCullagh explains on Google+. This is a response to someone on a private mailing list for Silicon Valley folks, who said that he had no issue with automated collection of license plate data:

Tomorrow one of your PV [Portola Valley] neighbors will set up a computer-connected camera on private property and aimed at the street. It records all those “plates exposed” going by and, by doing optical character recognition with free software such as ANPR MX (C# code, BSD-licensed), it records every time a car goes by. The DMV will happily provide drivers’ names based on the license plate*; there’s even a process for “bulk quantities” of data.** That information doesn’t include a home address, but that’s easy to come by through other searches.

Then the neighbor launches PVPeopleTracker.com. It updates in real time showing whenever someone is at home, and marks their house in bright red if they’re gone on an extended trip. If there are odd patterns of movement compared to a baseline — perhaps suspicious late-night outings — those can be flagged as well. Any visitor to PVPeopleTracker.com can sign up for handy free email alerts reporting at what time their targeted house becomes vacant each weekday morning. Other network-linked cameras in PV can supplement the PVPeopleTracker.com database, so that everyone driving in town will have their movements monitored, archived, and publicly visible at all times.

With more than one network-linked camera separated by a known distance by roads with known speed limits, it would be simple to calculate speeding violations and send automated alerts, with MP4 videos attached as evidence, to the sheriff and CHP. PVPeopleTracker.com can also be cross-referenced against databases showing, say, marijuana convictions; if your movement profile matches a known drug trafficker, law enforcement can be alerted. (Sorry about those false positives!)

May 23, 2014

QotD: Futurologists

Futurologists are almost always wrong. Indeed, Clive James invented a word – “Hermie” – to denote an inaccurate prediction by a futurologist. This was an ironic tribute to the cold war strategist and, in later life, pop futurologist Herman Kahn. It was slightly unfair, because Kahn made so many fairly obvious predictions – mobile phones and the like – that it was inevitable quite a few would be right.

Even poppier was Alvin Toffler, with his 1970 book Future Shock, which suggested that the pace of technological change would cause psychological breakdown and social paralysis, not an obvious feature of the Facebook generation. Most inaccurate of all was Paul R Ehrlich who, in The Population Bomb, predicted that hundreds of millions would die of starvation in the 1970s. Hunger, in fact, has since declined quite rapidly.

Perhaps the most significant inaccuracy concerned artificial intelligence (AI). In 1956 the polymath Herbert Simon predicted that “machines will be capable, within 20 years, of doing any work a man can do” and in 1967 the cognitive scientist Marvin Minsky announced that “within a generation … the problem of creating ‘artificial intelligence’ will substantially be solved”. Yet, in spite of all the hype and the dizzying increases in the power and speed of computers, we are nowhere near creating a thinking machine.

Bryan Appleyard, “Why futurologists are always wrong – and why we should be sceptical of techno-utopians: From predicting AI within 20 years to mass-starvation in the 1970s, those who foretell the future often come close to doomsday preachers”, New Statesman, 2014-04-10.

May 16, 2014

The built-in confusion about net neutrality

While I’ve been following the net neutrality debate, I was still unconvinced that either side had the answers. In a post from 2008, ESR helps to explain why I was confused:

Let it be clear from the outset that the telcos are putting their case for being allowed to do these things with breathtaking hypocrisy. They honk about how awful it is that regulation keeps them from setting their own terms, blithely ignoring the fact that their last-mile monopoly is entirely a creature of regulation. In effect, Theodore Vail and the old Bell System bribed the Feds to steal the last mile out from under the public’s nose between 1878 and 1920; the wireline telcos have been squatting on that unnatural monopoly ever since as if they actually had some legitimate property right to it.

But the telcos’ crimes aren’t merely historical. They have repeatedly bargained for the right to exclude competitors from their networks on the grounds that if the regulators would let them do that, they’d be able to generate enough capital to deploy broadband everywhere. That promise has been repeatedly, egregiously broken. Instead, they’ve creamed off that monopoly rent as profit or used it to cross-subsidize competition in businesses with higher rates of return. (Oh, and of course, to bribe legislators and buy regulators.)

Mistake #1 for libertarians to avoid is falling for the telcos’ “we’re pro-free market” bullshit. They’re anything but; what they really want is a politically sheltered monopoly in which they have captured the regulators and created business conditions that fetter everyone but them.

OK, so if the telcos are such villainous scum, the pro-network-neutrality activists must be the heroes of this story, right?

Unfortunately, no.

Your typical network-neutrality activist is a good-government left-liberal who is instinctively hostile to market-based approaches. These people think, rather, that if they can somehow come up with the right regulatory formula, they can jawbone the government into making the telcos play nice. They’re ideologically incapable of questioning the assumption that bandwidth is a scarce “public good” that has to be regulated. They don’t get it that complicated regulations favor the incumbent who can afford to darken the sky with lawyers, and they really don’t get it about outright regulatory capture, a game at which the telcos are past masters.

[…]

In short, the “network neutrality” crowd is mainly composed of well-meaning fools blinded by their own statism, and consequently serving mainly as useful idiots for the telcos’ program of ever-more labyrinthine and manipulable regulation. If I were a telco executive, I’d be on my knees every night thanking my god(s) for this “opposition”. Mistake #2 for any libertarian to avoid is backing these clowns.

In the comments, he summarizes “the history of the Bell System’s theft of the last mile”.

May 15, 2014

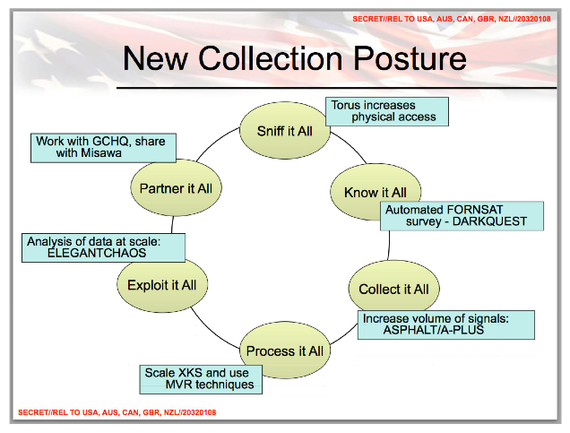
The NSA’s self-described mission – “Collect it all. Know it all. Exploit it all.”

Filed under: Government, Liberty, Media, Technology — Tags: , , , , — Nicholas @ 07:31

In The Atlantic, Conor Friedersdorf reviews Glenn Greenwald’s new book, No Place to Hide:

NSA - New Collection Posture

Collect it all. Know it all. Exploit it all.

That totalitarian approach came straight from the top. Outgoing NSA chief Keith Alexander began using “collect it all” in Iraq at the height of the counterinsurgency. Eventually, he aimed similar tools at hundreds of millions of innocent people living in liberal democracies at peace, not war zones under occupation.

The strongest passages in No Place to Hide convey the awesome spying powers amassed by the U.S. government and its surveillance partners; the clear and present danger they pose to privacy; and the ideology of the national-security state. The NSA really is intent on subverting every method a human could use to communicate without the state being able to monitor the conversation.

U.S. officials regard the unprecedented concentration of power that would entail to be less dangerous than the alternative. They can’t conceive of serious abuses perpetrated by the federal government, though recent U.S. history offers many examples.

[…]

But it is a mistake (albeit a common one) to survey the NSA-surveillance controversy and to conclude that Greenwald represents the radical position. His writing can be acerbic, mordant, biting, trenchant, scathing, scornful, and caustic. He is stubbornly uncompromising in his principles, as dramatized by how close he came to quitting The Guardian when it wasn’t moving as fast as he wanted to publish the first story sourced to Edward Snowden. Unlike many famous journalists, he is not deferential to U.S. leaders.

Yet tone and zeal should never be mistaken for radicalism on the core question before us: What should America’s approach to state surveillance be? “Defenders of suspicionless mass surveillance often insist … that some spying is always necessary. But this is a straw man … nobody disagrees with that,” Greenwald explains. “The alternative to mass surveillance is not the complete elimination of surveillance. It is, instead, targeted surveillance, aimed only at those for whom there is substantial evidence to believe they are engaged in real wrongdoing.”

That’s as traditionally American as the Fourth Amendment.

Targeted surveillance “is consistent with American constitutional values and basic precepts of Western justice,” Greenwald continues. Notice that the authority he most often cites to justify his position is the Constitution. That’s not the mark of a radical. In fact, so many aspects of Greenwald’s book and the positions that he takes on surveillance are deeply, unmistakably conservative.

May 14, 2014

Turning pixel weapons into bronze and steel

Filed under: Gaming, Technology, Weapons — Tags: , — Nicholas @ 07:41

I thought this Geek & Sundry project might be interesting. It’s called Arcade Arms and the idea is they take a weapon from an online game and try to create a real-world version, then use that to see what kind of damage you can do with it. The first episode is about a massively oversize mace from the game Elder Scrolls Online:

Published on 13 May 2014

Jake Powning shows Nika Harper how to forge the Mace of Molag Bal, featured in The Elder Scrolls series. Then Andre Sinou shows her how much damage a mace can really do!

Get Elder Scrolls Online for yourself: http://www.elderscrollsonline.com

In Arcade Arms Nika brings gaming into real life by taking the most potent digital weapons, from Final Fantasy XIV‘s Gae Bolg to Elder Scrolls Online‘s Mace of Molag Bal, and smashing things with their real life counterparts.

Real world downer note: most single-handed weapons were significantly lighter than this fantasy mace: it clocks in at 35 pounds, which is a lot more weight than you’d be able to swing in a real fight (their combat demonstrator also points this out … and note how much smaller the examples he shows are compared to the “Mace of Molag Bal”).

I’d hoped there would be more “how we made this” footage, but I understand the majority of the audience only really want to see how much damage the weapon can do…

« Newer PostsOlder Posts »

Powered by WordPress