Quotulatiousness

July 16, 2014

Rolling Stone is your top source for reliable, informative gun news

Filed under: Media, Technology, USA, Weapons — Tags: , , — Nicholas @ 08:10

The folks at Rolling Stone are concerned for your safety, so they’ve helpfully put together a primer on the five “most dangerous” guns in America. Because they love you, America:

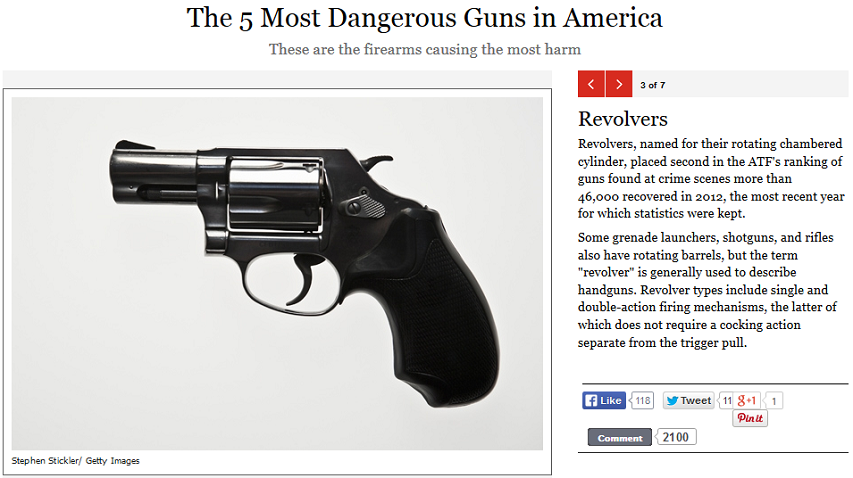
Rolling Stone dangerous guns 3

Yes, we’re apparently talking about grenade launchers here. I didn’t even know grenade launchers were available to civilians. Awesome!

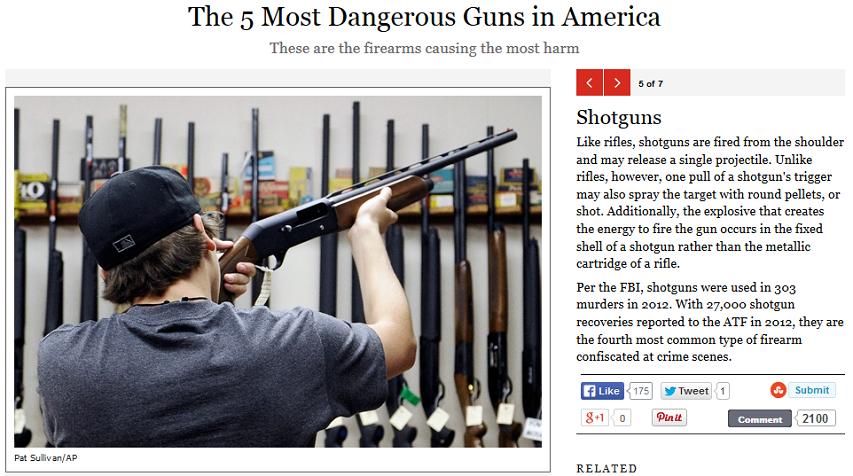
Rolling Stone dangerous guns 5

Wait, “the explosive that creates the energy to fire the gun occurs in the fixed shell of a shotgun rather than the metallic cartridge of a rifle”. Why would I expect the charge that propels the shot out of a shotgun to be ignited in a rifle cartridge? Is this some sort of magic that allows you to fire a different weapon than the one you’re holding? No wonder Rolling Stone thinks this is such a dangerous weapon!

H/T to Charles C. W. Cooke for the link.

July 15, 2014

The sheer difficulty of obtaining a warrant

Filed under: Government, Law, Liberty, Technology, USA — Tags: , , , — Nicholas @ 08:21

Tim Cushing wonders why we don’t seem to sympathize with the plight of poor, overworked law enforcement officials who find the crushing burden of getting a warrant for accessing your cell phone data to be too hard:

You’d think approved warrants must be like albino unicorns for all the arguing the government does to avoid having to run one by a judge. It continually acts as though there aren’t statistics out there that show obtaining a warrant is about as difficult as obeying the laws of thermodynamics. Wiretap warrants have been approved 99.969% of the time over the last decade. And that’s for something far more intrusive than cell site location data.

But still, the government continues to argue that location data, while possibly intrusive, is simply Just Another Business Record — records it is entitled to have thanks to the Third Party Doctrine. Any legal decision that suggests even the slightest expectation of privacy might have arisen over the past several years as the public’s relationship with cell phones has shifted from “luxury item/business tool” to “even grandma has a smartphone” is greeted with reams of paper from the government, all of it metaphorically pounding on the table and shouting “BUSINESS RECORDS!”

When that fails, it pushes for the lower bar of the Stored Communications Act [PDF] to be applied to its request, dropping it from “probable cause” to “specific and articulable facts.” The Stored Communications Act is the lowest bar, seeing as it allows government agencies and law enforcement to access electronic communications older than 180 days without a warrant. It’s interesting that the government would invoke this to defend the warrantless access to location metadata, seeing as the term “communications” is part of the law’s title. This would seem to imply what’s being sought is actual content — something that normally requires a higher bar to obtain.

Update: Ken White at Popehat says warrants are not particularly strong devices to protect your liberty and lists a few distressing cases where warrants have been issued recently.

We’re faced all the time with the ridiculous warrants judges will sign if they’re asked. Judges will sign a warrant to give a teenager an injection to induce an erection so that the police can photograph it to fight sexting. Judges will, based on flimsy evidence, sign a warrant allowing doctors to medicate and anally penetrate a man because he might have a small amount of drugs concealed in his rectum. Judges will sign a warrant to dig up a yard based on a tip from a psychic. Judges will kowtow to an oversensitive politician by signing a warrant to search the home of the author of a patently satirical Twitter account. Judges will give police a warrant to search your home based on a criminal libel statute if your satirical newspaper offended a delicate professor. And you’d better believe judges will oblige cops by giving them a search warrant when someone makes satirical cartoons about them.

I’m not saying that warrants are completely useless. Warrants create a written record of the government’s asserted basis for an action, limiting cops’ ability to make up post-hoc justifications. Occasionally some prosecutors turn down weak warrant applications. The mere process of seeking a warrant may regulate law enforcement behavior soomewhat.

Rather, I’m saying that requiring the government to get a warrant isn’t the victory you might hope. The numbers — and the experience of criminal justice practitioners — suggests that judges in the United States provide only marginal oversight over what is requested of them. Calling it a rubber stamp is unfair; sometimes actual rubber stamps run out of ink. The problem is deeper than court decisions that excuse the government from seeking warrants because of the War on Drugs or OMG 9/11 or the like. The problem is one of the culture of the criminal justice system and the judiciary, a culture steeped in the notion that “law and order” and “tough on crime” are principled legal positions rather than political ones. The problem is that even if we’d like to see the warrant requirement as interposing neutral judges between our rights and law enforcement, there’s no indication that the judges see it that way.

The economic side of Net Neutrality

Filed under: Business, Economics, Technology — Tags: , , , , — Nicholas @ 07:41

In Forbes, Tim Worstall ignores the slogans to follow the money in the Net Neutrality argument:

The FCC is having a busy time of it as their cogitations into the rules about net neutrality become the second most commented upon in the organisation’s history (second only to Janet Jackson’s nip-slip which gives us a good idea of the priorities of the citizenry). The various internet content giants, the Googles, Facebooks and so on of this world, are arguing very loudly that strict net neutrality should be the standard. We could, of course attribute this to all in those organisations being fully up with the hippy dippy idea that information just wants to be free. Apart from the obvious point that Zuckerberg, for one, is a little too young to have absorbed that along with the patchouli oil we’d probably do better to examine the underlying economics of what’s going on to work out why people are taking the positions they are.

Boiling “net neutrality” down to its essence the argument is about whether the people who own the connections to the customer, the broadband and mobile airtime providers, can treat different internet traffic differently. Should we force them to be neutral (thus the “neutrality” part) and treat all traffic exactly the same? Or should they be allowed to speed up some traffic, slow down other, in order to prioritise certain services over others?

We can (and many do) argue that we the consumers are paying for this bandwidth so it’s up to us to decide and we might well decide that they cannot. Others might (and they do) argue that certain services require very much more of that bandwidth than others, further, require a much higher level of service, and it would be economically efficient to charge for that greater volume and quality. For example, none of us would mind all that much if there was a random second or two delay in the arrival of a gmail message but we’d be very annoyed if there were random such delays in the arrival of a YouTube packet. Netflix would be almost unusable if streaming were subject to such delays. So it might indeed make sense to prioritise such traffic and slow down other to make room for it.

You can balance these arguments as you wish: there’s not really a “correct” answer to this, it’s a matter of opinion. But why are the content giants all arguing for net neutrality? What’s their reasoning?

As you’d expect, it all comes down to the money. Who pays more for what under a truly “neutral” model and who pays more under other models. The big players want to funnel off as much of the available profit to themselves as possible, while others would prefer the big players reduced to the status of regulated water company: carrying all traffic at the same rate (which then allows the profits to go to other players).

The attraction (and danger) of computer-based models

Filed under: Environment, Science, Technology — Tags: , , — Nicholas @ 00:02

Warren Meyer explains why computer models can be incredibly useful tools, but they are not the same thing as an actual proof:

    Among the objections, including one from Green Party politician Chit Chong, were that Lawson’s views were not supported by evidence from computer modeling.

I see this all the time. A lot of things astound me in the climate debate, but perhaps the most astounding has been to be accused of being “anti-science” by people who have such a poor grasp of the scientific process.

Computer models and their output are not evidence of anything. Computer models are extremely useful when we have hypotheses about complex, multi-variable systems. It may not be immediately obvious how to test these hypotheses, so computer models can take these hypothesized formulas and generate predicted values of measurable variables that can then be used to compare to actual physical observations.

[…]

The other problem with computer models, besides the fact that they are not and cannot constitute evidence in and of themselves, is that their results are often sensitive to small changes in tuning or setting of variables, and that these decisions about tuning are often totally opaque to outsiders.

I did computer modelling for years, though of markets and economics rather than climate. But the techniques are substantially the same. And the pitfalls.

Confession time. In my very early days as a consultant, I did something I am not proud of. I was responsible for a complex market model based on a lot of market research and customer service data. Less than a day before the big presentation, and with all the charts and conclusions made, I found a mistake that skewed the results. In later years I would have the moral courage and confidence to cry foul and halt the process, but at the time I ended up tweaking a few key variables to make the model continue to spit out results consistent with our conclusion. It is embarrassing enough I have trouble writing this for public consumption 25 years later.

But it was so easy. A few tweaks to assumptions and I could get the answer I wanted. And no one would ever know. Someone could stare at the model for an hour and not recognize the tuning.

July 10, 2014

Throwing a bit of light on security in the “internet of things”

Filed under: Technology — Tags: , , , , — Nicholas @ 07:36

The “internet of things” is coming: more and more of your surroundings are going to be connected in a vastly expanded internet. A lot of attention needs to be paid to security in this new world, as Dan Goodin explains:

In the latest cautionary tale involving the so-called Internet of things, white-hat hackers have devised an attack against network-connected lightbulbs that exposes Wi-Fi passwords to anyone in proximity to one of the LED devices.

The attack works against LIFX smart lightbulbs, which can be turned on and off and adjusted using iOS- and Android-based devices. Ars Senior Reviews Editor Lee Hutchinson gave a good overview here of the Philips Hue lights, which are programmable, controllable LED-powered bulbs that compete with LIFX. The bulbs are part of a growing trend in which manufacturers add computing and networking capabilities to appliances so people can manipulate them remotely using smartphones, computers, and other network-connected devices. A 2012 Kickstarter campaign raised more than $1.3 million for LIFX, more than 13 times the original goal of $100,000.

According to a blog post published over the weekend, LIFX has updated the firmware used to control the bulbs after researchers discovered a weakness that allowed hackers within about 30 meters to obtain the passwords used to secure the connected Wi-Fi network. The credentials are passed from one networked bulb to another over a mesh network powered by 6LoWPAN, a wireless specification built on top of the IEEE 802.15.4 standard. While the bulbs used the Advanced Encryption Standard (AES) to encrypt the passwords, the underlying pre-shared key never changed, making it easy for the attacker to decipher the payload.

July 8, 2014

The wine trade, legal “adjuncts”, and honest labelling

Filed under: Law, Technology, USA, Wine — Tags: , — Nicholas @ 14:47

In Wired, Christopher Null talks to Californian winemaker Paul Draper about what’s actually in the wine that you buy:

Unlike most food and drink, wine and other alcoholic beverages are governed not by the Food and Drug Administration (part of Health and Human Services) but by the Alcohol and Tobacco Tax and Trade Bureau (part of the U.S. Treasury). As the name suggests, the TTB’s primary goal is to collect taxes on booze and cigarettes, a longstanding vestige of Prohibition. Consumers have largely been left in the dark about what’s really inside the bottle.

Not everyone is thrilled about this, and as with many secrecy-laden industries, transparency is a buzzword that has a few wine industry leaders twittering. Their savior is Paul Draper, who has been lambasting adjuncts for years and who eschews their use at Ridge, where he’s been the chief winemaker since 1969. A legend in the business, his Cabernet placed fifth in the famous Judgment of Paris in 1976. His newest, somewhat Quixotic quest: to introduce full and truthful labeling to wine bottles. Ridge has published real ingredients labels on its bottles since 2012.

While Draper dislikes adjuncts, the enemy, he says, isn’t just cheap wine: It’s also winemakers’ increasing thirst for wines that are ready to drink without significant aging. This not only drives consumer sales, it also helps to drive higher scores from wine critics, as even professionals can struggle to rate a wine based on its future potential.

That in turn has led to a more nefarious way in which adjuncts are being deployed. While they are often used as an easy way to make cheap wine more palatable, adjuncts are increasingly being applied to high-end wines to eke another couple of points out of the critics. “You have that machine. It costs a half a million or a million dollars and it’s sitting in your winery,” Draper says. “The temptation to use it in years when you don’t need to use it is immense.” But ultimately, he complains, “If you use these techniques, you aren’t making fine wine.”

You’d think the various adjuncts wouldn’t make it past the sommeliers, high-end buyers, and big-name critics of the wine world, that such chemical or mechanical shortcuts would be picked up by their well-trained palates. But the truth is that these things can’t be sniffed, tasted, or spotted unless they are overused.

July 6, 2014

Even if you’re “doing nothing wrong”, the NSA is probably tracking you already

Filed under: Government, Liberty, Media, Technology, USA — Tags: , , , — Nicholas @ 09:17

The argument that you’ve got nothing to worry about because you’re not doing anything wrong has long since passed its best-before date. As Nick Gillespie points out, you don’t need to be a member of Al Qaeda, a black-hat hacker, or a registered Republican to be of interest to the NSA’s information gathering team:

If You’re Reading Reason.com, The NSA is Probably Already Following You

Two things to contemplate on early Sunday morning, before church or political talk shows get underway:

Remember all those times we were told that the government, especially the National Security Agency (NSA), only tracks folks who either guilty of something or involved in suspicious-seeming activity? Well, we’re going to have amend that a bit. Using documents from Edward Snowden, the Washington Post‘s Barton Gellman, Julie Tate, and Ashkan Soltani report

    Ordinary Internet users, American and non-American alike, far outnumber legally targeted foreigners in the communications intercepted by the National Security Agency from U.S. digital networks, according to a four-month investigation by The Washington Post.

    Nine of 10 account holders found in a large cache of intercepted conversations, which former NSA contractor Edward Snowden provided in full to The Post, were not the intended surveillance targets but were caught in a net the agency had cast for somebody else.

    Many of them were Americans. Nearly half of the surveillance files, a strikingly high proportion, contained names, e-mail addresses or other details that the NSA marked as belonging to U.S. citizens or residents. NSA analysts masked, or “minimized,” more than 65,000 such references to protect Americans’ privacy, but The Post found nearly 900 additional e-mail addresses, unmasked in the files, that could be strongly linked to U.S. citizens or U.S.residents.

The cache of documents in question date from 2009 through 2012 and comprise 160,000 documents collected up the PRISM and Upstream, which collect data from different sources. “Most of the people caught up in those programs are not the targets and would not lawfully qualify as such,” write Gellman, Julie Tate, and Ashkan Soltani, who also underscore that NSA surveillance has produced some very meaningful and good intelligence. The real question is whether the government can do that in a way that doesn’t result in massive dragnet programs that create far more problems ultimately than they solve (remember the Church Committee?).

Read the whole thing. And before anyone raises the old “if you’re innocent, you’ve got nothing to hide shtick,” read Scott Shackford’s “3 Reasons the ‘Nothing to Hide’ Crowd Should be worried about Government Surveillance.”

July 5, 2014

The mystic art of going viral – The Putter

Filed under: Britain, Business, Media, Technology — Tags: , — Nicholas @ 13:02

This is Collosal posted a lovely little video a few days ago, showing how one small century-old firm in Sheffield still “puts-together” scissors in the old way:

It’s been a popular video. It’s been a very popular video. In fact, it went viral.

The staff at Ernest Wright and Son Limited have been overwhelmed with interest from people who saw the video and decided they wanted a pair of hand-made scissors. A member of one of my mailing lists says he just got this response from the company about his order (placed before the video went online):

Dear Madam or Sir,

Firstly, may we thank you VERY MUCH for ordering a pair (or more) of our Hand-made in Sheffield England, Ernest Wright and Son Limited scissors.

Secondly, may I please take a moment to explain our current situation.

As you doubtless know, Shaun Bloodworth’s film “The Putter” was uploaded to the internet on Monday 23rdJune. We had been very much looking forward to seeing this film, if purely as an educational exercise documenting the immense skills of the ‘putter-togetherer’.

What we might not have expected was that Shaun’s own amazing skill, coupled with the gorgeous sound work from The Black Dog (wow!), would make such a beautiful and sensory-encompassing experience of something we just see our Cliff and Eric do every day.

And what we REALLY didn’t expect was for this film to go ‘viral’! This was not a ‘commercial launch’ by any means at all; so much as Shaun merely uploading the film for us back here in the factory to see. The power of the internet is truly an incredible and awesome thing.

This has rather caught us at an ‘interesting’ time. We have not been doing particularly well for a number of years as a business and have worryingly dwindled in size. Recently we actually had to make further redundancies and at a few times have thought that the end was truly nigh for Ernest Wright’s altogether. Cheap scissors are ubiquitous; no-one seems (seemed!) particularly interested in how scissors are made any more, and hardly anyone understood paying the price for a good pair – regardless of how we have ever tried to explain it. (Enter Shaun and “The Putter” – and what a benefit, hopefully, to us all!)

There are now just the five of us here in our little business:

Cliff and Eric are our putter-togetherers, although Cliff does the vast majority of the putting whilst Eric is also a skilled hand-grinder and finisher. Eric’s hands are actually those seen working the ‘insider’ machine in The Putter, linishing the inside of the bows (handles) with sparks flying in either direction. These two are both working through retirement years now – purely helping me to keep something we feel is so important, alive.

It would be remiss of me not to mention Ian, who eventually only retired last autumn (2013). All three can be seen here together by the way in a 2012 BBC documentary – http://www.youtube.com/watch?v=IitTC4PqcOI

These chaps have never earned too much – and there honestly hasn’t been too much to earn for a while. But they work hard; so very, very hard. And until around about this Tuesday, they had incredibly little appreciation for their life’s devotion to their craft. I am genuinely so touched that they are finally getting a mention, they so thoroughly deserve it.

We also now have young Jamie and Ryan, who are ‘the young blood’ apprentices and have been with us for around two years now. They began by learning tapping, grinding, then linishing, and are now slowly learning the full art of putting-together themselves – although not at all yet commercially. Practice will one day hopefully make them perfect.

Finally I am the managing director, van driver, salesman, go-fetcher and hopelessly-part-time receptionist. Ernest Wright was my great-grandfather, who formed the company in 1902. I took over when my father almost decided to close the business in 2012, and have since made it my mission in life to save these skills and their type – particularly in Sheffield, the hometown I am so very proud of.

So. Basically after a very long spell of quiet, since around Tuesday morning this week we have been suddenly inundated. With (gratefully) telephone calls, emails, tweets, views, messages, letters and (very gratefully) individual orders. I am honestly struggling to keep up at the moment. The telephone system has crashed and my inbox cannot download fast enough.

Regardless my aim is this: everyone who has ordered a pair of Cliff and Eric’s wonderful-handiwork scissors will receive them; as speedily and safely as is possible.

Ironically Cliff had gone off a well-earned holiday on Monday, and will be sitting in a deck chair in Filey or somewhere for the next week yet – hopefully wondering why on earth he is being asked for an autograph! He knows nothing about his new-found ‘internet popularity’, although he will be completely shy and modest about it as always when he finds out. Only Shaun’s down-to-earth and inconspicuous approach led him to be even filmed in the first place. Regardless I’m sure he will be pleased he can “learn some more” and get cracking with his hammer upon his return.

I cannot honestly promise how long these scissors are going to take to get to you at the moment! we haven’t yet worked out how many of each type are even required. Then they take a little while to be made – but you might know that now! One thing we won’t do, because Cliff and Eric would refuse every time, is to ‘do a rush job’. Your scissors might not always look quite perfect either, but that’s not what we 100% care about. Every pair might have a tiny mark, a scratch, a blemish or even the odd hammer dent, but that is precisely because they are hand, and not machine, made. They are made to be used, not looked at, is our opinion. What we concentrate on more than anything is that they work. Perfectly, every time. I actually reckon you that you can see that in Cliff’s face though, I’ve seen that a thousand times off-camera too.

We are working on strict order-date basis. I am hoping to keep up with at least broadcast emails for the next week until we see how much of a potential flash-in-the-pan this may be. It would be sadly more ironical than anything if this great new interest hurt us rather than helped, so please give me some time to address this situation properly? Meantime we have managed to send out quite a lot of orders already but the previous held-stock is now very low and new orders are still arriving! The lads are certainly preparing to get busy – apart from poor oblivious Cliff in his deckchair at the moment of course.

If orders are going to take more than one month to arrive, I will try to let you know in the next week? I hope that’s ok, it is honestly the very best we can do for now!

If you would prefer a refund, of course I understand completely. Please email me by reply to nick.wright@ernestwright.co.ukwith the title just “REFUND” and at least your order number (usually 4 digits) in the text. I will then get to it as soon as I also can.

Meantime THANK YOU so much, both to old followers and many new friends, for this amazing and wonderful support. This might be our chance for once to shine again. I will try my level best to reciprocate as much as I possibly can.

Yours with kindest regards,

Nick.

Nick Wright
Director
Ernest Wright and Son Limited

www.ernestwright.co.uk
July 2, 2014

Security threats and security myths

Filed under: Technology — Tags: , , — Nicholas @ 09:48

In Wired, Peter W. Singer And Allan Friedman analyze five common myths about online security:

“A domain for the nerds.” That is how the Internet used to be viewed back in the early 1990s, until all the rest of us began to use and depend on it. But this quote is from a White House official earlier this year describing how cybersecurity is too often viewed today. And therein lies the problem, and the needed solution.

Each of us, in whatever role we play in life, makes decisions about cybersecurity that will shape the future well beyond the world of computers. But by looking at this issue as only for the IT Crowd, we too often do so without the proper tools. Basic terms and essential concepts that define what is possible and proper are being missed, or even worse, distorted. Some threats are overblown and overreacted to, while others are ignored.

Perhaps the biggest problem is that while the Internet has given us the ability to run down the answer to almost any question, cybersecurity is a realm where past myth and future hype often weave together, obscuring what actually has happened and where we really are now. If we ever want to get anything effective done in securing the online world, we have to demystify it first.

[…]

Myth #2: Every Day We Face “Millions of Cyber Attacks”

This is what General Keith Alexander, the recently retired chief of US military and intelligence cyber operations, testified to Congress in 2010. Interestingly enough, leaders from China have made similar claims after their own hackers were indicted, pointing the finger back at the US. These numbers are both true and utterly useless.

Counting individual attack probes or unique forms of malware is like counting bacteria — you get big numbers very quickly, but all you really care about is the impact and the source. Even more so, these numbers conflate and confuse the range of threats we face, from scans and probes caught by elementary defenses before they could do any harm, to attempts at everything from pranks to political protests to economic and security related espionage (but notably no “Cyber Pearl Harbors,” which have been mentioned in government speeches and mass media a half million times). It’s a lot like combining everything from kids with firecrackers to protesters with smoke bombs to criminals with shotguns, spies with pistols, terrorists with grenades, and militaries with missiles in the same counting, all because they involve the same technology of gunpowder.

June 30, 2014

Has your Facebook feed been particularly “down” lately?

Filed under: Media, Technology — Tags: , , — Nicholas @ 08:42

If so, you may have been involuntarily recruited to take part in a “scientific” study as Facebook tailored hundreds of thousands of users’ feeds to show them only good news or only bad news:

As you may have heard (since it appears to have become the hyped up internet story of the weekend), the Proceedings of the National Academy of Sciences (PNAS) recently published a study done by Facebook, with an assist from researchers at UCSF and Cornell, in which they directly tried (and apparently succeeded) to manipulate the emotions of 689,003 users of Facebook for a week. The participants — without realizing they were a part of the study — had their news feeds “manipulated” so that they showed all good news or all bad news. The idea was to see if this made the users themselves feel good or bad. Contradicting some other research which found that looking at photos of your happy friends made you sad, this research apparently found that happy stuff in your feed makes you happy. But, what’s got a lot of people up in arms is the other side of that coin: seeing a lot of negative stories in your feed, appears to make people mad.

There are, of course, many different ways to view this: and the immediate response from many is “damn, that’s creepy.”

Did you know that your terms of service with Facebook allow this? I suspect a lot of Facebook users had no clue that their newsfeeds could be (and regularly are) manipulated without their awareness and consent.

If anything, what I think this does is really to highlight how much Facebook manipulates the newsfeed. This is something very few people seem to think about or consider. Facebook‘s newsfeed system has always been something of a black box (which is a reason that I prefer Twitter‘s setup where you get the self-chosen firehose, rather than some algorithm (or researchers’ decisions) picking what I get to see). And, thus, in the end, while Facebook may have failed to get the level of “informed consent” necessary for such a study, it may have, in turn, done a much better job accidentally “informing” a lot more people how its newsfeeds get manipulated. Whether or not that leads more people to rely on Facebook less, well, perhaps that will be the subject of a future study…

Related: Brendan posted this the other day, and I found it quite amusing.

June 23, 2014

Justice Department staff fall for phishing scam simulation

Filed under: Cancon, Government, Technology — Tags: , — Nicholas @ 06:36

This doesn’t speak well of the federal government’s staff security training:

Many of the Justice Department’s finest legal minds are falling prey to a garden-variety Internet scam.

An internal survey shows almost 2,000 staff were conned into clicking on a phoney “phishing” link in their email, raising questions about the security of sensitive information.

The department launched the mock scam in December as a security exercise, sending emails to 5,000 employees to test their ability to recognize cyber fraud.

The emails looked like genuine communications from government or financial institutions, and contained a link to a fake website that was also made to look like the real thing.

What’s even more interesting is that the government bureaucrats fell for this scam at a far higher rate than average Canadian internet users:

The Justice Department’s mock exercise caught 1,850 people clicking on the phoney embedded links, or 37 per cent of everyone who received the emails.

That’s a much higher rate than for the general population, which a federal website says is only about five per cent.

The exercise did not put any confidential information at risk, but the poor results raise red flags about public servants being caught by actual phishing emails.

A spokeswoman says “no privacy breaches have been reported” from any real phishing scams at Justice Canada.

Carole Saindon also said that two more waves of mock emails in February and April show improved results, with clicking rates falling by half.

So in an earlier test, our public servants were clicking on phishing links well over 50% of the time? Yikes.

June 21, 2014

The science of booze

Filed under: History, Science, Technology, Wine — Tags: , , — Nicholas @ 09:18

Mankind has been making alcoholic beverages for thousands of years, yet there are still some pretty basic things we don’t know about alcohol:

Consider the number of things we still don’t know: Yeast, the single-celled fungus responsible for fermentation (the conversion of sugar into alcohol), seems to have been domesticated about 12,000 years ago, but we don’t know for sure where it came from, why it makes ethanol, or why some strains do it better than others.

The physics of distillation are well established, but nobody knows who invented it — an alchemist in ancient Alexandria called Maria the Jewess? — and getting a consistent taste from the finicky process is more an art than a science.

Aging in toasted barrels clearly does hooch good, as the wood breaks down and the liquid penetrates its pores to mix with tannins and other molecules. But the final flavor of a spirit depends on everything from the temperature in the warehouse where it is aged to the climate where the trees are grown, and attempts to create synthetic processes to season liquor quicker (read: more profitably) have come mostly to naught.

Even at the most basic level, scientists don’t yet understand why booze makes us feel the way it does. Alcohol’s mode of action in the brain is much more complicated and elusive than that of a drug such as heroin, which locks into specific, identified receptors meant for natural neurotransmitters. “The truth is, we don’t know at the molecular level what alcohol is binding to,” Rogers quotes the director of the National Institute on Alcohol Abuse and Alcoholism as saying. “It’s never been resolved.”

June 18, 2014

The liability concern in the future of driverless cars

Filed under: Law, Technology — Tags: , , , — Nicholas @ 08:04

Tim Worstall asks when it would be appropriate for your driverless car to kill you:

Owen Barder points out a quite delightful problem that we’re all going to have to come up with some collective answer to over the driverless cars coming from Google and others. Just when is it going to be acceptable that the car kills you, the driver, or someone else? This is a difficult public policy question and I’m really not sure who the right people to be trying to solve it are. We could, I guess, given that it is a public policy question, turn it over to the political process. It is, after all, there to decide on such questions for us. But given the power of the tort bar over that process I’m not sure that we’d actually like the answer we got. For it would most likely mean that we never do get driverless cars, at least not in the US.

The basic background here is that driverless cars are likely to be hugely safer than the current human directed versions. For most accidents come about as a result of driver error. So, we expect the number of accidents to fall considerably as the technology rolls out. This is great, we want this to happen. However, we’re not going to end up with a world of no car accidents. Which leaves us with the problem of how do we program the cars to work when there is unavoidably going to be an accident?

[…]

So we actually end up with two problems here. The first being the one that Barder has outlined, which is that there’s an ethical question to be answered over how the programming decisions are made. Seriously, under what circumstances should a driverless car, made by Google or anyone else, be allowed to kill you or anyone else? The basic Trolly Problem is easy enough, kill fewer people by preference. But when one is necessary which one? And then a second problem which is that the people who have done the coding are going to have to take legal liability for that decision they’ve made. And given the ferocity of the plaintiff’s bar at times I’m not sure that anyone will really be willing to make that decision and thus adopt that potential liability.

Clearly, this needs to be sorted out at the political level. Laws need to be made clarifying the situation. And hands up everyone who thinks that the current political gridlock is going to manage that in a timely manner?

Quite.

This is why computer security folks look so frustrated

Filed under: Technology — Tags: , , — Nicholas @ 07:41

It’s not that the “security” part of the job is so wearing … it’s that people are morons:

Security white hats, despair: users will run dodgy executables if they are paid as little as one cent.

Even more would allow their computers to become infected by botnet software nasties if the price was increased to five or 10 cents. Offer a whole dollar and you’ll secure a herd of willing internet slaves.

The demoralising findings come from a study lead by Nicolas Christin, research professor at Carnegie Mellon University’s CyLab which baited users with a benign Windows executable sold to users under the guise of contributing to a (fictitious) study.

It was downloaded 1,714 times and 965 users actually ran the code. The application ran a timer simulating an hour’s computational tasks after which a token for payment would be generated.

The researchers collected information on user machines discovering that many of the predominantly US and Indian user machines were already infected with malware despite having security systems installed, and were happy to click past Windows’ User Access Control warning prompts.

The presence of malware actually increased on machines running the latest patches and infosec tools in what was described as an indication of users’ false sense of security.

June 17, 2014

BC supreme court attempts to extend jurisdiction over Google’s global services

Filed under: Cancon, Law, Liberty, Media, Technology — Tags: , , , , , — Nicholas @ 08:10

Michael Geist talks about another court attempting to push local rules into other jurisdictions online — in this case it’s not the European “right to be forgotten” nonsense, it’s unfortunately a Canadian court pulling the stunt:

In the aftermath of the European Court of Justice “right to be forgotten” decision, many asked whether a similar ruling could arise in Canada. While a privacy-related ruling has yet to hit Canada, last week the Supreme Court of British Columbia relied in part on the decision in issuing an unprecedented order requiring Google to remove websites from its global index. The ruling in Equustek Solutions Inc. v. Jack is unusual since its reach extends far beyond Canada. Rather than ordering the company to remove certain links from the search results available through Google.ca, the order intentionally targets the entire database, requiring the company to ensure that no one, anywhere in the world, can see the search results. Note that this differs from the European right to be forgotten ruling, which is limited to Europe.

The implications are enormous since if a Canadian court has the power to limit access to information for the globe, presumably other courts would as well. While the court does not grapple with this possibility, what happens if a Russian court orders Google to remove gay and lesbian sites from its database? Or if Iran orders it remove Israeli sites from the database? The possibilities are endless since local rules of freedom of expression often differ from country to country. Yet the B.C. court adopts the view that it can issue an order with global effect. Its reasoning is very weak, concluding that:

    the injunction would compel Google to take steps in California or the state in which its search engine is controlled, and would not therefore direct that steps be taken around the world. That the effect of the injunction could reach beyond one state is a separate issue.

Unfortunately, it does not engage effectively with this “separate issue.”

« Newer PostsOlder Posts »

Powered by WordPress