Quotulatiousness

November 13, 2021

The unrealistic expectations society has of minimum-wage security guards

Filed under: Business, Cancon, Law, USA — Tags: , , — Nicholas @ 03:00

As a teenager, I worked several months as a security guard. In the 1970s in Ontario, to work as a security guard you basically needed to be physically fit (to a not-very-high standard), to pass a police background check and to be 18 or over. The jobs I worked were usually overnight shifts at upscale apartment buildings, industrial facilities and fill-in shifts at retail malls to cover for regular security staff vacations (plus one really interesting midnight shift on a ship docked in Toronto harbour). I think I was paid $3 per hour, and 99% of the time the work wasn’t worth any more than that. It’s that 1% of situations where the company hiring security guards might wish they’d invested in better-trained staff. According to Joshua Hind‘s article in The Line, the standards for security guards have been improved in the many years since my time, but that 1% is still a big issue:
While some of the best minds in the field of crowd management and event safety weigh in on the probable causes of the crowd surge, a new article in Rolling Stone has turned a spotlight on the security guards, and the culpability of private security in general, a high turnover, low-wage business focused on filling orders with warm bodies, seemingly regardless of their actual experience or competency. In Canada, security work is one of the easiest routes to employment for young people and particularly recent immigrants with little Canadian work experience, but, when it comes to live events, it’s also an often impossible mix of customer support, crowd management, law enforcement, and emergency medical services that requires years of training and on-the-ground experience to do well.

The apparent failures of this type of security, which is often referred to as “contract security” (not be confused with “private security”, which usually means expensive bodyguards), are not unique to Houston. I’ve been working in large public events for more than 20 years and contract security has always been one of the great planning dilemmas. If you want to get insured, you need lots of security, but every one of those guards must be treated as part asset and part liability.

Event sites, especially festivals with multiple stages, are expansive (the site in Houston was over 1,000,000 square feet in total space), and a well-designed event site, just like a well-designed building, needs plenty of entrances and exits, each of which must be adequately staffed. Guards are needed in front of the stage, in the crowd, at backstage access points, and around critical infrastructure. On top of all that you also need a team of roving guards to patrol the site looking for issues. Add it up and a large event site could have dozens or hundreds of security guards doing a variety of jobs, all of which fall under the catch-all description of “security”. On a big summer weekend at the height of event season, a large city like Toronto might have thousands of guards working dozens of sites. How do you find that many good people who can bear the responsibility of preserving public safety? Generally, you don’t.

It only requires a two-week commitment and a little patience to become a security guard in Ontario. So long as you have a clean criminal record, you can sign up for the required training: 40 hours on law and security, plus another 30-40 hours of first aid. This training is often performed by the very companies that do the hiring, which can greatly affect priorities in accurate skills testing. Hit all those marks and mere weeks after deciding to become a security guard you could be faced with a horde of concertgoers busting through the fence you’ve just been ordered to protect.

When I started in live events, it was all on the technical side, setting up lighting, sound and stages, and I didn’t pay much attention to what happened on the other side of the crowd barrier. About 15 years ago I started working on Nuit Blanche, Toronto’s overnight outdoor art event, and it was during those long nights watching hundreds of thousands and then millions of people that I developed a sense of how they act in large groups and how unpredictable they can be. This isn’t meant to sound like a superpower, it’s just a honed instinct. It took me well over a decade of steady work and constant observation to develop some ability to sense when a crowd might turn ugly. That experience can’t be replicated with two weeks of training, but that’s exactly what’s often expected of security guards.
December 28, 2020

Another aircraft that’s about to become a political football in Canada

Filed under: Cancon, Government, Military — Tags: , , , — Nicholas @ 03:00

Ted Campbell discusses the need to replace the Royal Canadian Air Force long-haul VIP transport aircraft (the current CC-150 Polaris planes were built and first operated by Wardair in 1987 and obtained by the government in 1993). It’s traditional for the government to be assailed by the opposition and the media (at least when it’s a Conservative government in office) for wanting to spend far too many dollars for unnecessarily luxurious planes (Jean Chretien in opposition called the Polaris a “flying Taj Mahal”)*. The Polaris and its eventual replacement do a lot more than just fly junketing politicians around:

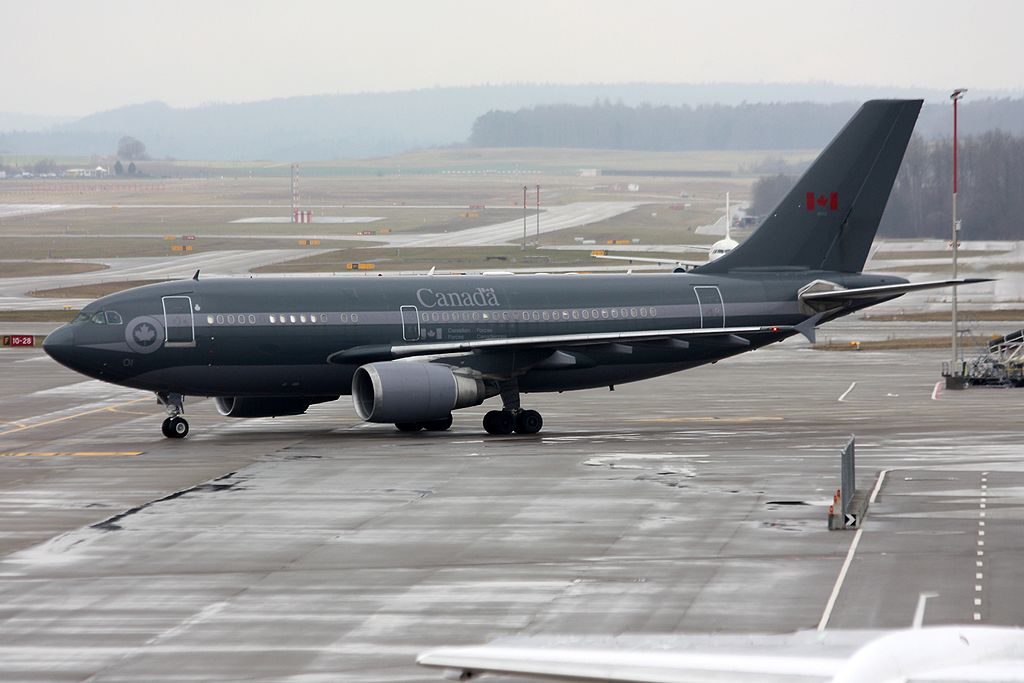
RCAF CC-150 Polaris at Zurich, Switzerland on 25 January, 2012.
Photo by Kambui via Wikimedia Commons

… let’s all remember please that the primary roles of this fleet of aircraft are to transport Canadian troops to wherever in the world they might need to go, for operations, and to refuel our jet fighters when they are deployed overseas, and to carry cargo, but smaller loads that do not require a big CC-130 Hercules or the mighty CC-177 Globemaster III. The Royal Canadian Air Force needs a fleet of specially modified aircraft for those roles. There are several more modern “tankers” available including the Boeing KC-46 which is used by the USA and Israel and the Airbus A330 Multi Role Tanker Transport (MRTT) which is used by several nations including Australia and the United Kingdom. […] Some commercial aircraft can be converted, easily and quickly, from carrying passengers in seats to carrying cargo in containers to carrying aircraft fuel in giant bladders with refuelling hoses attached. They are true multi-role aircraft. They can also be converted to VIP aircraft with special suites for sleeping, with showers, work spaces, secure telecommunications and regular conventional passenger seats for support staff and journalists.

The key bit of a real VIP aircraft is a secure (high-grade encryption) communications and information suite. The prime minister, ministers and senior officials, when en route to a meeting in a foreign capital may need to have discussions that are SECRET-CANADIAN EYES ONLY with senior staff back in Ottawa and they may then need to have a video conference call with, say, the Prime Ministers of e.g. Australia and the United Kingdom using a different security system that allows them to discuss SECRET-FIVE EYES ONLY materiel. You’re talking a reliable satellite communications system (with a back-up, too) and various cryptographic terminals and the people to operate and maintain them. The comm/IT suite is complex and expensive. Everything else is optional and, even in the case of a VIP shower stall, pretty cheap, too.

OK, I can already hear the objections, many from Conservatives: “Why doesn’t he fly commercial? He can even fly First Class,” some will say. Aside from some very real security concerns, suppose he has to attend a G-20 meeting in Brazil. There are no flights from Ottawa, there are no direct flights from Toronto. Even if there were he would need an entourage of security and telecommunications/cryptography specialists. I know the Pope charters an Alitalia jet when he travels but I’m afraid that even Air Canada, which has 400± aircraft and carries over 50,000,000 passengers a year, might find it too difficult to keep an aircraft on something close to “hot-standby,” as the RCAF does, for the prime minister. This problem was examined many times over the years and the range of factors ~ security, communications, availability ~ dictate that a dedicated VIP squadron in the Air Force is the best choice … maybe the only sensible choice.

* I rarely say much in favour of former PM Jean Chrétien, but in this particular case he was consistent in his opposition even after being elected: he refused to use the VIP transport during his time in office and attempted to find a buyer for that particular aircraft. Successor Paul Martin had no such aversion and used the aircraft during his premiership.

December 17, 2019

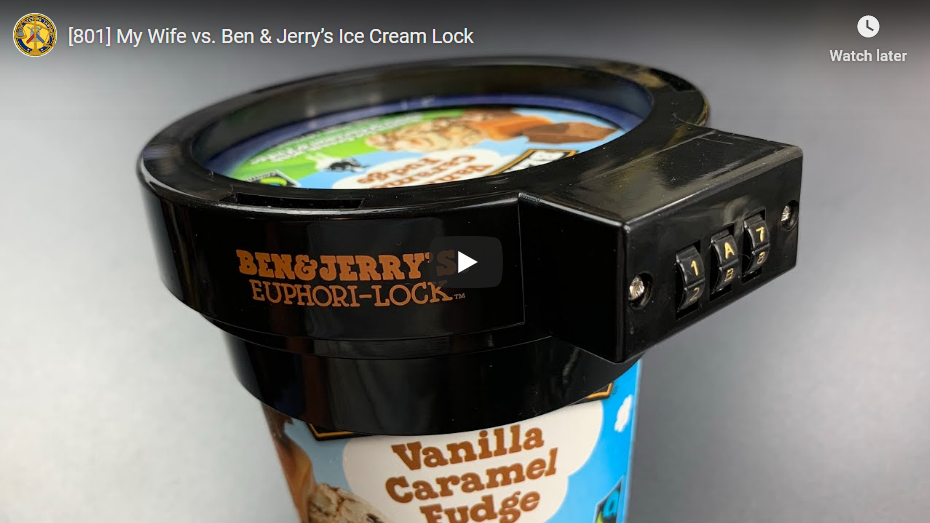
My Wife vs. Ben & Jerry’s Ice Cream Lock

Filed under: Food, Humour, Randomness — Tags: — Nicholas @ 02:00

LockPickingLawyer
Published 15 Dec 2018

From the comments:

Hacker Lord
4 months ago
He sounds so calm for someone who’s probably sleeping on the couch tonight lol

August 30, 2019

EFF sues Homeland Security over illegal GPS vehicle trackers

Filed under: Government, Law, Liberty, USA — Tags: , , , , — Nicholas @ 03:00

Kieren McCarthy on a recent lawsuit by the Electronic Frontiers Foundation:

The Electronic Frontier Foundation (EFF) has sued the US Department of Homeland Security to find out more about a program where, it is claimed, officers secretly stick GPS trackers on vehicles they are suspicious of as they come through the border.

The EFF has made repeated freedom of information act (FoIA) requests about the program’s policies but has been stonewalled, with Homeland Security’s responses claiming any information would contain “sensitive information” that could lead to “circumvention of the law.”

The foundation’s main concern is that Homeland Security is carrying out its secret tracking without a warrant, or even anything beyond a single officer’s suspicion. And it points to a recent US Supreme Court decision where it ruled that warrantless GPS tracking was unconstitutional under the Fourth Amendment.

Details of the program came to light last year when customs officers revealed in court filings that they had used GPS trackers without a warrant at the border. Since then the EFF has tried to find out what the policies and procedures are for deciding when a vehicle can be tagged. The relevant authorities have not been keen to go into any detail.

There’s another legal precedent too: a California court ruled that government officials’ use of GPS devices to track two suspected drug dealers without getting a warrant violated the Supreme Court decision, made in 2012, and was government misconduct.

June 8, 2019

Differentiating between actual security and security theatre

Filed under: Britain, Humour, Liberty, Technology — Tags: , — Nicholas @ 03:00

Alistair Dabbs has a security tale of woe:

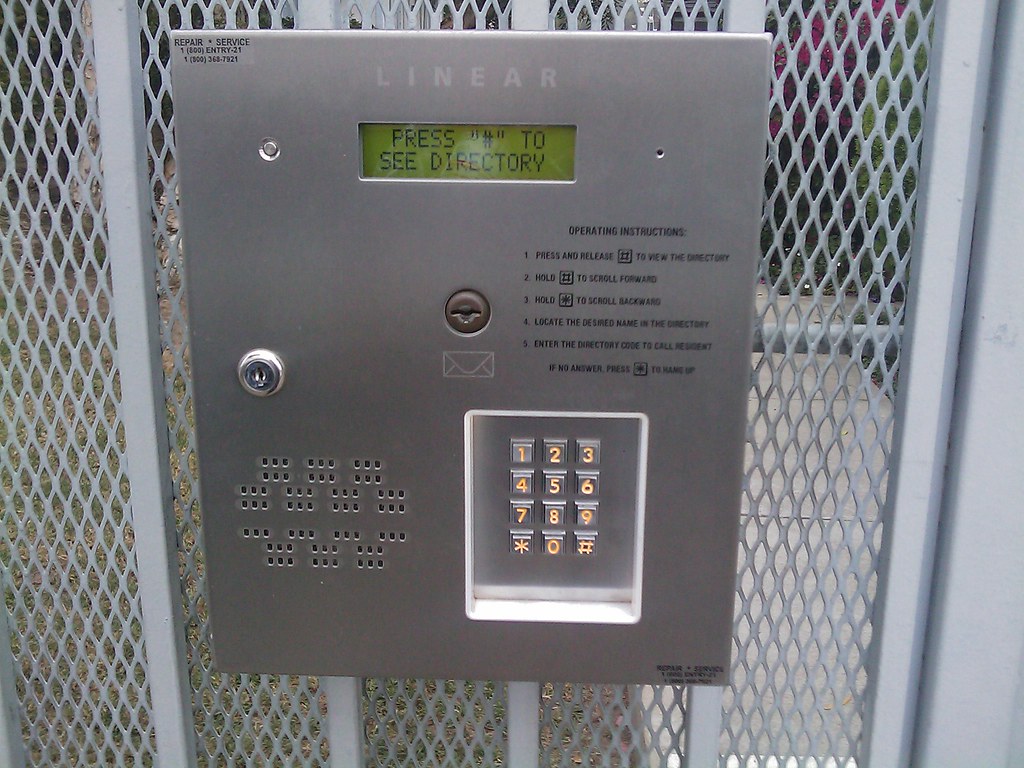
“Keypad Entry”by Victor Frost is licensed under CC BY-NC-SA 2.0

Access denied. Enter Access Code.

That’s a good start. Just a few moments ago I was handed a card on which is written, in blue ballpoint, a newly compiled string of alphanumerics that is supposed to identify me as a unique user. Oh well, maybe I fumbled the buttons. Let’s try again.

Access denied. Enter Access Code.

I am standing in the driving rain – this is London in the summer – in front of a large electronically operated vehicle barrier that keeps the riff-raff from getting anywhere near the car park and loading bay behind the building where I am to be working this week.

The vertical stainless steel keypad into which I am pushing my access code is weather-resistant. I am not. You’d think they could have installed the keypad at car-window level but no, it’s at lorry level. And it’s not on the driver’s side anyway, so anyone not rolling up in an unmodified US or continental import vehicle is forced to exit and walk over to the access terminal.

Access denied. Enter Access Code.

As far as it is concerned, I am riff-raff. I look behind me to see a steel-grey car has pulled up behind mine. Steel-grey = bland, unimaginative, company car, must be management. As I trudge back towards the street entrance around the corner to ask the security desk for an alternative access code, remembering this time to express an explicit preference for one that actually provides access, I notice the driver in the grey car has started to harrumph.

Security systems like this exist to protect me and my possessions, whether physical or electronic. They keep out the nasties and foil the mischievous. They allow access to the honest and prevent it to the unauthorised.

They are a pain in the arse.

Security is essential, of course, but only for other people. Not me. I’m the nice guy here and this sodding keypad is stopping me from getting in.

But then security authentication is one of those functions whose philosophical concept is hampered by self-contradictory details of its own design. To pick a topical example, it is the right of European Union citizens to enjoy free movement between EU countries without being stopped by border controls. However, how can the border controls know whether you are an EU citizen or not unless they stop you to ask for your EU identification? So it’s only by presenting your passport or ID card that you can exercise your right not to have to present your passport or ID card.

The forces of law and order, from police to night club bouncers, face the same recursive logic. Why do they insist on frisking me? Why can’t they concentrate their stop and search efforts only on those who are carrying concealed weapons?

May 8, 2019

Your electronic devices and the Canadian Border Services Agency

Filed under: Cancon, Law, Liberty, Technology — Tags: , , , , , , — Nicholas @ 03:00

A few years ago, many civil libertarians were upset that the US government allowed warrantless searches of electronic devices at the border, but it was less well known that the Canadian Border Services Agency does the same at the Canadian border:

According to the CBSA, it has the right to search electronic devices at the border for evidence of customs-related offences — without a warrant — just as it does with luggage.

If travellers refuse to provide their passwords, officers can seize their devices.

The CBSA said that between November 2017 and March 2019, 19,515 travellers had their digital devices examined, which represents 0.015 per cent of all cross-border travellers during that period.

During 38 per cent of those searches, officers uncovered evidence of a customs-related offence — which can include possessing prohibited material or undeclared goods, and money laundering, said the agency.

While the laws governing CBSA searches have existed for decades, applying them to digital devices has sparked concern in an era where many travellers carry smartphones full of personal and sometimes very sensitive data.

A growing number of lawyers across Canada argue that warrantless digital device searches at the border are unconstitutional, and the practice should be stopped or at least limited.

“The policy of the CBSA of searching devices isn’t something that is justifiable in a free and democratic society,” said Wright who ran as a Green Party candidate in the 2015 federal election.

“It’s appalling, it’s shocking, and I hope that government, government agencies and the courts, and individual citizens will inform themselves and take action.”

January 4, 2019

SplashData’s Top 100 Worst Passwords of 2018

Filed under: Humour, Technology — Tags: , , — Nicholas @ 02:00

SplashData's Top 100 Worst Passwords of 2018 from John Hall on Vimeo.

December 7, 2018

Australian parliament votes to weaken encryption

Filed under: Australia, Government, Law, Liberty, Technology — Tags: , , — Nicholas @ 03:00

Scott Shackford reports on the latest bit of oddness from the southern hemisphere:

Pretty much every single person in the tech industry, human rights circles, and academia warned the Australian government that forcing online platforms to weaken encryption would lead to disastrous results. Nonetheless, lawmakers are pushing forward — and it’s not just Australians who will suffer as a result.

Last night, Australia’s parliament rushed through the Assistance and Access Bill of 2018 right as their session was coming to a close. The bill gives various government agencies the authority to demand that tech and communication platforms provide them secret bypass routes around encrypted messages.

This is what is known as an encryption “backdoor,” and it’s a bad idea. Governments insist such tools are needed to fight crime and terrorism. The problem is that an encryption backdoor doesn’t care who uses it: If there’s a mechanism to bypass privacy security on a communication system, it can be exploited by anybody who knows how. That includes hackers, thieves, officials from authoritarian governments, and all sorts of dangerous people (including, of course, the very government people who insist they’re trying to protect us). That’s why tech companies have spent years fighting against the idea.

Weak encryption is a threat to the health of any tech platform that involves transferring data, and governments know that. So they insist they’re not demanding encryption backdoors while attempting to enact policies that pretty much demand them.

The Assistance and Access Bill won’t just grant the Australian government the power to demand that everybody from Facebook to Whatsapp help them bypass security to access private communications. The bill will let officials order companies, through “technical capability notices,” to alter their programming to facilitate snooping. And it gives the government the authority to force the tech employees who implement the changes to keep them secret. Break that secrecy, and the employees can face up to five years in jail.

November 10, 2018

Don’t expect the “Internet-of-Things” to get better security without Uncle Sam’s pressure

Filed under: Business, Government, Technology — Tags: , — Nicholas @ 05:00

Bruce Schneier believes it will take government action (or as The Register phrased it, “Uncle Sam … putting boots to asses”) to get any significant improvement in Internet-of-Shit device security:

Any sort of lasting security standard in IoT devices may only happen if governments start doling out stiff penalties.

So said author and computer security guru Bruce Schneier, who argued during a panel discussion at the Aspen Cyber Summit this week that without regulation, there is little hope the companies hooking their products up to the internet will implement proper security protections.

“Looking at every other industry, we don’t get security unless it is done by the government,” Schneier said.

“I challenge you to find an industry in the last 100 years that has improved security without being told [to do so] by the government.”

Schneier went on to point out that, as it stands, companies have little reason to implement safeguards into their products, while consumers aren’t interested in reading up about appliance vendors’ security policies.

“I don’t think it is going to be the market,” Schneier argued. “I don’t think people are going to say I’m going to choose my refrigerator based on the number of unwanted features that are in the device.”

Schneier is not alone in his assessment either. Fellow panellist Johnson & Johnson CISO Marene Allison noted that manufacturers have nothing akin to a bill of materials for their IP stacks, so even if customers want to know how their products and data are secured, they’re left in the dark.

“Most of the stuff out there, even as a security professional, I have to ask myself, what do they mean?” Allison said.

September 20, 2018

Mind Your Business Ep. 3: Public Safety from Private Security

Filed under: Business, Law, Liberty, USA — Tags: , , — Nicholas @ 06:00

Foundation for Economic Education
Published on 18 Sep 2018

In Detroit, dependence on law enforcement has proved insufficient to keep people safe. Enter Dale Brown, a threat management professional who specializes in stopping violence and empowering individuals to protect themselves and their loved ones.

September 11, 2018

Fear the Internet-of-Things

Filed under: Business, Technology — Tags: , , , — Nicholas @ 05:00

Martin Giles talks to Bruce Schneier about his new book, Click Here to Kill Everybody:

The title of your book seems deliberately alarmist. Is that just an attempt to juice sales?

It may sound like publishing clickbait, but I’m trying to make the point that the internet now affects the world in a direct physical manner, and that changes everything. It’s no longer about risks to data, but about risks to life and property. And the title really points out that there’s physical danger here, and that things are different than they were just five years ago.

How’s this shift changing our notion of cybersecurity?

Our cars, our medical devices, our household appliances are all now computers with things attached to them. Your refrigerator is a computer that keeps things cold, and a microwave oven is a computer that makes things hot. And your car is a computer with four wheels and an engine. Computers are no longer just a screen we turn on and look at, and that’s the big change. What was computer security, its own separate realm, is now everything security.

You’ve come up with a new term, “Internet+,” to encapsulate this shift. But we already have the phrase “internet of things” to describe it, don’t we?

I hated having to create another buzzword, because there are already too many of them. But the internet of things is too narrow. It refers to the connected appliances, thermostats, and other gadgets. That’s just a part of what we’re talking about here. It’s really the internet of things plus the computers plus the services plus the large databases being built plus the internet companies plus us. I just shortened all this to “Internet+.”

Let’s focus on the “us” part of that equation. You say in the book that we’re becoming “virtual cyborgs.” What do you mean by that?

We’re already intimately tied to devices like our phones, which we look at many times a day, and search engines, which are kind of like our online brains. Our power system, our transportation network, our communications systems, are all on the internet. If it goes down, to a very real extent society grinds to a halt, because we’re so dependent on it at every level. Computers aren’t yet widely embedded in our bodies, but they’re deeply embedded in our lives.

Can’t we just unplug ourselves somewhat to limit the risks?

That’s getting harder and harder to do. I tried to buy a car that wasn’t connected to the internet, and I failed. It’s not that there were no cars available like this, but the ones in the range I wanted all came with an internet connection. Even if it could be turned off, there was no guarantee hackers couldn’t turn it back on remotely.

Hackers can also exploit security vulnerabilities in one kind of device to attack others, right?

There are lots of examples of this. The Mirai botnet exploited vulnerabilities in home devices like DVRs and webcams. These things were taken over by hackers and used to launch an attack on a domain-name server, which then knocked a bunch of popular websites offline. The hackers who attacked Target got into the retailer’s payment network through a vulnerability in the IT systems of a contractor working on some of its stores.

July 24, 2018

QotD: Passwords

Filed under: Quotations, Technology — Tags: , — Nicholas @ 01:00

It makes no sense to force users to generate passwords for websites they only log in to once or twice a year. Users realize this: they store those passwords in their browsers, or they never even bother trying to remember them, using the “I forgot my password” link as a way to bypass the system completely — ­effectively falling back on the security of their e-mail account.

Bruce Schneier, “Security Design: Stop Trying to Fix the User”, Schneier on Security, 2016-10-03.

June 27, 2018

Canada’s euphemistically named “High Risk Returnees”

Filed under: Cancon, Middle East, Politics, Religion — Tags: , , , , , , — Nicholas @ 05:00

Judith Bergman on the Canadian government’s kid-gloves approach to dealing with Canadian citizens who return to Canada after volunteering to serve with terrorist organizations:

Canadians who go abroad to commit terrorism – predominantly jihadists, in other words – have a “right to return” according to government documents obtained by Global News. They not only have a right of return, but “… even if a Canadian engaged in terrorist activity abroad, the government must facilitate their return to Canada,” as one document says.

According to the government, there are still around 190 Canadian citizens volunteering as terrorists abroad. The majority are in Syria and Iraq, and 60 have returned. Police are reportedly expecting a new influx of returnees over the next couple of months.

The Canadian government is willing to go to great (and presumably costly) lengths to “facilitate” the return of Canadian jihadists, unlike the UK, for example, which has revoked the citizenship of ISIS fighters so they cannot return. The Canadian government has established a taskforce, the High Risk Returnee Interdepartmental Taskforce, that, according to government documents:

    “… allows us to collectively identify what measures can mitigate the threat these individuals may pose during their return to Canada. This could include sending officers overseas to collect evidence before they depart, or their detention by police upon arrival in Canada.”

Undercover officers may also be used “to engage with the HRT [High Risk Traveler] to collect evidence, or monitor them during their flight home.”

In the sanitizing Orwellian newspeak employed by the Canadian government, the terrorists are not jihadis who left Canada to commit the most heinous crimes, such as torture, rape and murder, while fighting for ISIS in Syria and Iraq, but “High Risk Travelers” and “High Risk Returnees”.

The government is fully aware of the security risk to which it is subjecting Canadians: According to the documents, “HRRs [High Risk Returnees] can pose a significant threat to the national security of Canada”. This fact raises the question of why the government of Canada is keen to facilitate these people’s “right of return” — when presumably the primary obligation of the government is to safeguard the security of law-abiding Canadian citizens.

June 5, 2018

The Internet-of-Things as “Moore’s Revenge”

Filed under: Technology — Tags: , , , — Nicholas @ 03:00

El Reg‘s Mark Pesce on the end of Moore’s Law and the start of Moore’s Revenge:

… the cost of making a device “smart” – whether that means, aware, intelligent, connected, or something else altogether – is now trivial. We’re therefore quickly transitioning from the Death of Moore’s Law into the era of Moore’s Revenge – where pretty much every manufactured object has a chip in it.

This is going to change the whole world, and it’s going to begin with a fundamental reorientation of IT, away from the “pinnacle” desktops and servers, toward the “smart dust” everywhere in the world: collecting data, providing services – and offering up a near infinity of attack surfaces. Dumb is often harder to hack than smart, but – as we saw last month in the Z-Wave attack that impacted hundreds of millions of devices – once you’ve got a way in, enormous damage can result.

The focus on security will produce new costs for businesses – and it will be on IT to ensure those costs don’t exceed the benefits of this massively chipped-and-connected world. It’ll be a close-run thing.

It’s also likely to be a world where nothing works precisely as planned. With so much autonomy embedded in our environment, the likelihood of unintended consequences amplifying into something unexpected becomes nearly guaranteed.

We may think the world is weird today, but once hundreds of billions of marginally intelligent and minimally autonomous systems start to have a go, that weirdness will begin to arc upwards exponentially.

May 5, 2018

Passwords, again

Filed under: Technology — Tags: , — Nicholas @ 03:00

At The Register, a meditation on passwords by Kieren McCarthy:

“It’s World #PasswordDay! A reminder to change your pins/passwords frequently,” it advised anyone following the hashtag “PasswordDay”. But this, as lots of people quickly pointed out, is terrible advice.

But hang on a second: isn’t that the correct advice? Weren’t all sysadmins basically forced to change their systems to make people reset passwords every few months because it was better for security?

Yes, but that was way back in 2014. Starting late 2015, there was a big push from government departments across the world – ranging from UK spy agency GCHQ to US standard-setting National Institute of Standards and Technology (NIST) and consumer agency the Federal Trade Commission (FTC) – to not do that.

That said, the past few years has been virtually defined by the loss of billions of usernames and passwords from corporations, ranging from your email provider, to your credit agency, home improvement store, retail store and, yes, even government departments.

In that case, does it not in fact make sense to get people to periodically change their passwords? Well, yes. And no.

Yes, because the information would age and so become irrelevant faster. No, because constant resets eat up resources, tend to nudge people toward using simpler passwords, and don’t really make it harder for some miscreant using a brute force attack to guess the password.

[…]

Random or pronounceable?

Everyone agrees that using the word “password” for a password is pretty much the dumbest thing you can do. But so many people still do it that designers have been forced to hardcode a ban on the word into most password systems.

But from there – where do you go? How much better is “password1”? Is it sufficiently better? What about switching letters to other things, like “p@ssw0rd”? Yes, objectively, that is better. But the point is that there are much better ways. And that comes down to basically two choices: random or pronounceable.

The best random password is one that really is random i.e. not a weird spelling that you quickly forget but a combination of letters, numbers and symbols like “4&bqJv8dZrXgp” that you would simply never be able to remember.

But here’s the thing – the reason that particular password is better is largely because in order to use and generate such passwords, you would likely use a password manager. And password managers are great things that we’ll deal with later.

But here’s the thing: if someone is trying to crack your password randomly they are likely to be using automated software that simply fires thousands of possible passwords at a system until it hits the right one.

In that scenario, it is not the gibberish that is important but the length of the password that matters. Computers don’t care if a password is made up of English words – or words of any language. But the longer it is, the more guesses will be needed to get it right.

As our dear truthsayer XKCD points out: “Through 20 years of effort we’ve successfully trained everyone to use passwords that are hard for humans to remember, but easy for computers to guess.”

« Newer Posts — Older Posts »

Powered by WordPress